
Cofense Details Meta-Themed Phishing Campaign That Captures Passwords and Live 2FA Codes
Summary
Cofense describes a Meta-impersonating phishing campaign that routes victims through Google Forms to a Vercel-hosted page, harvesting passwords and live 2FA tokens for near-immediate account access.
Key points
- Cofense’s Phishing Defense Center identified a campaign impersonating Meta’s verification process and targeting individuals and businesses.
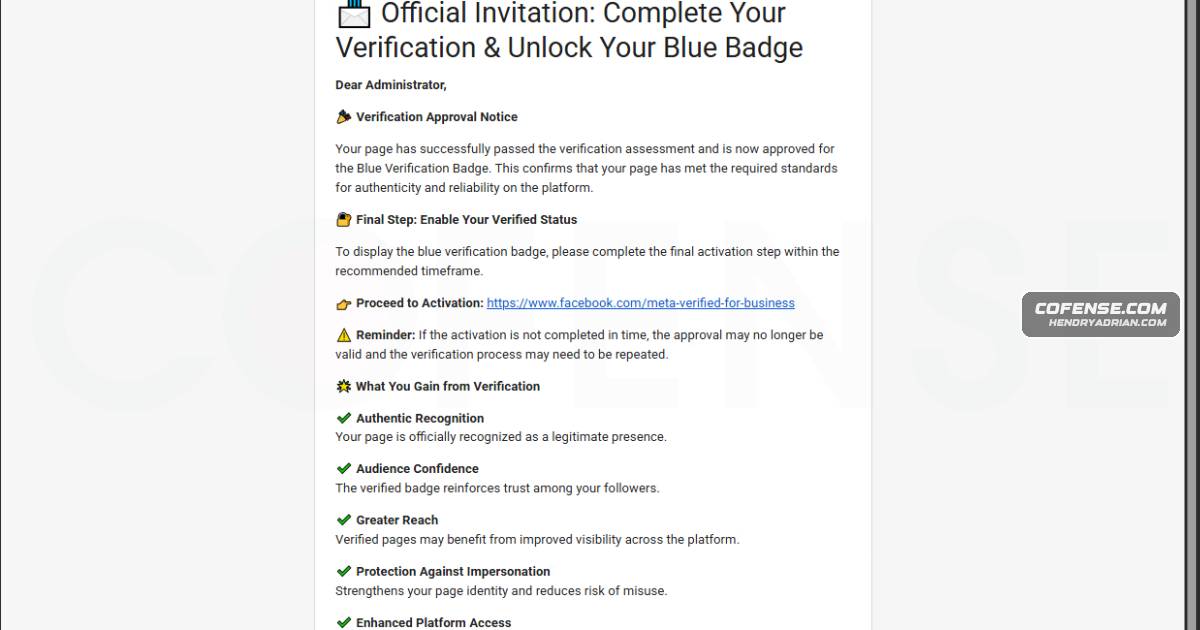
- The emails use a Gmail sender display name of “Meta Verified” and claim account verification has been approved.
- Recipients are directed through a Google Form to a Meta-styled phishing page hosted at verifybadge-trustix[.]vercel[.]app/privacy-center.
- The flow collects personal details and passwords, then prompts victims to enter a live 2FA token.
- Cofense reports that credentials and tokens are captured in real time and used to attempt near-immediate account access; the article provides no named victim or independent confirmation of a specific account takeover.
- The article identifies the mismatch between Meta branding and the vercel.app host as an indicator users can check.
Article Details
- Event Type
- Phishing campaign impersonating Meta’s verification process to steal credentials and 2FA tokens.
- Impact
- The campaign captures passwords and live 2FA tokens, which are reportedly used almost immediately to access and take over victims’ accounts and potentially steal sensitive information.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| URL | hxxps[:]//forms[.]gle/cV8Fbu9eNgHpdY1dA | Stage 1 phishing URL redirecting recipients to a Google Form used to begin credential collection. |
| URL | hxxps[:]//verifybadge-trustix[.]vercel[.]app/privacy-center | Stage 2 phishing landing page hosted on vercel.app and identified as impersonating Meta’s privacy/verification center. |
MITRE ATT&CK
T1078 · Valid AccountsThe article reports that captured credentials and live 2FA tokens are used to log into victims’ accounts.T1204.002 · Malicious FileThe credential collection flow begins when a recipient clicks the embedded phishing link.T1566.002 · Spearphishing LinkThe phishing email contains a link that redirects recipients to a Google Form for credential harvesting.T1566.003 · Spearphishing via ServiceThe campaign abuses Google Forms and a hosted landing page to present convincing phishing content.T1583.004 · ServerThe campaign uses a vercel.app-hosted phishing page; the article describes web services as infrastructure used to host phishing pages.
Vendors
Products
Google formsA phishing campaign impersonating Meta uses a Gmail sender display name and Google Forms to harvest login credentials and capture 2FA tokens in real time.Meta VerifiedAttackers use a Gmail account with the display name “Meta Verified” and an email claiming account verification to lure victims.