
Hudson Rock Links Coinbase Cartel Victims to Infostealer-Harvested Credentials
Summary
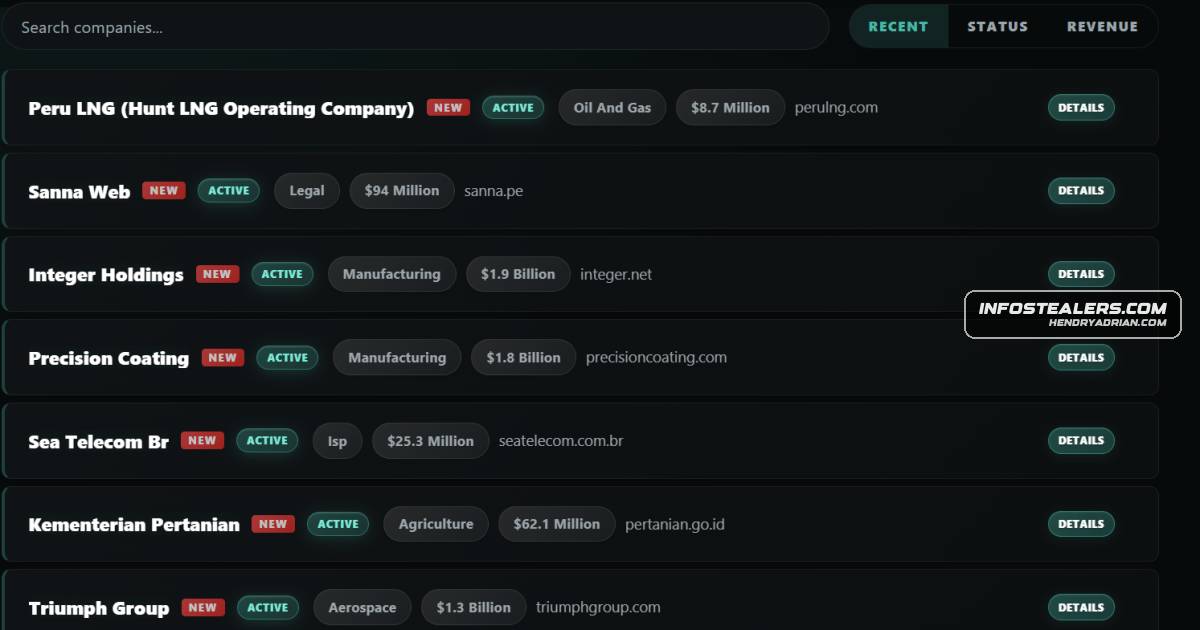
Hudson Rock says its analysis linked about 80% of 164 Coinbase Cartel victims to prior infostealer infections. The group is described as using old credentials to access cloud and file-sharing services for data theft and extortion.
Key points
- Coinbase Cartel has claimed more than 100 targets and is described in the article as an extortion group that steals data rather than encrypting files.
- Hudson Rock and Ransomware.live reportedly compared 164 victim records with Hudson Rock’s Cavalier database; about 80% were linked to prior infostealer infections.
- The article names RedLine, Lumma, and Vidar as infostealers associated with credential theft.
- Hudson Rock says credentials found in infostealer logs were used to access cloud, FTP, and file-sharing services, sometimes years after they were exposed.
- The article gives five victim examples, including Aptim, Canada Goose, Efficy, The Epoch Times, and RAKS; the claimed links and incidents are presented through Hudson Rock’s analysis and cartel listings.
- The article says organizations with many employees affected by infostealers may struggle to identify which exposed credential was used.
Article Details
- Attack Vectors
- Coinbase Cartel reportedly uses old employee or contractor credentials harvested by infostealers to access corporate cloud, FTP, and file-sharing services.
- The group exfiltrates sensitive corporate data and extorts victims without encrypting their files.
- Defensive Notes
- Change exposed credentials; the article warns that infostealer logs may remain useful until credentials are changed, even years after infection.
- Review historical infostealer exposure and employee credential logs when investigating breaches; the article says numerous exposed accounts can make it difficult to identify which credential was used.
MITRE ATT&CK
Threat Actors
Malware
Lummashows the cartel predominantly gains access using old Infostealerâharvested credentials (e.g., RedLine, Lumma, Vidar) to compromise cloud, FTP, and fileâsharing services, complicating attribution and remediation.RedLineshows the cartel predominantly gains access using old Infostealerâharvested credentials (e.g., RedLine, Lumma, Vidar) to compromise cloud, FTP, and fileâsharing services, complicating attribution andVidarcartel predominantly gains access using old Infostealerâharvested credentials (e.g., RedLine, Lumma, Vidar) to compromise cloud, FTP, and fileâsharing services, complicating attribution and remediation.
Vendors
Products
Industries
Architecture and engineeringAptim, a major architecture and engineering firm, was breached and actively leaked by the cartel.business servicesEfficy, a prominent business services provider, saw 43GB of their data leaked.FashionGlobal fashion brand Canada Goose suffered a significant data leak.HealthcareHigh-revenue organizations in healthcare, technology, and transportation are primary targets due to regulatory and reputational exposure.ManufacturingManufacturing / TechMediaMedia organizations are not immune. The Epoch Times was successfully targeted, with their exposed credentials heavily documented in our historical records.TechnologyHigh-revenue organizations in healthcare, technology, and transportation are primary targets due to regulatory and reputational exposure.TransportationHigh-revenue organizations in healthcare, technology, and transportation are primary targets due to regulatory and reputational exposure.