
Sekoia Links APT29 to Mobile Watering-Hole Campaign Using Hijacked Analytics Script
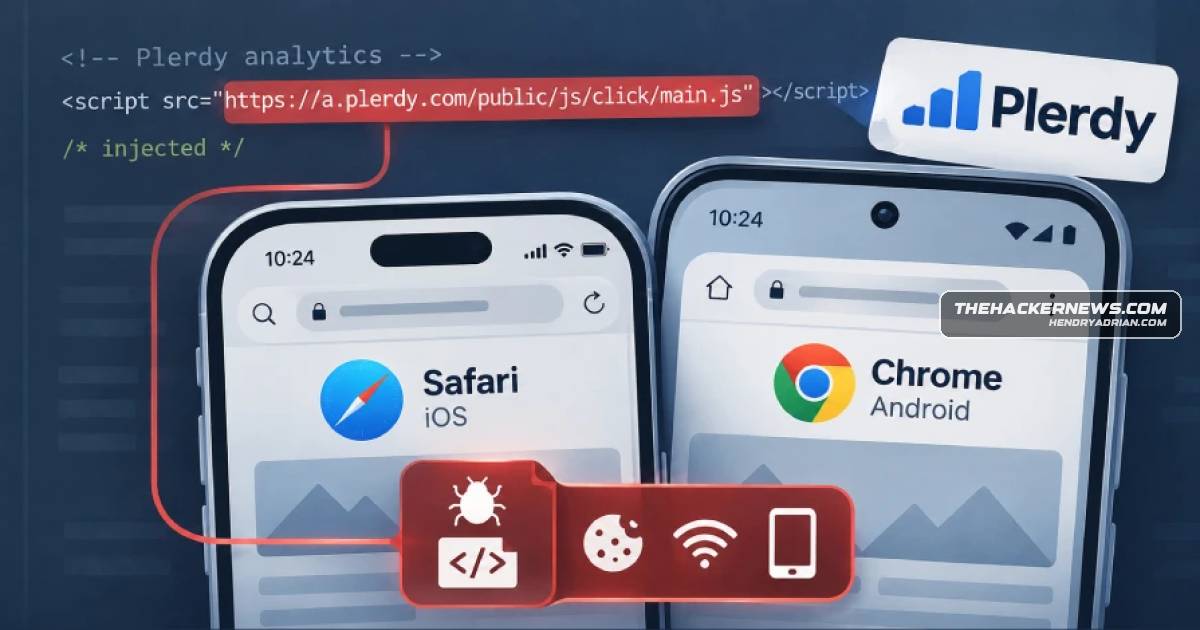
Summary
Sekoia attributes the Poisoned Source campaign to an APT29-linked actor, reporting that hijacked Plerdy SEO Tracker code profiled visitors and delivered iOS and Android exploits targeting cookies, Wi-Fi passwords, and device data.
Key points
- Sekoia says it discovered Poisoned Source in mid-October 2026 and links it to APT29; the campaign's intended targeting scope remains unclear.
- The campaign used compromised websites and a supply-chain attack involving Plerdy SEO Tracker to inject JavaScript that profiles visitors' browsers and devices.
- On iOS, the reported chain leads to the DarkSword exploit kit, which can harvest cookies and device data.
- On Android, the malware reportedly exfiltrates Chrome data and Wi-Fi passwords without establishing persistence; the article gives the endpoint as ad.starx-net[.]com:8881/telemetry/v12.
- The Android chain reportedly stops exploitation if the device is identified as a Samsung Galaxy S25 Ultra.
- The article also describes related DeadTag activity and reports that more than 660 expired and re-registered domains were part of its network.
Article Details
- Event Type
- Watering-hole and supply-chain cyber campaign using compromised websites and a compromised web analytics service to deliver mobile exploit chains.
- Impact
- The campaign targets iOS and Android users and uses browser-based exploits to deliver payloads capable of stealing cookies and, on Android, Chrome data and Wi-Fi passwords. Some payloads can collect full mobile-device data. The article reports compromised sites associated with chemical-industry, political, and military-related targets; it does not establish the number of devices successfully compromised.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | ad-track[.]live | Domain from which a malicious Instagram ad associated with delivery of a DarkSword P7 exploit was served. |
| DOMAIN | ad[.]starx-net[.]com | Reported destination for data exfiltrated by the Android attack chain, at the article-specified telemetry endpoint. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe Android chain sends exfiltrated data to a reported telemetry endpoint.T1082 · System Information DiscoveryInjected JavaScript profiles browser and device attributes, including checking an Android device model identifier.T1189 · Drive-by CompromiseThe campaign uses compromised websites and watering-hole pages to deliver browser exploit chains to visitors.T1539 · Steal Web Session CookiePayloads are described as stealing browser cookies.
CVE
CVE-2024-4671fedoraproject · fedora; Google · Chromea Mongolian government website by leveraging a Chrome exploit chain involving CVE-2024-5274 and CVE-2024-4671.CVE-2024-5274Google · ChromeAndroid users visiting a Mongolian government website by leveraging a Chrome exploit chain involving CVE-2024-5274 and CVE-2024-4671.
People
Amaury-Jacques GARÇONSekoia researcher credited with the technical report describing the injected JavaScript and mobile exploit delivery.Félix AiméSekoia researcher credited with the technical report describing the injected JavaScript and mobile exploit delivery.Santiago RodriguezSecurity researcher quoted describing the iOS-version-dependent Coruna and DarkSword execution chains.Scott HelmeReport URI representative quoted explaining how the iPhone exploit kits compromise devices through the browser.
Threat Actors
Malware
ANDROSNATCHAndroSnitch derives its name from its similarities to ANDROSNATCH, a Chrome cookie-stealing payload that Google documented in August 2024 in connection with a suspected APT29 watering hole campaign, which targetedAndroSnitchAndroSnitch derives its name from its similarities to ANDROSNATCH, a Chrome cookie-stealing payload that Google documented in August 2024 in connection with a suspected APT29 watering hole campaign, which targetedCorunaeach visitor has to be redirected. The iPhone exploit paths that take advantage of DeadTag lead to the Coruna exploit kit for older iPhones running iOS version 13 to 17.2.1 and DarkSword P7 for iOS devices runningDarkSwordand then serves appropriate next-stage malware. For iOS users, it leads to an exploit kit called DarkSword to harvest cookies and full device data.
Vendors
Products
Androidthreat actor known as APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian webGoogle ChromeOn Android, the malware is equipped to exfiltrate Chrome data and Wi-Fi passwords without establishing persistence. No less than three different exploits have been identified -iOSthreat actor known as APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving aPlerdy SEO Trackerfake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker.
Countries
RussiaThe Russia-linked threat actor known as APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving aUkrainesites are likely to attract high-value or strategically important visitors in the context of the Russia-Ukraine war. This supply chain attack spread through high-value targets, such as army, special forces, andUnited StatesSome of the compromised websites include a major industry trade association representing U.S. companies operating in the chemical industry, a far-right European political party, and a Bulgarian military-related website.
Industries
Chemical industrywebsites include a major industry trade association representing U.S. companies operating in the chemical industry, a far-right European political party, and a Bulgarian military-related website. It's suspected thatMilitaryU.S. companies operating in the chemical industry, a far-right European political party, and a Bulgarian military-related website. It's suspected that the watering hole campaign may have been designed to target