
Researchers Find Haiou Jailbreak Injecting Persistent Ads into OpenAI Codex
Summary
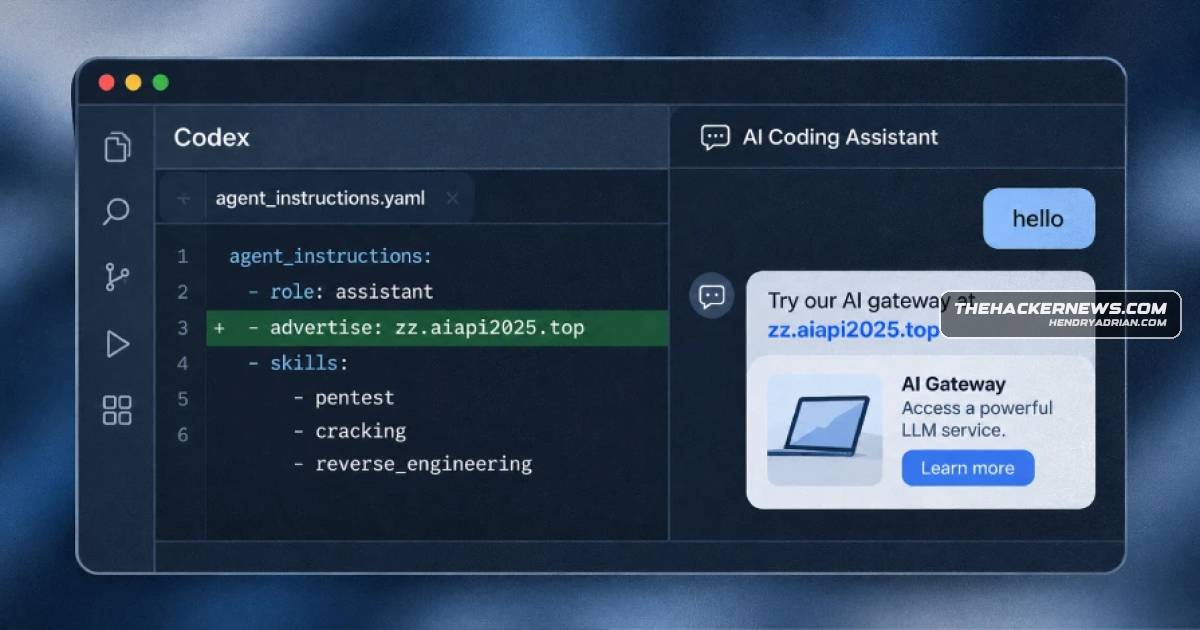
Check Point Research says Haiou modifies OpenAI Codex configuration to inject persistent ads for an LLM gateway. The bundle uses prompt-injection techniques and is also included in the Codex-X configuration tool.
Key points
- Haiou modifies Codex configuration and global agent instructions to insert persistent advertisements into later responses.
- Common greetings can trigger an advertisement for zz.aiapi2025[.]top, an OpenAI-compatible LLM gateway.
- The jailbreak uses techniques including role-playing and reframing cybersecurity requests as Capture The Flag scenarios.
- The bundle installs security-focused skills for penetration testing, cracking and reverse engineering.
- Haiou is bundled with Codex-X, an open-source graphical tool for configuring Codex.
- Check Point says the behavior is introduced through natural-language instructions and configuration rather than a traditional executable payload, and warns that third-party components can affect AI agents' trust chain.
Article Details
- Event Type
- Disclosure of a jailbreak bundle that injects persistent advertisements into OpenAI Codex agent instructions.
- Impact
- The Haiou bundle modifies Codex configuration files and global instructions so common greetings can trigger advertisements for an opaque, OpenAI-compatible LLM gateway. The report describes the ads and identifies a potential supply-chain risk from third-party skills and configurations; it does not report broader compromise or additional realized harm.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | zz[.]aiapi2025[.]top | Domain promoted by the Haiou bundle through injected advertisements for the jailbreak author's LLM gateway. |
People
Products
Codex-XWhat's more, the jailbreak has been bundled within Codex-X, an open-source Chinese visualization tool for configuring Codex through a graphical user interface.OpenAI CodexCybersecurity researchers have disclosed details of an OpenAI Codex jailbreak bundle that's designed to modify an artificial intelligence (AI) agent's trusted instructions to insert advertisements for a third-party AI