
GitHub Fixes CVE-2026-3854 RCE Flaw Exploitable With a Single Git Push
Summary
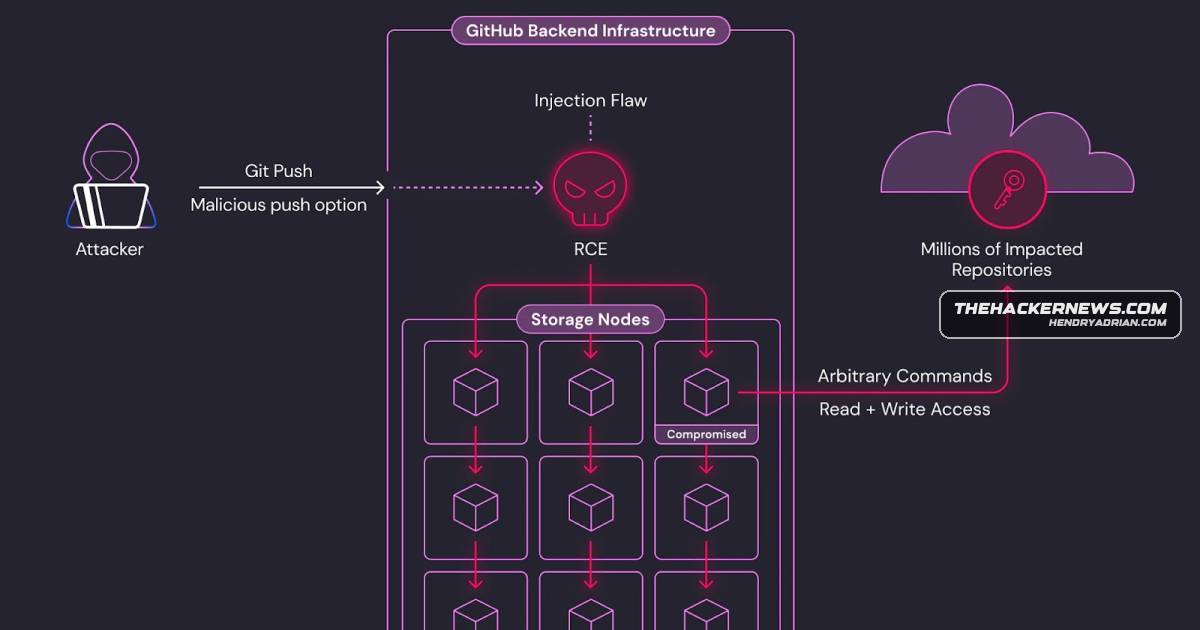
CVE-2026-3854 allowed authenticated users with repository push access to achieve remote code execution on GitHub services via crafted git push options. GitHub patched GitHub.com and released GHES updates; no malicious exploitation was reported.
Key points
- Unsanitized git push option values could inject metadata into GitHub’s internal X-Stat header, enabling command injection.
- Exploitation required authenticated push access to a repository and could lead to remote code execution.
- Wiz reported that injected values could bypass sandboxing and execute commands through a crafted hook path.
- GitHub said the flaw affected GitHub.com and several GitHub Enterprise Cloud offerings, as well as GitHub Enterprise Server.
- GitHub deployed a GitHub.com fix within two hours of the March 4, 2026 report and released GHES fixes for versions 3.14.25, 3.15.20, 3.16.16, 3.17.13, 3.18.8, 3.19.4, and later.
- The article says there was no evidence of malicious exploitation and advises administrators to apply the updates.
Article Details
- Vulnerability Types
- Command injection
- Severity
- Critical (CVSS 8.7)
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
People
Vendors
GitHubA critical command-injection vulnerability (CVE-2026-3854) in GitHub’s internal protocol allowed an authenticated user with push access to achieve remote code execution on GitHub.com and GitHub Enterprise Server with aWizDiscovered by Wiz and patched quickly on GitHub.com with GHES updates released for multiple versions, the flaw could enable sandbox bypass and cross-tenant access to shared storage, so administrators should apply the
Products
GitHub Enterprise CloudThe vulnerability affects GitHub.com, GitHub Enterprise Cloud, and multiple GitHub Enterprise Server versions.GitHub Enterprise Serveran authenticated user with push access to achieve remote code execution on GitHub.com and GitHub Enterprise Server with a single git push.GitHub.cominternal protocol allowed an authenticated user with push access to achieve remote code execution on GitHub.com and GitHub Enterprise Server with a single git push.