
ShinyHunters Claims Theft of 280 Million Records in Instructure Breach
Summary
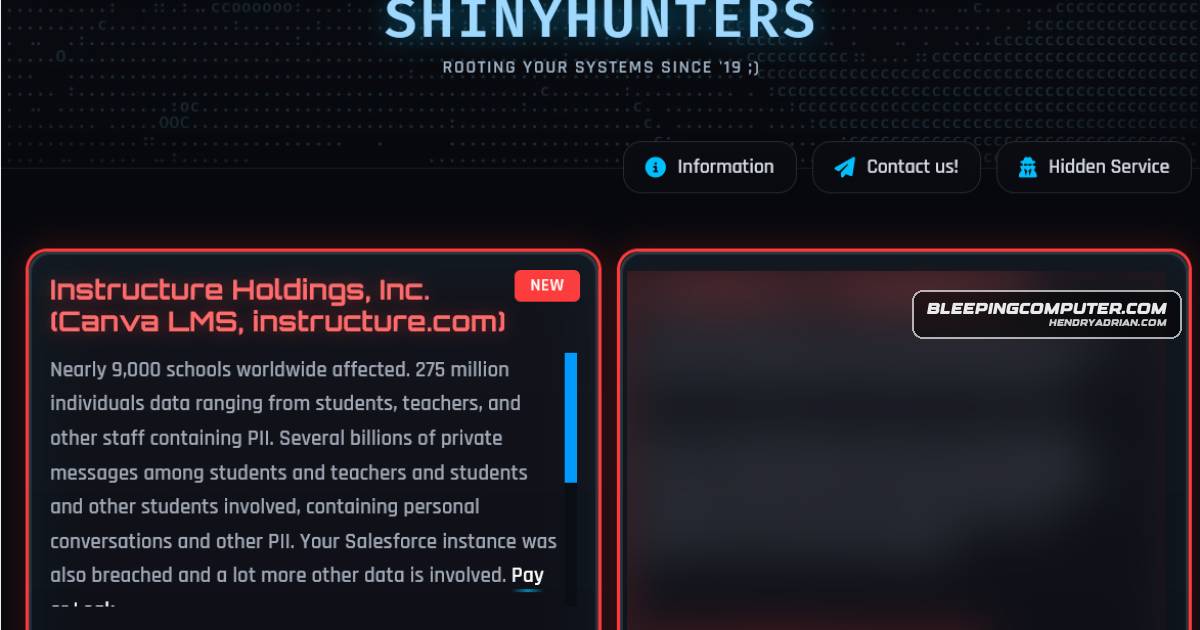
ShinyHunters claims it stole 280 million records from 8,809 education organizations through Canvas export features. Instructure is investigating; the claimed scale and affected institutions have not been independently verified.
Key points
- Instructure disclosed a data breach in which users’ names, email addresses, and private messages were exposed.
- ShinyHunters claims it stole 280 million records associated with students, teachers, and staff across 8,809 education organizations.
- The group says it used Canvas data export features, including DAP queries, provisioning reports, and user APIs.
- The actor published institution-level record counts, but BleepingComputer says it has not independently verified which organizations were affected.
- Instructure is investigating; the University of Colorado Boulder acknowledged the reported nationwide incident, while Rutgers said it had not been notified of a direct impact.
- Tilburg University said it had not confirmed whether its students or staff were affected and was seeking clarification from the supplier.
Article Details
- Victim Organization
- Instructure
- Incident Type
- Cyberattack and data breach; ShinyHunters claims bulk data theft using Canvas export features.
- Data Types Exposed
- Names
- Email addresses
- Private messages
- Enrollment information (claimed by ShinyHunters)
- Affected Records
- ShinyHunters claims 280 million records tied to students and staff across 8,809 institutions; the figures have not been independently verified.
- Affected Data Size
- ShinyHunters claims it harvested hundreds of gigabytes; not independently verified.
- Operational Impact
- Instructure is investigating. Some universities are assessing potential impact. Rutgers reported no direct impact to its campus at the time of its statement and said Canvas remained available and operational.
- Ransom Or Extortion
- ShinyHunters, described as an extortion gang, claimed responsibility and published an institution-level list with record counts on its data leak site. No ransom demand is reported.
- Claim Status
- claimed