
Trellix Confirms Unauthorized Access to Source Code Repository; RansomHouse Claims Attack
Summary
Trellix confirmed unauthorized access to part of its source code repository and is investigating. RansomHouse claimed responsibility and said the intrusion involved encryption, but its screenshots were not verified. Trellix found no evidence its release or distribution
Key points
- Trellix confirmed unauthorized access to part of its source code repository and said it began working with forensic experts.
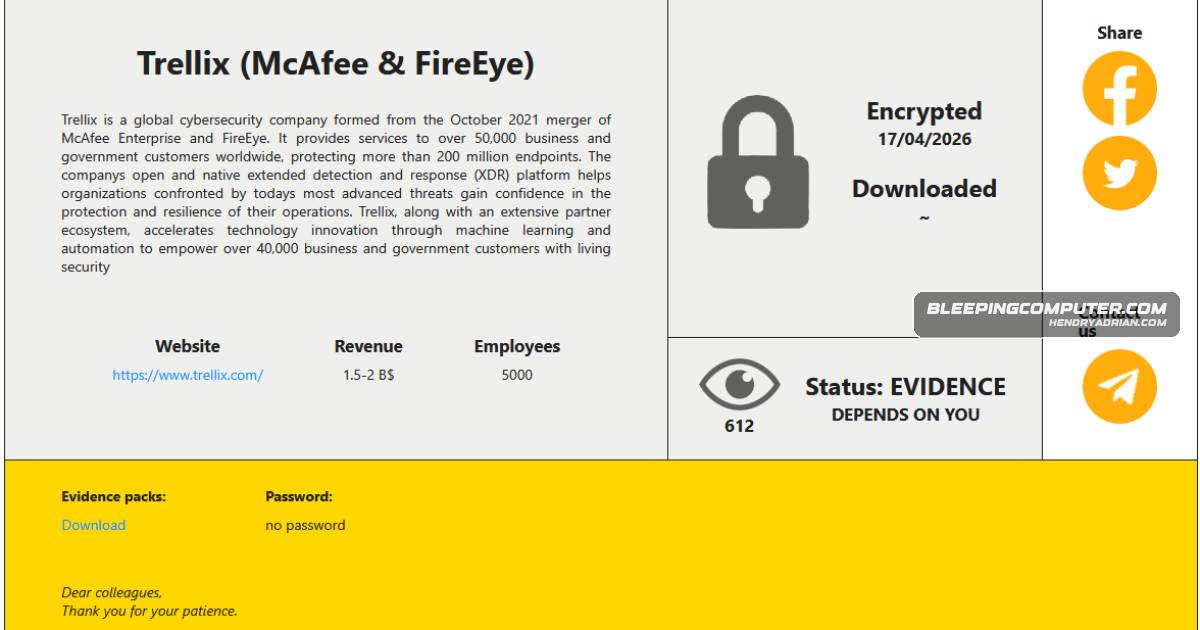
- RansomHouse claimed responsibility and posted screenshots it presented as evidence; BleepingComputer could not confirm their authenticity.
- RansomHouse said the intrusion occurred on April 17 and involved data encryption.
- Trellix notified law enforcement and said it found no evidence that its source code release or distribution process was affected.
- Trellix’s investigation was ongoing, and the company said it would share more details when available.
Article Details
- Victim Organization
- Trellix
- Incident Type
- Unauthorized access to part of Trellix’s source code repository; RansomHouse claimed responsibility and said the intrusion involved data encryption.
- Affected Records
- Not disclosed
- Affected Data Size
- Not disclosed
- Operational Impact
- Trellix confirmed unauthorized access to part of its source code repository and said it was investigating with forensic experts. It reported no evidence that its source code release or distribution process was affected, or that its source code had been exploited.
- Ransom Or Extortion
- RansomHouse claimed responsibility, posted screenshots on its data leak site, and listed Trellix on its extortion portal. The screenshots’ authenticity could not be confirmed by BleepingComputer; no ransom demand or payment was reported.
- Claim Status
- confirmed
Threat Actors
Malware
MarioOver time, the threat actor added more advanced encryption utilities to their toolkit, such as ‘Mario,’ which performs a dual-encryption pass with two keys on target files, and ‘MrAgent,’ which automates the deploymentMrAgenttoolkit, such as ‘Mario,’ which performs a dual-encryption pass with two keys on target files, and ‘MrAgent,’ which automates the deployment of encryptors on VMware ESXi hypervisors.