
Google Ads and Claude Shared Chats Used to Deliver Mac Malware
Summary
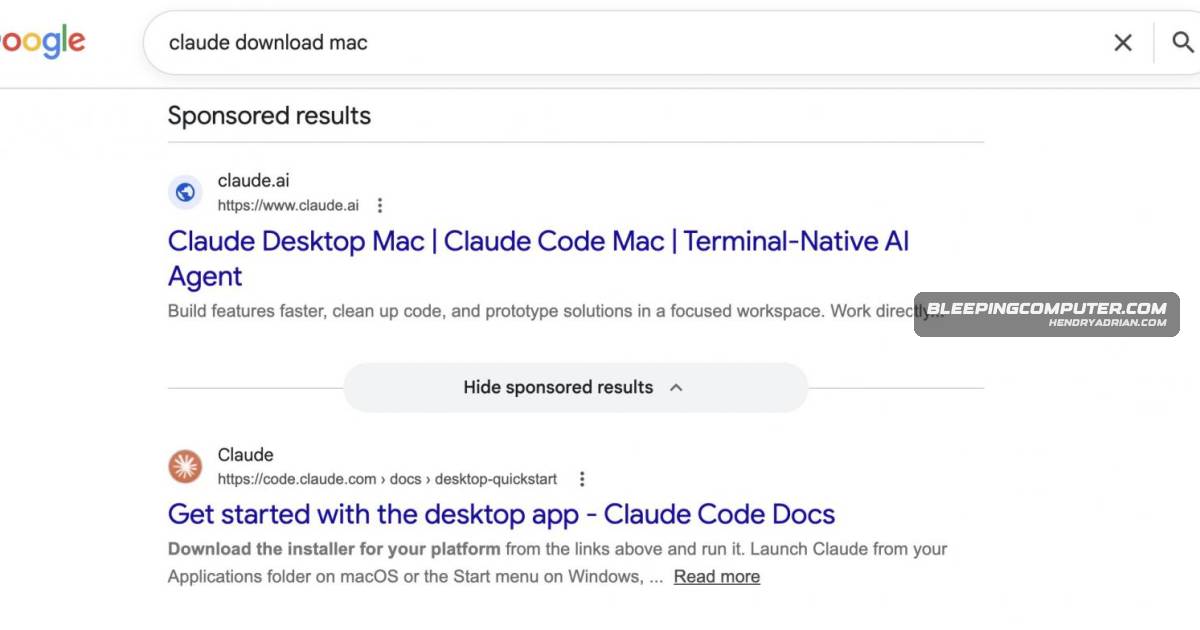
A malvertising campaign uses Google Ads and malicious instructions in genuine Claude[.]ai shared chats to trick macOS users into running shell payloads. Reported variants include polymorphic delivery and a MacSync infostealer targeting browser and Keychain data.
Key points
- Sponsored search results for Claude downloads lead to genuine claude[.]ai shared chats that pose as installation guides and instruct users to paste commands into Terminal.
- Researcher Berk Albayrak identified one malicious chat; BleepingComputer found a second chat using different infrastructure and payloads.
- The payloads use encoded or compressed shell scripts that can run in memory; one observed variant changes its obfuscation on each request.
- A BleepingComputer-observed variant checks for Russian or CIS keyboard input and collects the victim's external IP, hostname, OS version, and keyboard locale before proceeding.
- Albayrak identified a variant as the MacSync infostealer, which steals browser credentials, cookies, and macOS Keychain contents and exfiltrates them.
- The article advises users to navigate directly to Claude's official site and avoid running terminal commands supplied through chat instructions.
Article Details
- Event Type
- Malvertising campaign using Google Ads and malicious instructions in Claude.ai shared chats to deliver macOS malware.
- Impact
- The payloads run shell commands and can collect victim system information. One identified variant, MacSync, steals browser credentials, cookies, and macOS Keychain data and exfiltrates them to an attacker server.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | briskinternet[.]com | Domain associated with the MacSync variant identified by Berk Albayrak; the article says it appeared to be down at the time of writing. |
| URL | hxxp[:]//customroofingcontractors[.]com/curl/b42a0ed9d1ecb72e42d6034502c304845d98805481d99cea4e259359f9ab206e | Malicious URL serving an encoded shell-script payload in the variant identified by Berk Albayrak. |
| URL | hxxps[:]//bernasibutuwqu2[.]com/debug/loader.sh?build=a39427f9d5bfda11277f1a58c89b7c2d | Malicious URL serving the loader.sh payload in the variant observed by BleepingComputer. |
MITRE ATT&CK
T1059.002 · AppleScriptThe second-stage payload is run through osascript.T1059.004 · Unix ShellThe payload uses shell commands executed through Terminal.T1204.004 · Malicious Copy and PasteThe instructions trick users into pasting and running commands from a shared chat.T1539 · Steal Web Session CookieThe MacSync variant steals browser cookies.T1555.001 · KeychainThe MacSync variant steals macOS Keychain contents.T1555.003 · Credentials from Web BrowsersThe MacSync variant steals browser credentials.
People
Malware
Vendors
AnthropicBoth Google ads seen here point to Anthropic’s real domain, claude.ai, since the attackers are hosting their malicious instructions inside Claude’s own shared chat feature.GoogleAttackers are abusing Google Ads and legitimate Claude.ai shared chats to trick macOS users searching for “Claude mac download” into running malware through terminal commands.
Products
Claude CodeThe shared chat presents itself as an official “Claude Code on Mac” guide.claude.aiAttackers are abusing Google Ads and legitimate Claude.ai shared chats to trick macOS users searching for “Claude mac download” into running malware through terminal commands.Google AdsAttackers are abusing Google Ads and legitimate Claude.ai shared chats to trick macOS users searching for “Claude mac download” into running malware through terminal commands.macOSAttackers are abusing Google Ads and legitimate Claude.ai shared chats to trick macOS users searching for “Claude mac download” into running malware through terminal commands.