
Instructure Confirms Canvas Breach Involving XSS and Portal Defacements
Summary
Instructure confirmed data was stolen in a Canvas breach. Attackers used XSS flaws to hijack admin sessions and later deface login portals with a ransom message. ShinyHunters claimed responsibility; Canvas was restored May 9.
Key points
- Instructure said it discovered unauthorized access on April 29, revoked the intruder’s access, and began an investigation with outside forensic experts.
- BleepingComputer reports that multiple XSS flaws in user-generated content features enabled attackers to hijack authenticated admin sessions and perform privileged actions.
- Instructure confirmed data was stolen in the initial breach; ShinyHunters claimed it took more than 3.6 TB of uncompressed data.
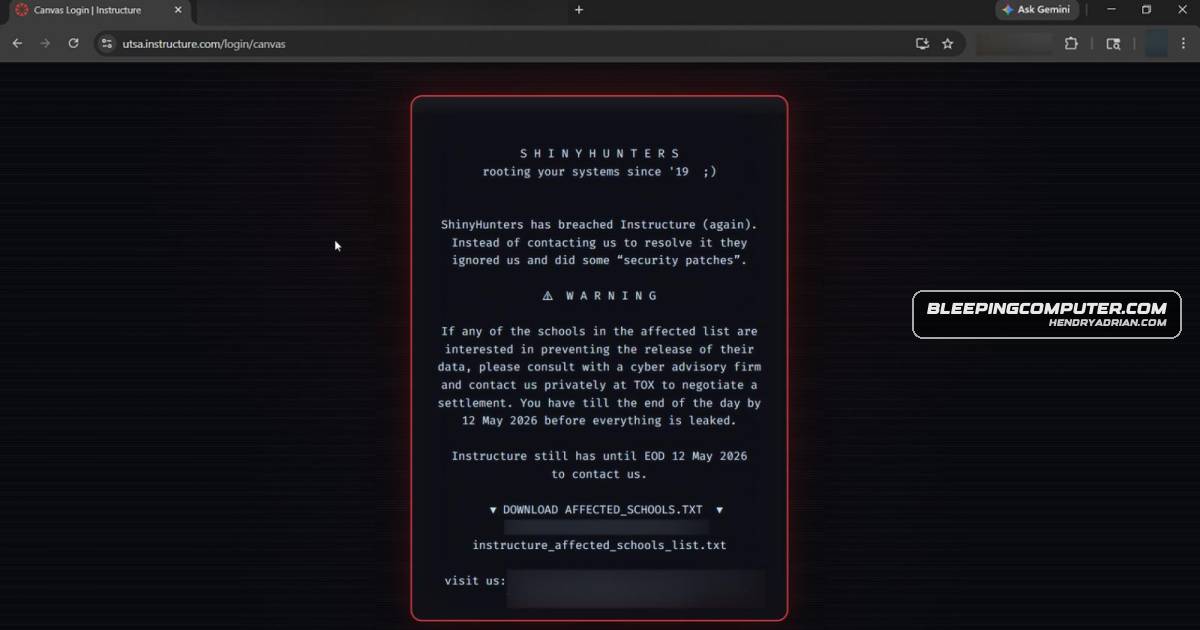
- ShinyHunters allegedly used the same flaw on May 7 to deface Canvas login portals and post a ransom message. The article says no data was compromised in the defacement.
- Instructure said the issue affected Canvas Free-for-Teacher. Canvas was temporarily taken offline and restored on May 9; Free-for-Teacher accounts remained shut down until the issues were resolved.
- ShinyHunters claimed the breach involved 8,809 educational organizations and 275 million records; these figures are attributed to the group.
Article Details
- Victim Organization
- Instructure
- Incident Type
- Confirmed network breach involving multiple cross-site scripting (XSS) vulnerabilities. The attacker reportedly used injected JavaScript to obtain authenticated admin sessions, steal data in the initial breach, and later deface Canvas login portals.
- Data Types Exposed
- Usernames (reported as likely included)
- Email addresses (reported as likely included)
- Course names (reported as likely included)
- Enrollment information (reported as likely included)
- Messages (reported as likely included)
- Affected Records
- ShinyHunters claimed the breach affected 8,809 educational organizations and involved 275 million records belonging to students, teachers, and other staff members.
- Affected Data Size
- ShinyHunters stated it stole more than 3.6 terabytes of uncompressed data.
- Operational Impact
- Instructure temporarily took Canvas offline to contain the activity, investigate, and apply safeguards. Free-for-Teacher accounts were shut down until the issues were resolved. Canvas was restored by May 9; the article gives no year for these dates.
- Ransom Or Extortion
- The article reports that ShinyHunters used the May 7 defacement to pressure Instructure into ransom negotiations. The message on Canvas login portals gave Instructure and schools using the platform until May 12 to make contact and negotiate. The article gives no year for these dates.
- Claim Status
- confirmed