Human Attacker Used AI Agents to Intrude Into Enterprise Network in Under 10 Hours
Summary
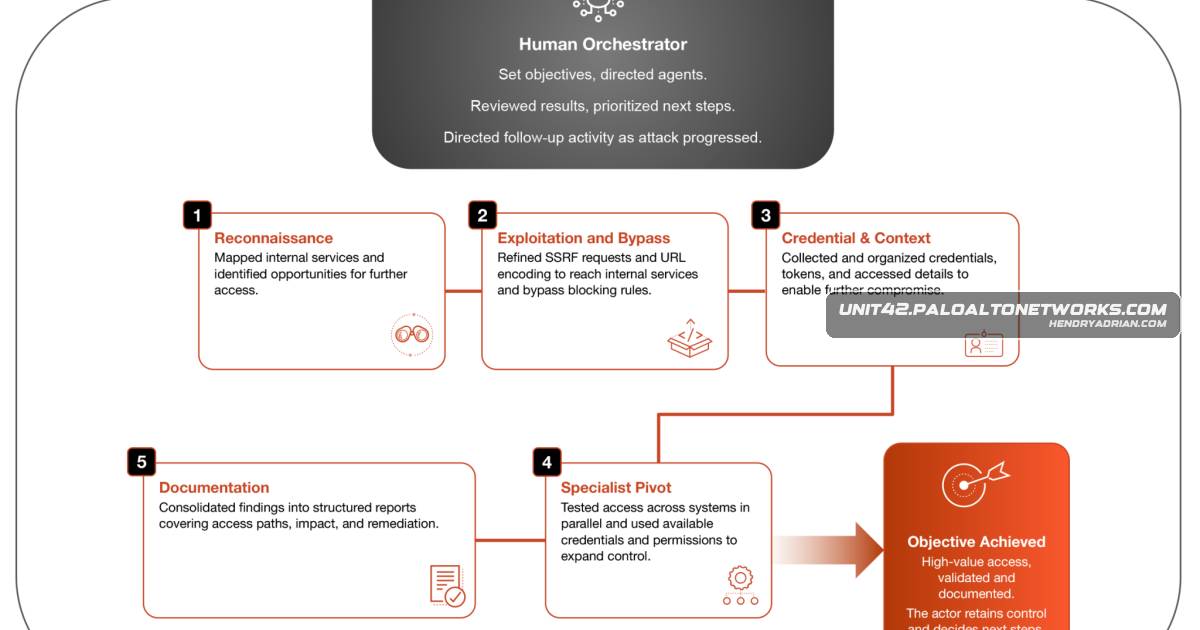
Unit 42 describes an enterprise intrusion in which a human attacker used AI agents to map systems, steal credentials and cloud keys, and abuse CI/CD workflows. The attack unfolded in under 10 hours; the article clarifies it was not ransomware.
Key points
- The attacker reportedly compressed weeks of intrusion activity into less than 10 hours using AI agents and more than 50 MITRE ATT&CK techniques.
- Initial access came through a publicly accessible web service, followed by automated mapping of internal services.
- Agents searched code repositories for secrets and used exposed credentials to access a secrets manager and obtain administrative credentials.
- The attacker abused CI/CD workflows to obtain cloud access keys; branch protections blocked attempted Terraform backdoors.
- Stolen cloud keys were used to invoke the victim's AI infrastructure as post-compromise infrastructure.
- Unit 42 observed indicators consistent with AI use, including parallel LLM calls, structured Markdown files, and custom scripts.
- The article recommends synchronized containment, strict controls and logging for AI services, behavioral-loop detection, and stronger DevOps pipeline protections.
Article Details
- Victim Organization
- Not disclosed
- Incident Type
- Unauthorized enterprise network intrusion involving automated reconnaissance, credential theft, CI/CD abuse, and use of the victim’s AI infrastructure after compromise. The article’s update clarified that this was an intrusion, not a ransomware attack.
- Data Types Exposed
- Source code repository contents
- Hard-coded tokens
- Service passwords
- Master administrative credentials
- Cloud access keys
- Affected Records
- Not disclosed
- Affected Data Size
- Not disclosed
- Operational Impact
- The attacker gained root system access, triggered unauthorized CI/CD builds, and used stolen cloud keys to turn the victim’s AI endpoints into post-compromise infrastructure. An attempted backdoor in Terraform configurations was blocked by branch-protection controls. The attacker also left an 80-page technical audit of exploited findings.
- Ransom Or Extortion
- The article initially described a ransom attack, but an update clarified that the incident was an intrusion, not a ransomware attack. No ransom or extortion activity is reported.
- Claim Status
- confirmed
MITRE ATT&CK
T1046 · Network Service DiscoveryAutomated mapping of internal services; mapped to Network Service Discovery.T1078 · Valid AccountsThe attacker invoked cloud AI models using stolen keys; mapped to Valid Accounts.T1190 · Exploit Public-Facing ApplicationThe attacker breached a publicly accessible web service; mapped to Exploit Public-Facing Application.T1552.001 · Credentials In FilesThe attacker scraped code repositories for secrets; mapped to Credentials In Files.T1555 · Credentials from Password StoresThe attacker infiltrated a secrets manager to harvest administrative credentials; mapped to Credentials from Password Stores.T1578 · Modify Cloud Compute InfrastructureThe article maps CI/CD pipeline activity and attempted cloud provisioning tool edits to Modify Cloud Compute Infrastructure.