
Binance Details Fake-Interview and AI Tool Abuse in $6.43 Billion Theft
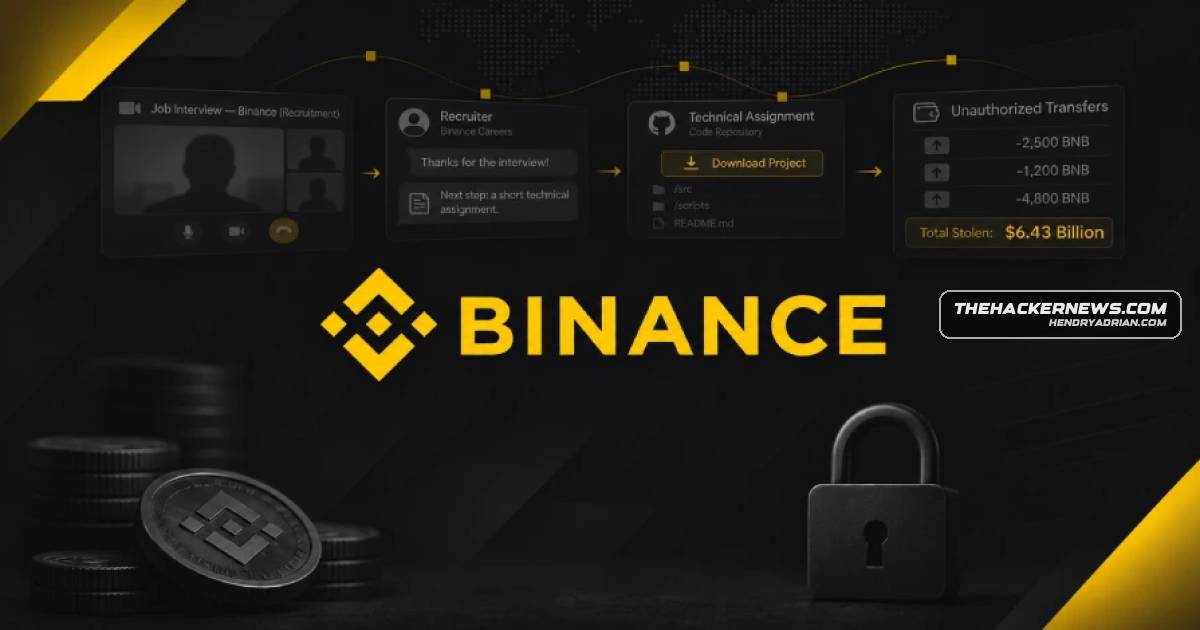
Summary
Binance says a trojanized Homebrew installer and a fake job interview led to engineer endpoint compromise and abuse of internal AI tooling, culminating in unauthorized wallet-signing transactions and a reported $6.43 billion asset theft.
Key points
- Binance traced an initial June 2026 supply-chain attack to an engineer who downloaded a trojanized Homebrew installer while seeking an AI tool.
- In September, a person posing as a company director used fake job interviews to persuade another engineer to download a malicious code repository.
- The malware ran during setup, used a poisoned development-tool component to execute commands and contact an external server, and removed forensic artifacts.
- Binance says the attacker later abused a compromised workstation and internal AI tool to gain control of two other engineers.
- On October 29, the attacker allegedly used stolen credentials and a deployment token to deploy a container and run a malicious script.
- The attacker used unauthorized access to Binance's internal wallet-signing service to initiate transactions outside the normal withdrawal process; Binance reported a $6.43 billion asset theft.
- Binance says it rebuilt affected systems and its internal AI tool, closed identified entry points, tightened device and wallet-service controls, and expanded behavioral anomaly detection.
Article Details
- Victim Organization
- Binance
- Incident Type
- Multi-stage cyberattack involving a trojanized Homebrew installer, recruitment-themed social engineering, malicious code execution, compromised endpoints and internal AI tooling, stolen credentials, and unauthorized access to a wallet signing service.
- Data Types Exposed
- Information about Engineer A's role and related colleagues on the wallet infrastructure team
- Engineer A's credentials
- Affected Records
- Not disclosed
- Affected Data Size
- Not disclosed
- Operational Impact
- The attacker used unauthorized access to Binance's internal wallet signing service to initiate transactions outside the normal withdrawal process. Binance said it reconstructed the affected wallet system, rebuilt its internal AI tool and access controls, and rebuilt or replaced systems involved in the attack path. The article reports a theft of $6.43 billion in assets.
- Claim Status
- confirmed
MITRE ATT&CK
T1059 · Command and Scripting InterpreterThe attacker triggered a malicious script after deploying a container.T1078 · Valid AccountsThe attacker used credentials stolen from Engineer A to log onto Engineer C's computer.T1195.002 · Compromise Software Supply ChainA trojanized Homebrew installer was used in the initial supply chain attack against an engineer.T1204.002 · Malicious FileEngineer B was instructed to download a malicious code repository whose code executed during setup.