
Genesis Claims Ransomware Incident at Pequod Associates
Summary
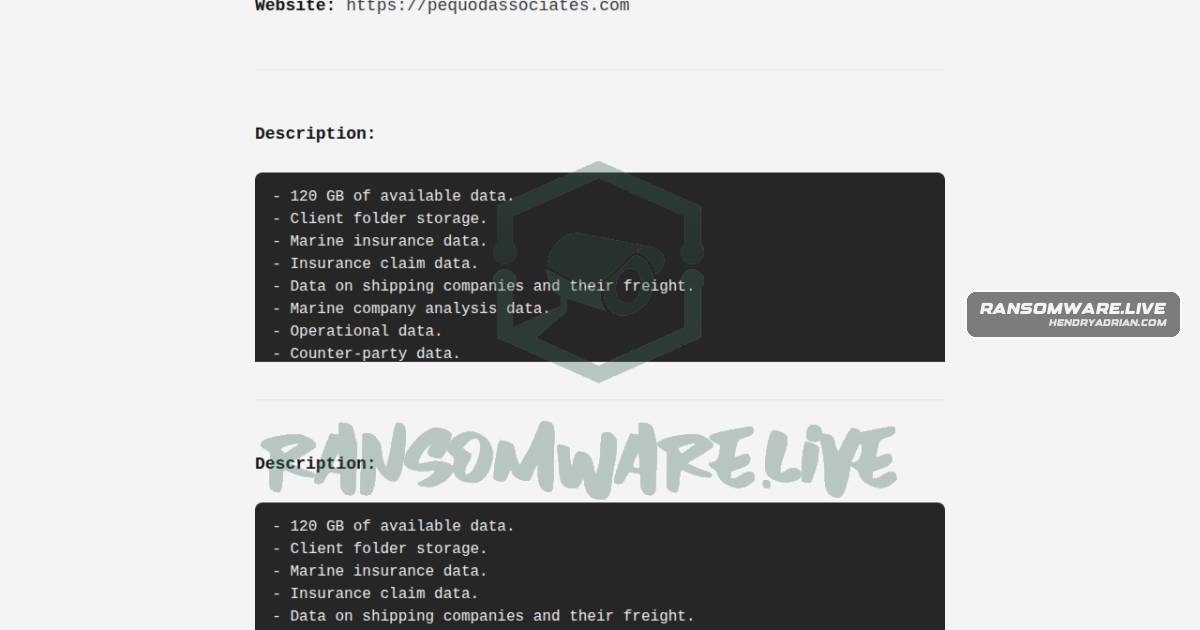
A ransomware.live monitoring post attributes a claim against Pequod Associates to the Genesis group, alleging unauthorized access, data encryption and extortion demands. The post says the claim is unconfirmed.
Key points
- The post names Pequod Associates, a US-based marine claims and recovery services company, as the alleged victim.
- The claim is attributed to the Genesis ransomware group and includes a group source link.
- The post alleges unauthorized access, encryption and extortion demands but states that the information could not be confirmed.
Article Details
- Victim
- Pequod Associates
- Claim Date
- 2026-05-11
- Encryption Status
- Unverified; the article attributes data encryption to the group but says the claim cannot be confirmed.
- Exfiltration Status
- Unknown; exfiltration is not reported.
- Ransom Demand
- An extortion demand is reported in the unverified group claim; no amount is disclosed.
- Leak Status
- Unknown; no leak or publication status is reported.