
Aurora Claims Data from Avanti Windows & Doors
Summary
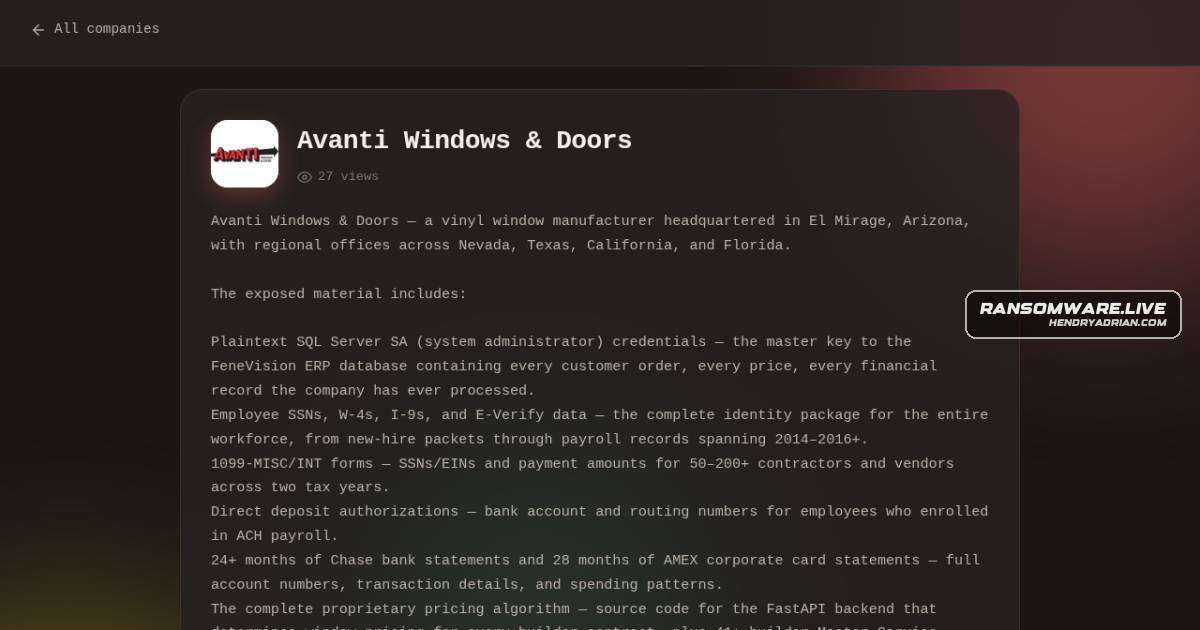
A ransomware.live-monitored post attributes to aurora a claim involving Avanti Windows & Doors. The post lists alleged employee, financial, business, and health-related records; the author says the claims are unconfirmed.
Key points
- The record names Avanti Windows & Doors as the victim and aurora as the ransomware actor.
- A linked aurora post is cited as the claim source; the record says it was monitored by ransomware.live.
- The claim lists employee SSNs, tax forms, identity records, and payroll bank details.
- Other allegedly exposed material includes FeneVision ERP database credentials, financial statements, bank and card statements, and proprietary pricing information.
- The author states that the group's claims could not be confirmed.
Article Details
- Victim
- Avanti Windows & Doors
- Encryption Status
- Unknown
- Exfiltration Status
- Unverified; the article relays a public claim by aurora but does not independently confirm exfiltration.
- Exfiltrated Data
- The group reportedly claims to have information including employee tax and identity records, financial and banking documents, proprietary pricing materials and source code, workplace and insurance records, privileged correspondence, and Windows roaming profiles.
- Ransom Demand
- Not disclosed
- Leak Status
- Unverified; the article reports a public claim by aurora and cautions that the information's accuracy cannot be confirmed.