
Instructure Says ShinyHunters Returned Stolen Canvas Data Under Agreement
Summary
Instructure says ShinyHunters returned data stolen from its Canvas LMS and provided shred logs after an extortion agreement. The breach exposed usernames, emails, course and enrollment details, and messages; attackers exploited Free-for-Teacher and Canvas XSS flaws.
Key points
- Instructure confirmed that data was stolen in a breach affecting its Canvas LMS, used by more than 30 million people across over 8,000 schools and universities.
- The stolen information included usernames, email addresses, course names, enrollment details, and messages.
- ShinyHunters claimed responsibility and said it stole more than 3.6 TB of uncompressed data.
- Instructure says ShinyHunters returned the data and provided shred logs; the company said customers would not be extorted as a result of the incident.
- Instructure confirmed exploitation of a security issue in its Free-for-Teacher environment. BleepingComputer reported that multiple Canvas XSS flaws were used to obtain authenticated admin sessions and perform privileged actions.
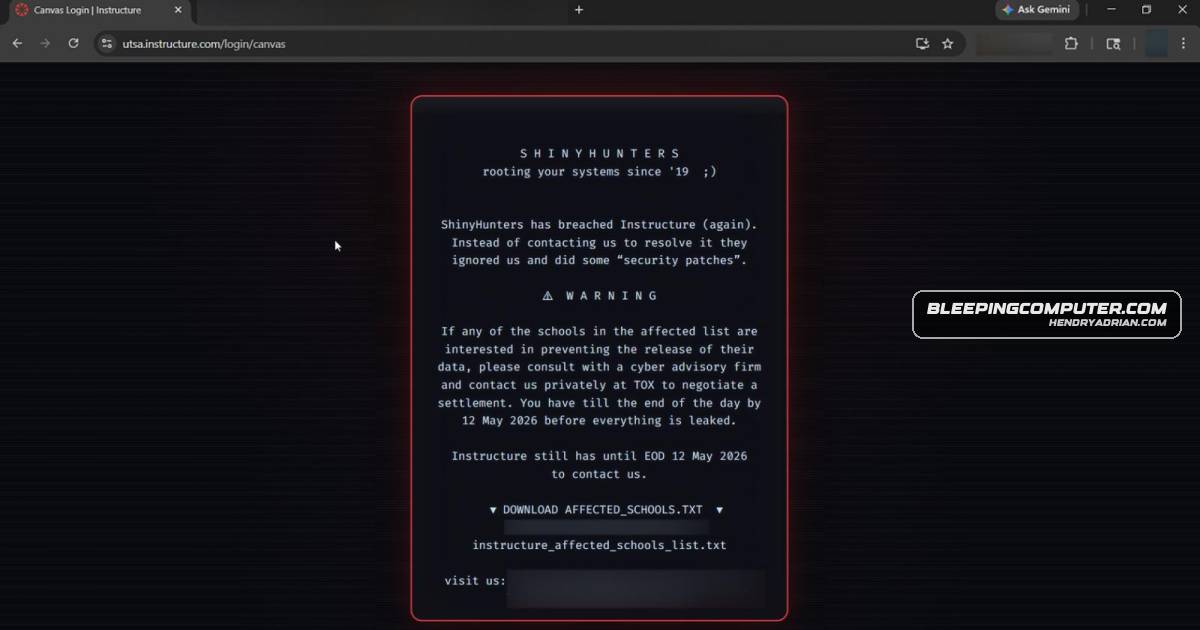
- On May 7, attackers reportedly reused the vulnerability to deface Canvas login portals and post an extortion message.
- Canvas was restored; Instructure temporarily shut down Free-for-Teacher accounts and advised customers to monitor their environments and administrative activity.
Article Details
- Victim Organization
- Instructure
- Incident Type
- Data breach involving exploitation of Canvas XSS vulnerabilities, followed by defacement of login portals and an extortion demand.
- Data Types Exposed
- Usernames
- Email addresses
- Course names
- Enrollment information
- Messages
- Affected Records
- Not disclosed
- Affected Data Size
- ShinyHunters claimed the stolen data comprised more than 3.6 TB of uncompressed data; Instructure did not confirm this volume.
- Operational Impact
- Canvas login pages were defaced, and attackers reportedly obtained authenticated admin sessions and performed privileged actions. Instructure said Canvas was restored and fully available, and temporarily shut down Free-for-Teacher accounts while working to resolve the security issues.
- Ransom Or Extortion
- ShinyHunters left an extortion message demanding negotiations by May 12. Instructure said it reached an agreement with the unauthorized actor, was informed that no customers would be extorted, and that the actor returned the data and provided shred logs. The source does not say whether a ransom was paid.
- Claim Status
- confirmed
MITRE ATT&CK
Threat Actors
Vendors
Products
CanvasInstructure says it reached an agreement with ShinyHunters after the group stole and then returned data from a breach affecting its Canvas LMS, which serves over 30 million users across 8,000 schools and universities.Free-for-TeacherThe attack exploited Free-for-Teacher and Canvas XSS flaws to steal information and deface login portals, and Instructure says no customers will be extorted.