
Signal Adds In-App Warnings Against Phishing and Social Engineering
Summary
Signal added warnings, confirmations, and safety tips to help users spot phishing and fake support messages. The update follows attacks reportedly using QR codes or one-time codes to link devices to targeted accounts.
Key points
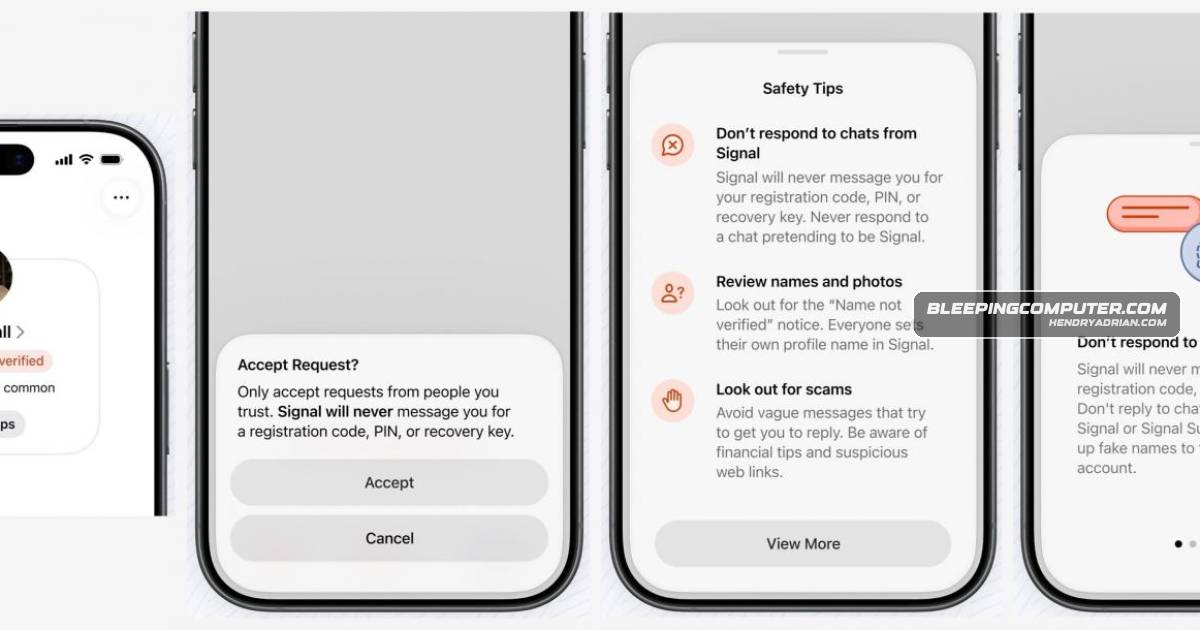
- Signal now labels some direct-message contacts “Name not verified” and indicates when users have “No groups in common.”
- Before accepting a new request, users receive reminders that Signal will not ask for registration codes, PINs, or recovery keys.
- Signal added safety guidance and reminders about chats impersonating Signal Support.
- The article says recent attacks targeting high-profile users used fake support alerts to persuade victims to scan QR codes or share one-time codes.
- Those actions could let attackers link a device to an account and access its chats and contacts; the attacks were attributed to Russian state-sponsored hackers.
Article Details
- Event Type
- Signal introduced in-app safeguards against phishing and social engineering.
- Impact
- The warnings and confirmations are intended to help users identify fraudulent profiles and requests before accepting them or sharing codes. The article reports that attackers attributed to Russian state-sponsored hackers abused Signal's Linked Device feature to access targeted accounts, chats, and contact lists.