
Foxconn confirms cyberattack on North American factories as Nitrogen claims data theft
Summary
Foxconn confirmed a cyberattack affected some North American factories, which are resuming normal production. Nitrogen claims it stole 8 TB and over 11 million documents, but the theft allegation is not independently confirmed.
Key points
- Foxconn said some North American factories suffered a cyberattack and are resuming normal production.
- The company said its cybersecurity team activated response measures to maintain production and deliveries.
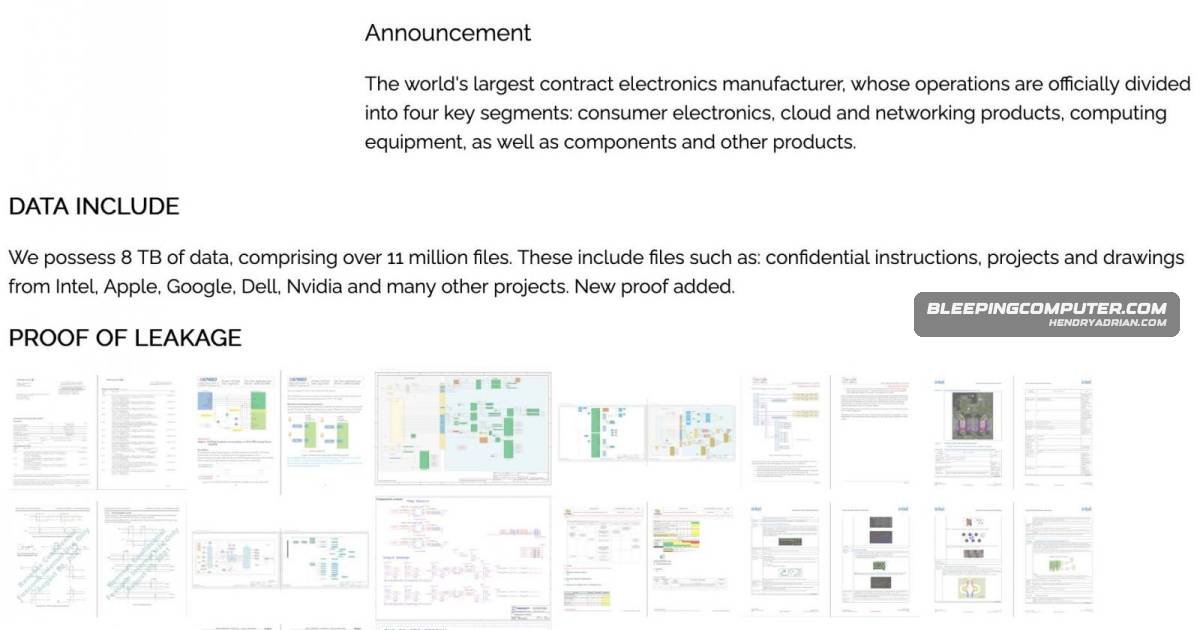
- Nitrogen claims it stole 8 TB of data and more than 11 million documents; the theft claim is unconfirmed.
- Nitrogen's leak site alleges the files include confidential instructions, projects, and drawings tied to Foxconn customers including Apple, Intel, Google, Nvidia, and AMD.
- Nitrogen first surfaced in 2023 with a loader that deployed BlackCat/ALPHV ransomware; the group later developed its own strain using leaked Conti 2 builder code.
- Coveware researchers said a coding error in Nitrogen's ESXi malware causes files to be encrypted with the wrong public key, irrevocably corrupting them.
Article Details
- Victim Organization
- Foxconn
- Incident Type
- Cyberattack affecting some North American factories; Nitrogen claimed a ransomware-related data theft.
- Data Types Exposed
- Confidential instructions, projects, and drawings, according to Nitrogen
- Affected Records
- More than 11 million documents, claimed by Nitrogen
- Affected Data Size
- 8 TB, claimed by Nitrogen
- Operational Impact
- Some North American factories were affected. Foxconn said its cybersecurity team activated its response mechanism and that the affected factories were resuming normal production.
- Ransom Or Extortion
- Nitrogen claimed it stole data and listed Foxconn on its leak site; the article does not report a ransom demand for this incident. It separately reports that DoppelPaymer demanded $34 million in connection with a claimed 2020 incident at a Foxconn facility.
- Claim Status
- confirmed
Threat Actors
DoppelpaymerThe ransomware operation claimed to have hit Foxconn’s CTBG MX facility in December 2020 and allegedly stole data, encrypted servers, and destroyed backup data; it reportedly demanded a $34 million ransom.LockBitThe ransomware group previously claimed to have hit Foxconn subsidiary Foxsemicon in January 2024 and a Foxconn production plant in Tijuana, Mexico, in May 2022.NitrogenThe ransomware operation claimed responsibility for the Foxconn incident and claimed to have stolen 8 TB of data and more than 11 million documents; the reported theft remains a group claim. The article says the operation later developed its own ransomware strain.
Malware
BlackCat/ALPHVâThe threat actors behind the Nitrogen ransomware operation first surfaced in 2023 with a malware loader using the same name that deployed BlackCat/ALPHV ransomware payloads.Conti 2The cybercrime group later developed its own ransomware strain using leaked Conti 2 builder code.NitrogenFoxconn said some of its North American factories are resuming normal operations after a cyberattack, while the Nitrogen ransomware group claimed it stole 8 TB of data and more than 11 million documents.