
Pwn2Own Berlin 2026 Awards $1.29 Million for 47 Zero-Day Exploits
Summary
Researchers earned $1,298,250 for exploiting 47 zero-days at Pwn2Own Berlin 2026. DEVCORE led the contest, and vendors have 90 days to patch the flaws before ZDI publicly discloses them.
Key points
- Contestants earned $1,298,250 for exploiting 47 zero-day flaws across enterprise software, browsers, AI systems, and virtualization technologies.
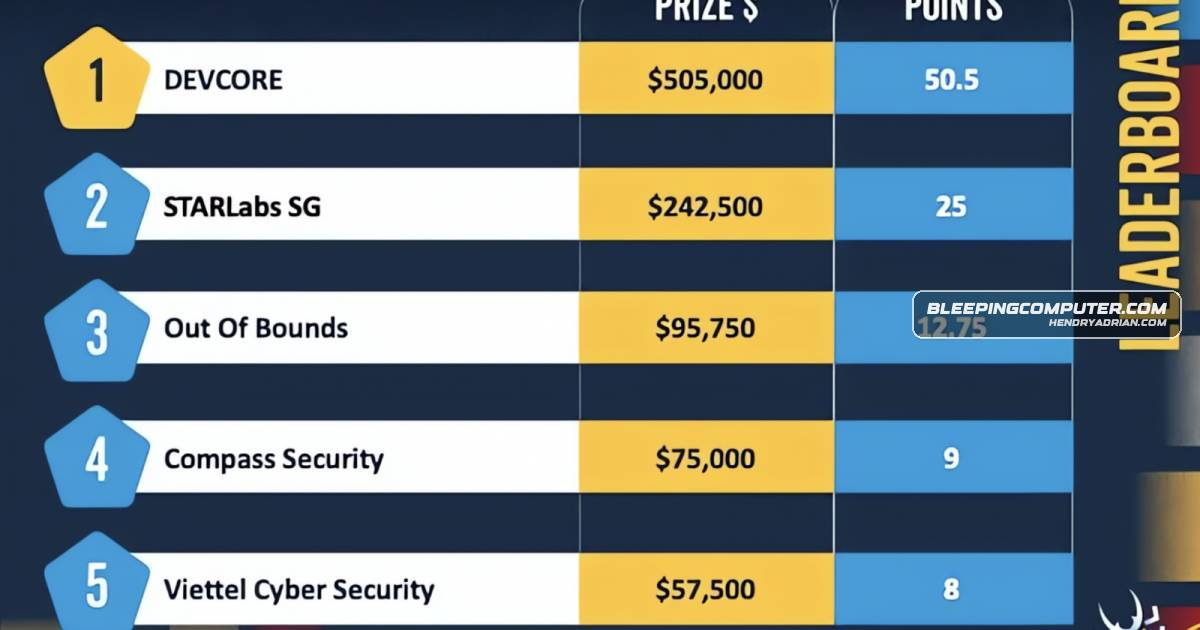
- DEVCORE topped the leaderboard with 50.5 points and $505,000 in rewards.
- Orange Tsai received the top single payout, $200,000, for chaining three bugs to achieve remote code execution with SYSTEM privileges on Microsoft Exchange.
- Other reported targets included Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, VMware ESXi, and AI coding agents.
- Vendors have 90 days to release patches before Trend Micro’s Zero Day Initiative publicly discloses the flaws.
Article Details
- Event Type
- Pwn2Own Berlin 2026 zero-day exploit competition
- Impact
- Researchers demonstrated 47 zero-day flaws in enterprise software, browsers, AI systems, and virtualization technologies, earning $1,298,250 in rewards. The demonstrations included remote code execution with SYSTEM privileges on Microsoft Exchange, a Microsoft Edge sandbox escape, and vulnerabilities affecting Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi. Vendors have 90 days to release patches before ZDI publicly discloses the flaws.
People
Orange TsaiDEVCORE Research Team member who earned the contest's highest reward for chaining three bugs to achieve remote code execution with SYSTEM privileges on Microsoft Exchange; also known as Orange Tsai.Valentina PalmiottiIBM X-Force Offensive Research participant who earned $70,000 for rooting Red Hat Enterprise Linux for Workstations and demonstrating a zero-day in NVIDIA Container Toolkit; also known as chompie.
Vendors
MicrosoftDEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.NvidiaDEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.Red HatDEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.TrendMicroAfter Pwn2Own ends, vendors have 90 days to release security patches before TrendMicro’s Zero Day Initiative (ZDI) publicly discloses them.VMwareDEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.
Products
Microsoft EdgeDEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.Microsoft ExchangeDEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.Nvidia Container ToolkitDEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.Red Hat Enterprise Linux for WorkstationsDEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.VMware ESXiDEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.Windows 11DEVCORE topped the leaderboard, with standout wins against Microsoft Exchange, Microsoft Edge, Windows 11, Red Hat Enterprise Linux for Workstations, NVIDIA Container Toolkit, and VMware ESXi.