MintsLoader Campaign Uses Compromised Certified Email Accounts to Deliver Malware
Summary
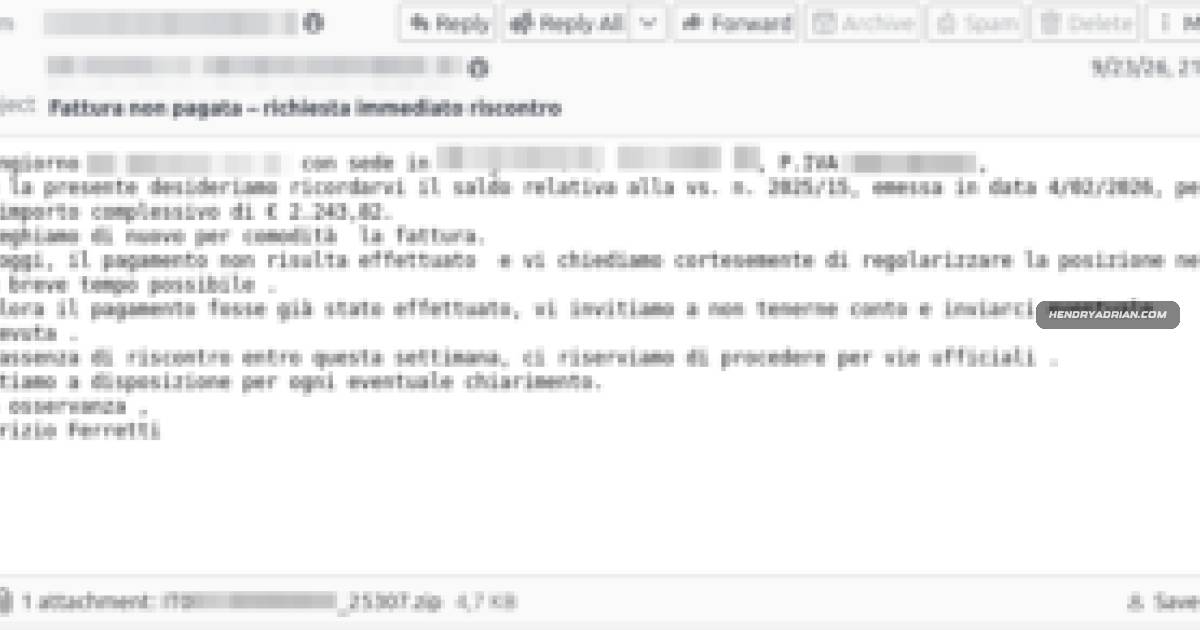
CERT-AGID reports a campaign using compromised certified email accounts to send fake invoice reminders with ZIP attachments. The files launch a chain leading to MintsLoader and potentially RATs or stealers.
Key points
- The campaign used compromised PEC accounts to send convincing fake payment reminders, including references to unpaid invoices.
- Messages carried ZIP archives containing HTML files rather than the expected invoices.
- Opening the HTML triggered a download chain involving JavaScript and PowerShell that executed MintsLoader, which can load other malware, including RATs and stealers.
- The campaign used frequently changing retrieval addresses, including domains generated with DGA techniques.
- Some attacker-controlled addresses were initially inactive and became operational on the morning of September 24.
- CERT-AGID coordinated countermeasures with PEC providers and shared campaign indicators with accredited organizations.
- CERT-AGID warns that a valid PEC sender does not rule out account compromise or make an attachment safe.
Article Details
- Event Type
- Malware distribution through fraudulent payment-reminder emails sent from compromised certified email (PEC) accounts
- Impact
- Opening the attached ZIP and its HTML file can start a chain that executes MintsLoader, which downloads and runs further malware. The article depicts RATs or stealers as possible final payloads but does not report a number of infected systems.
MITRE ATT&CK
T1059.001 · PowerShellLater infection stages used PowerShell.T1204.002 · Malicious FileThe infection chain depended on a recipient opening the HTML file inside the ZIP attachment.T1566.001 · Spearphishing AttachmentFraudulent payment-reminder emails carried malicious ZIP attachments.T1568.002 · Domain Generation AlgorithmsAddresses used to retrieve components changed frequently and also used Domain Generation Algorithm techniques.