
GitHub Says Malicious VS Code Extension Led to Exfiltration of 3,800 Internal Repositories
Summary
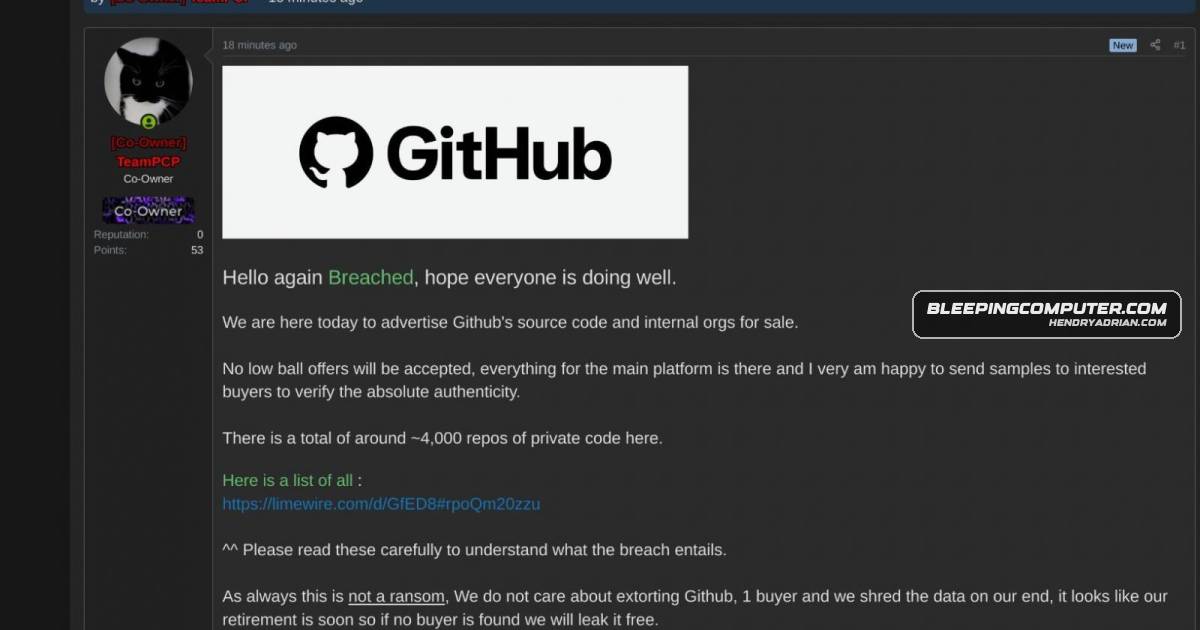
GitHub says a malicious VS Code extension on an employee device led to the exfiltration of about 3,800 internal repositories. TeamPCP claimed access; GitHub said it found no evidence that customer data outside those repositories was affected.
Key points
- GitHub detected and contained a compromise of an employee device involving a poisoned VS Code extension.
- GitHub’s current assessment is that the activity involved exfiltration of internal repositories; the group’s claim of about 3,800 repositories is consistent with its investigation so far.
- GitHub removed the malicious extension version, isolated the affected endpoint, and began incident response.
- TeamPCP claimed access to GitHub source code and about 4,000 private repositories on a cybercrime forum, offering the data for at least $50,000.
- GitHub said it has no evidence that customer data outside the affected repositories was impacted; it has not attributed the breach.
Article Details
- Victim Organization
- GitHub
- Victim Domain
- github.com
- Incident Type
- Compromise of an employee device via a malicious VS Code extension, followed by exfiltration of GitHub-internal repositories.
- Data Types Exposed
- GitHub-internal source code and private repositories
- Affected Records
- About 3,800 internal repositories; GitHub said the attackers’ claim of approximately 3,800 was directionally consistent with its investigation.
- Operational Impact
- GitHub removed the malicious extension version, isolated the affected endpoint, and began incident response. GitHub said it had no evidence that customer data outside the affected repositories was impacted.
- Ransom Or Extortion
- TeamPCP claimed access and offered the stolen data for sale, asking for at least $50,000. The group said it would leak the data if no buyer was found and described the offer as not being a ransom. A sale or leak was not confirmed.
- Claim Status
- confirmed