
U.S. and Canada Arrest Suspected KimWolf Botnet Operator
Summary
Canadian authorities arrested Jacob Butler, accused of operating the KimWolf DDoS-for-hire botnet; he faces extradition to the U.S. Authorities also seized 45 DDoS-for-hire platforms, while officials linked KimWolf to more than 25,000 attacks.
Key points
- Canadian authorities arrested 23-year-old Jacob Butler, also known as “Dort,” in Ottawa on an extradition warrant; he faces one U.S. count of aiding and abetting computer intrusions.
- A criminal complaint cited IP and online account information, transaction records, and messages as evidence linking Butler to KimWolf.
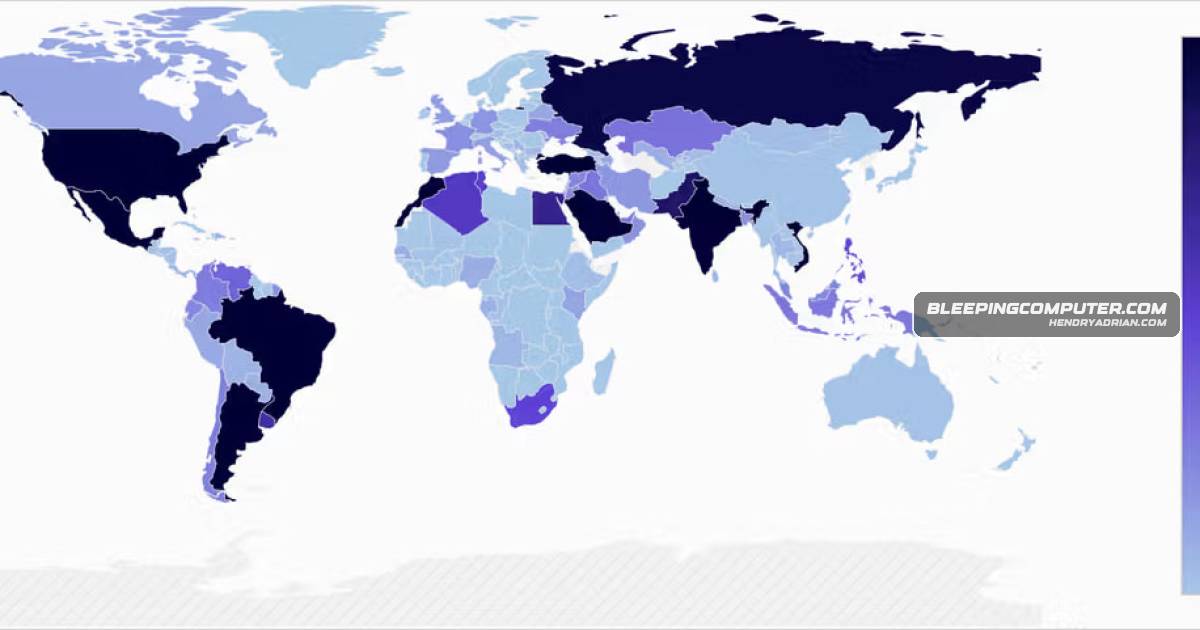
- Researchers at Synthient said KimWolf grew to nearly two million infected devices, including Android devices, and generated about 12 million unique IP addresses weekly.
- Court documents describe KimWolf as a DDoS-for-hire service used in more than 25,000 attacks, including against Department of Defense network IP addresses; attacks reached nearly 30 Tbps.
- Authorities unsealed seizure warrants targeting 45 DDoS-for-hire platforms, disrupting several services and redirecting associated domain records to warning pages.
- A March 2026 operation seized command-and-control infrastructure for KimWolf and the related Aisuru, JackSkid, and Mossad botnets, which authorities said collectively infected more than three million IoT devices.
Article Details
- Event Type
- Arrest and criminal charge of a suspected KimWolf botnet operator, alongside disruption of DDoS-for-hire platforms.
- Impact
- Authorities allege that KimWolf infected nearly two million devices and enabled more than 25,000 attacks worldwide, including attacks against Department of Defense network IP addresses. Attacks reached nearly 30 terabits per second, and some victims suffered losses exceeding $1 million. Authorities also disrupted 45 DDoS-for-hire platforms and seized associated domain records.
MITRE ATT&CK
Threat Actors
DortOnline alias identified in the article as belonging to Jacob Butler, who is accused of operating the KimWolf botnet.Jacob ButlerAuthorities arrested and charged Butler over allegedly operating the KimWolf botnet; he is accused of aiding and abetting computer intrusions and awaits extradition to the U.S.
Malware
Products
Countries
CanadaRead More: https://www.bleepingcomputer.com/news/security/us-and-canada-arrest-and-charge-suspected-kimwolf-botnet-admin/United StatesU.S. and Canadian authorities arrested Jacob Butler for allegedly running the KimWolf DDoS botnet, a service that infected nearly two million devices and powered attacks at massive scale.