
Loxone Reports Unauthorized Access to Internal Systems; Samurai Claim Unconfirmed
Summary
LOXONE says it detected unauthorized access to internal systems on Oct. 18, 2026, and isolated affected systems. A notice attributed to the Samurai ransomware group claimed 201.6 GB was copied and encrypted; LOXONE has not confirmed data theft.
Key points
- LOXONE reported detecting a cyberattack and unauthorized third-party access to internal company systems on Oct. 18, 2026.
- The company says affected systems were isolated and external security experts and forensic investigators are examining the incident; authorities were informed.
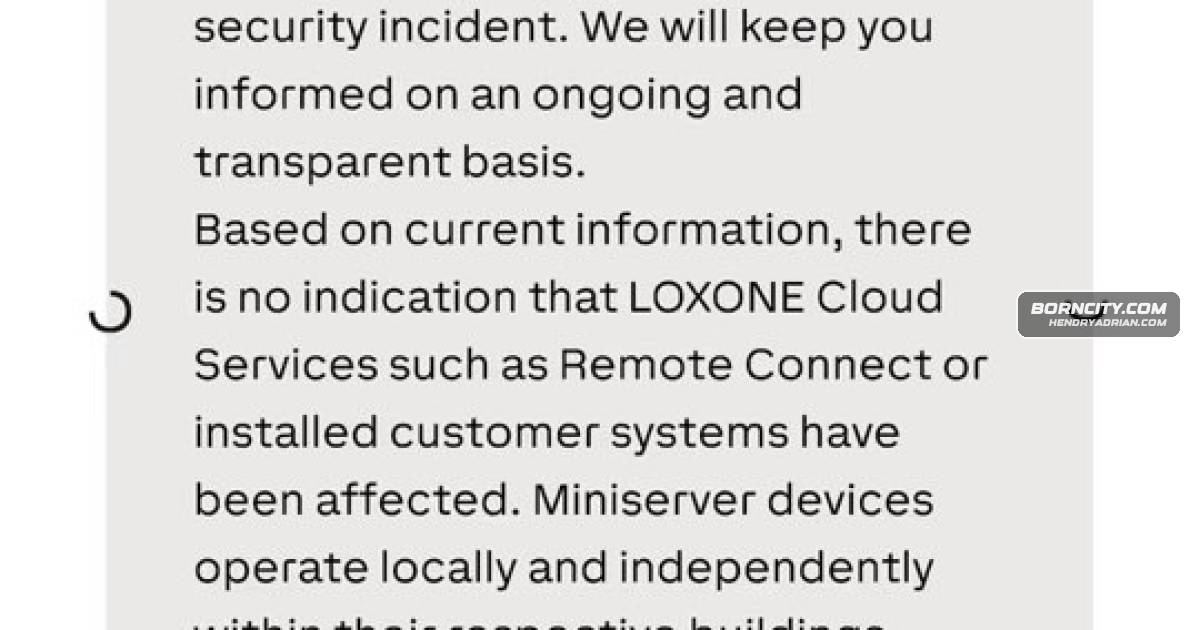
- LOXONE says its Miniserver, Remote Connect and Exosphere services were not affected, and installations continued operating.
- A screenshot attributed to a ransomware notice from a group calling itself Samurai claimed 201.6 GB was copied and encrypted, and threatened publication. LOXONE has not confirmed the alleged data theft.
- The article says LOXONE planned to bring services back online in stages from around Oct. 20.
Article Details
- Victim Organization
- LOXONE Group
- Incident Type
- Cyberattack involving unauthorized access to internal company IT systems; a ransomware attack was alleged by a group calling itself Samurai.
- Incident Date
- 2026-10-18
- Disclosure Date
- 2026-10-18
- Affected Data Size
- 201.6 GB, according to a ransomware notice attributed to Samurai; the company had not confirmed the alleged data theft.
- Operational Impact
- LOXONE isolated affected systems and began forensic analysis. The company said its Miniserver, Remote Connect, Exosphere, and other services were unaffected, and installations continued to operate. It was gradually bringing systems back online as of 2026-10-20.
- Ransom Or Extortion
- A ransomware notice attributed to Samurai claimed data had been copied and encrypted, threatened publication after a countdown, and urged LOXONE to negotiate via Session. The notice also threatened that the price would rise after the timer expired. LOXONE had not confirmed the alleged data exfiltration.
- Claim Status
- confirmed