
JR Tokai Takashimaya Reports Unauthorized Access to Hiring Server; Data Exposure Unconfirmed
Summary
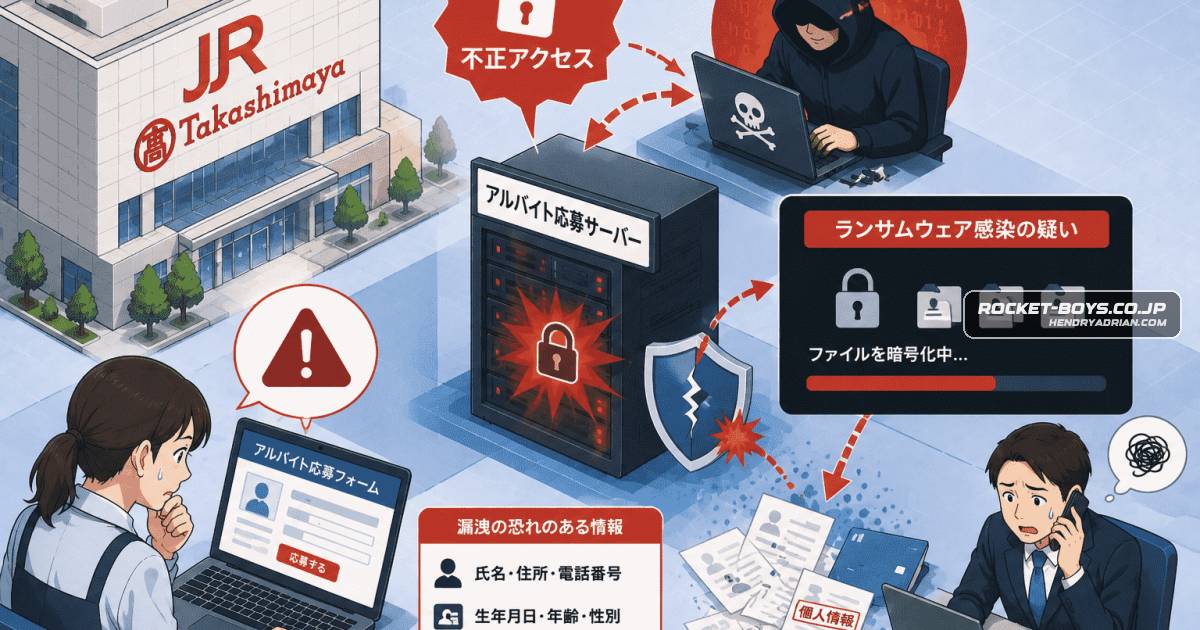
JR Tokai Takashimaya reported unauthorized access to its part-time hiring server. Up to 1,338 employees’ personal data, including bank account details, may have been exposed; leakage is unconfirmed and a ransomware infection is suspected.
Key points
- The company said it detected unauthorized access to its part-time hiring server on May 1, 2026, and announced the incident on May 8.
- The server held data for part-time employees hired from March 1, 2021 onward; up to 1,338 records may be affected.
- Potentially exposed information includes names, contact details, and bank account information for salary deposits.
- The company said actual data leakage has not been confirmed and that a ransomware infection is suspected; its investigation with external specialists is ongoing.
- The server was disconnected from the network after detection, and new part-time employee registrations were suspended.
Article Details
- Victim Organization
- 株式会社ジェイアール東海高島屋
- Incident Type
- Unauthorized access to the part-time employee application server; ransomware infection was suspected.
- Incident Date
- 2026-05-01
- Disclosure Date
- 2026-05-08
- Data Types Exposed
- Names
- Contact information
- Payroll bank account details
- Affected Records
- Up to 1,338 part-time employees contracted on or after 2021-03-01 may have been affected; actual data leakage had not been confirmed.
- Operational Impact
- The server was isolated from the network after detection. New part-time employee registrations were suspended while the company investigated with external specialists. No impact on customer personal information was reported.
- Ransom Or Extortion
- No ransom demand or confirmed data exfiltration was reported. The article says double extortion could not be ruled out.
- Claim Status
- confirmed