July 2026 Attacks Targeted US, European and Brazilian Organizations with Phishing and Malware
Summary
ANY.RUN reports July campaigns targeting organizations in the US, Europe and Brazil with phishing, account-takeover tactics, RATs and stealers that threatened cloud accounts, financial workflows, credentials and sensitive data.
Key points
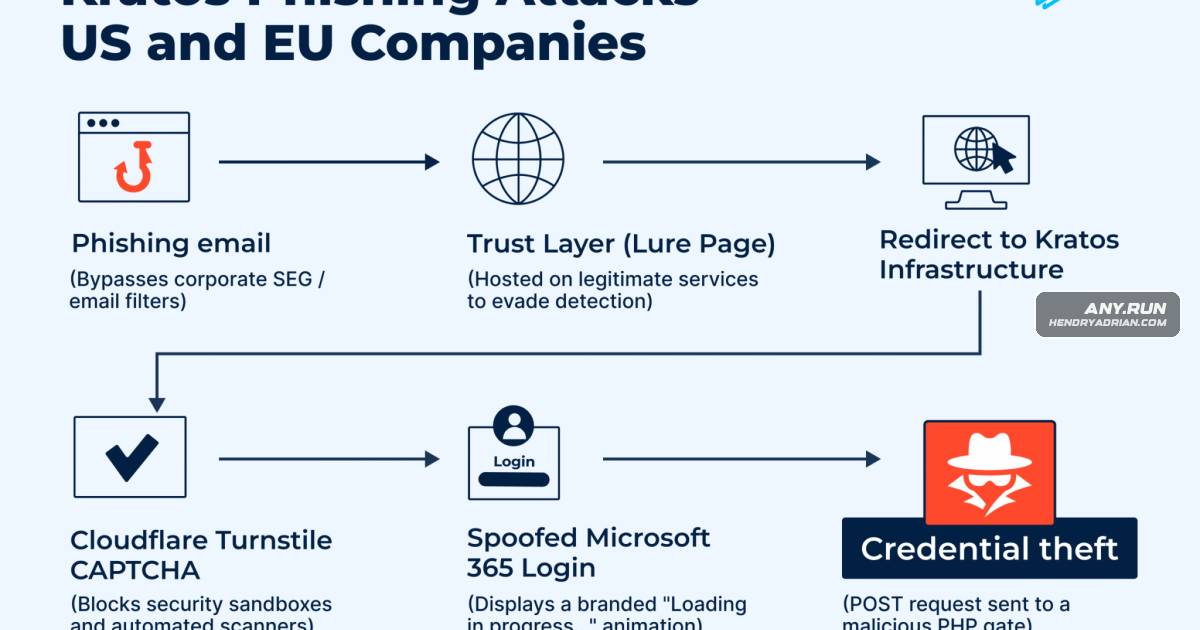
- Kratos phishing used document-sharing and invoice lures to target Microsoft 365 accounts, potentially exposing email, files and payment workflows.
- Kali365 used Microsoft device-code authentication to obtain OAuth access and refresh tokens, potentially enabling continued cloud access without stealing passwords.
- PhantomEnigma used at least 20 compromised Brazilian government portals and compromised government mailboxes to deliver malware to banking and public-sector targets.
- Banana RAT added randomized identifiers, stronger persistence and encrypted WebSocket communications; its capabilities included remote control and monitoring banking sessions.
- A malicious PDF-themed LNK file used Windows tools, AutoIt and PowerShell to deploy DARTHVADER Stealer and establish persistence.
- During analysis of an infection targeting Germany and the UK, an operator deployed OVERLORD RAT and transmitted about 86 MB of data in 45 minutes.
- DestinyStealer collected browser, Outlook, VPN, file-transfer and wallet data; the article advises investigating exposed accounts and access, not just cleaning the infected endpoint.
Article Details
- Event Type
- Multiple cyberattacks observed in July 2026, including phishing, account takeover, remote-access trojan activity, credential theft, and malware delivery.
- Impact
- The attacks put cloud accounts, corporate email, shared files, supplier communications, payment workflows, financial activity, and sensitive data at risk. Reported capabilities and effects included stolen credentials and tokens, potential fraud and payment redirection, persistence, remote control, and data exfiltration. The article reports activity affecting organizations in the United States, Europe, and Brazil; it does not quantify overall losses or confirmed victim counts.
Malware
Banana RATA single endpoint could expose access across the business: DestinyStealer, Banana RAT, DARTHVADER Stealer, and OVERLORD RAT collected or targeted browser credentials, cookies, Outlook data, VPN access, file-transferDARTHVADER StealerA single endpoint could expose access across the business: DestinyStealer, Banana RAT, DARTHVADER Stealer, and OVERLORD RAT collected or targeted browser credentials, cookies, Outlook data, VPN access, file-transferDestinyStealerA single endpoint could expose access across the business: DestinyStealer, Banana RAT, DARTHVADER Stealer, and OVERLORD RAT collected or targeted browser credentials, cookies, Outlook data, VPN access, file-transferOverlord RATendpoint could expose access across the business: DestinyStealer, Banana RAT, DARTHVADER Stealer, and OVERLORD RAT collected or targeted browser credentials, cookies, Outlook data, VPN access, file-transfer accounts,PythonRATWhile analyzing a PythonRAT infection, ANY.RUN observed the attacker connect to the compromised system, upload another payload, and deploy OVERLORD RAT in real time.StormKittyIts code also showed clear continuity with StormKitty.
Vendors
MicrosoftTrusted business services created false confidence: SharePoint, OneDrive, Zoom Events, Microsoft authentication pages, and compromised government systems appeared in attack chains.ZoomTrusted business services created false confidence: SharePoint, OneDrive, Zoom Events, Microsoft authentication pages, and compromised government systems appeared in attack chains.
Products
Canvalures, often routing victims through trusted services such as SharePoint, OneDrive, Microsoft Forms, Canva, and Tilda before displaying a fake Microsoft login page.FileZillaDestinyStealer focused on credentials and information held in browsers, Outlook, VPN clients, FileZilla, Wi-Fi profiles, and wallet extensions.Microsoft 365Identity attacks threatened core business workflows: Kratos and Kali365 put Microsoft 365 accounts, corporate email, shared files, supplier communication, and payment conversations at risk.Microsoft Formsand invoice lures, often routing victims through trusted services such as SharePoint, OneDrive, Microsoft Forms, Canva, and Tilda before displaying a fake Microsoft login page.Microsoft OneDriveTrusted business services created false confidence: SharePoint, OneDrive, Zoom Events, Microsoft authentication pages, and compromised government systems appeared in attack chains.Microsoft SharePointTrusted business services created false confidence: SharePoint, OneDrive, Zoom Events, Microsoft authentication pages, and compromised government systems appeared in attack chains.OutlookBanana RAT, DARTHVADER Stealer, and OVERLORD RAT collected or targeted browser credentials, cookies, Outlook data, VPN access, file-transfer accounts, cryptocurrency wallets, and other sensitive information.Tildaoften routing victims through trusted services such as SharePoint, OneDrive, Microsoft Forms, Canva, and Tilda before displaying a fake Microsoft login page.ZoomTrusted business services created false confidence: SharePoint, OneDrive, Zoom Events, Microsoft authentication pages, and compromised government systems appeared in attack chains.
Tools
AutoItLegitimate tools made malicious activity harder to separate from normal operations: PowerShell, AutoIt, Windows utilities, trusted applications, and cloud services helped attackers hide inside familiar system activity.PowerShellLegitimate tools made malicious activity harder to separate from normal operations: PowerShell, AutoIt, Windows utilities, trusted applications, and cloud services helped attackers hide inside familiar system activity.
Countries
BrazilANY.RUN observed attacks that put cloud accounts, financial processes, sensitive data, and business continuity at risk across the US, Europe, and Brazil.GermanyThe activity, seen targeting Germany and the UK, showed that the initial infection was only the first step in a broader compromise.SpainKratos affected SMBs, law firms, schools, polytechnic institutions, and industrial organizations, with a strong concentration in Spain and Southern Europe.United KingdomThe activity, seen targeting Germany and the UK, showed that the initial infection was only the first step in a broader compromise.United StatesJuly’s campaigns reached organizations across the United States, Europe, and Brazil, with activity affecting both private and public-sector environments.
Industries
BankingBanking organizations in Brazil ConsultingKali365 activity appeared across manufacturing, technology, healthcare, government, consulting, and MSSPs.EducationGovernmentTrusted business services created false confidence: SharePoint, OneDrive, Zoom Events, Microsoft authentication pages, and compromised government systems appeared in attack chains.HealthcareKali365 activity appeared across manufacturing, technology, healthcare, government, consulting, and MSSPs.LegalPhantomEnigma used police and legal themes and compromised government infrastructure during delivery.Managed Security Service ProvidersManufacturingKali365 activity appeared across manufacturing, technology, healthcare, government, consulting, and MSSPs.TechnologyKali365 activity appeared across manufacturing, technology, healthcare, government, consulting, and MSSPs.