
REXT Holdings Reports VPN-Linked Ransomware Incident at D&M, 633 Records at Risk
Summary
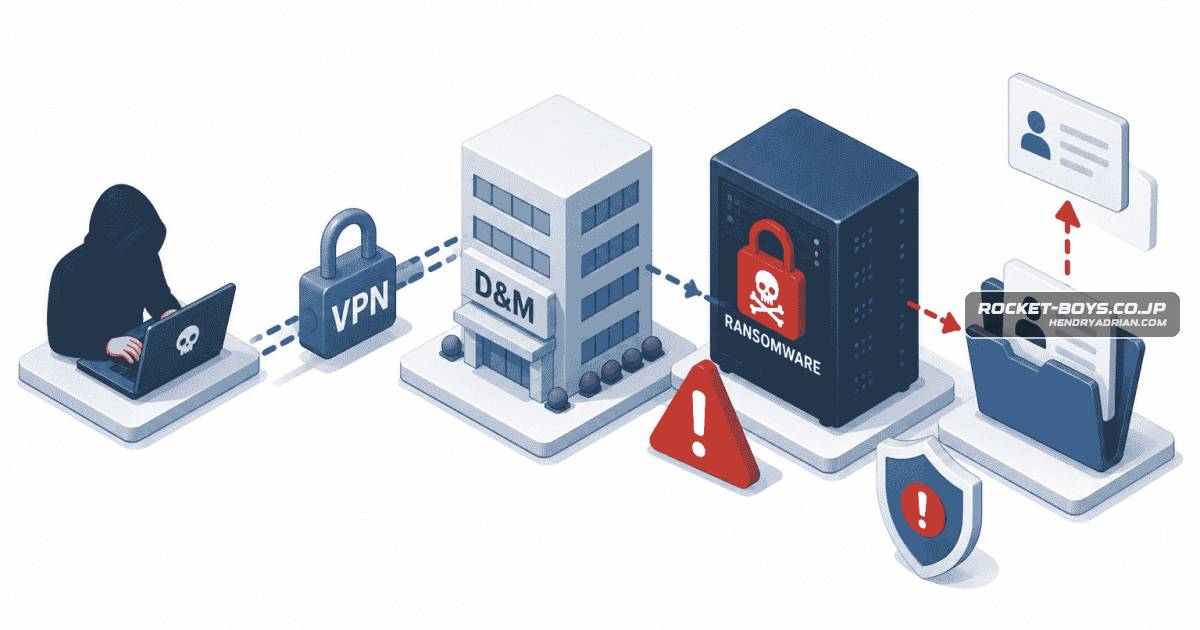
REXT Holdings says attackers accessed subsidiary D&M’s file-sharing server via a VPN and infected it with ransomware. About 633 FAX-order records may have been exposed; payment data was not confirmed affected. Operations resumed on June 1.
Key points
- REXT Holdings reported that unauthorized access through a VPN led to ransomware infection of subsidiary D&M’s file-sharing server; the incident was discovered on June 1, 2026.
- About 633 FAX-order PDFs from August 1, 2024, to June 1, 2026, contained customer and business-partner names, addresses, and phone numbers that may have been exposed.
- The company said external leakage of the data was highly likely, but did not report confirmed exfiltration.
- Credit-card and bank-account information had not been confirmed affected; secondary misuse was also unconfirmed.
- D&M isolated the affected server and completed security measures for the VPN equipment. Normal operations resumed on the discovery date with minimal disruption.
- The company said it was making required reports to public authorities and planned to strengthen monitoring and prevention.
Article Details
- Victim Organization
- D&M
- Victim Domain
- dmsupporter.jp
- Incident Type
- Ransomware infection of a file-sharing server following unauthorized access via VPN; external exposure of personal data is considered highly likely but was not confirmed.
- Disclosure Date
- 2026-06-12
- Data Types Exposed
- Names
- Addresses
- Telephone numbers
- Business partner and customer information contained in fax order PDFs
- Affected Records
- 633 cases
- Operational Impact
- The file server was isolated from the network and security measures were completed for the VPN equipment. Normal operations resumed on 2026-06-01 after safety checks, with only minor disruption to routine business.
- Ransom Or Extortion
- None reported.
- Claim Status
- confirmed