
Meitetsu Kyosho Confirms Ransomware-Linked Server Intrusion and Service Disruptions
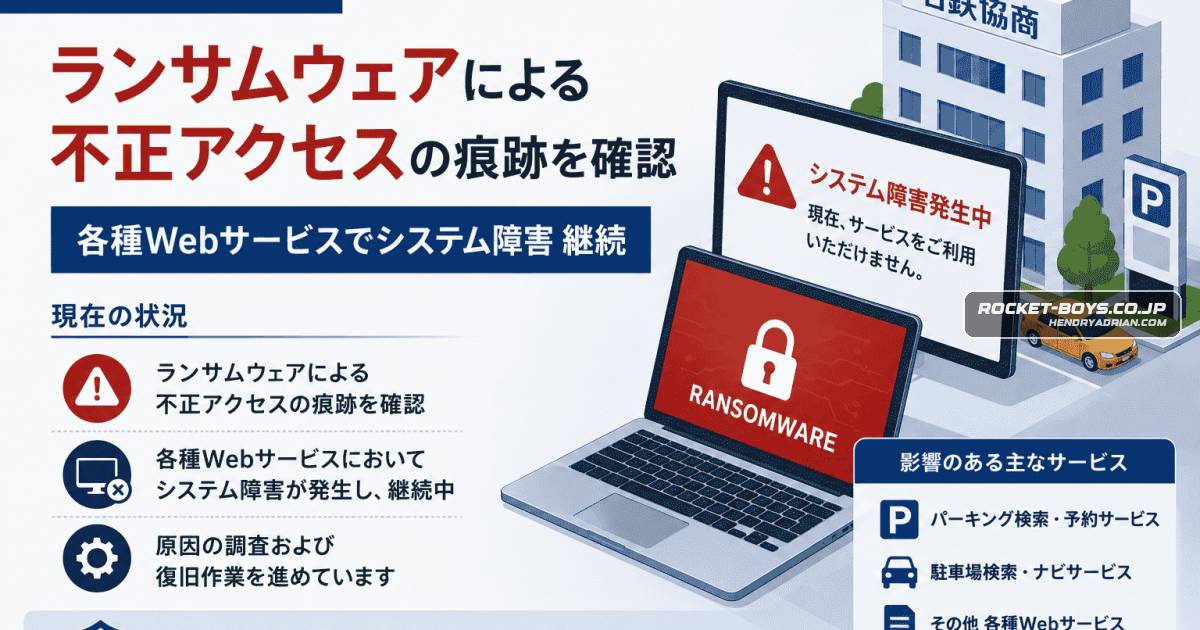
Summary
Meitetsu Kyosho says an external investigation found traces of ransomware-related unauthorized access on June 19. Multiple services were disrupted; as of July 2, the company had not confirmed an external data leak and was still investigating.
Key points
- Meitetsu Kyosho detected suspicious server access on June 23 and announced the incident on July 2.
- An external investigation found traces of ransomware-related unauthorized access on June 19.
- The company isolated affected systems and disconnected them from the network.
- Disruptions affected parking, points-card, business-card, ticket-sales, car-share and other services; some functions were stopped or delayed.
- The company said no external information leak had been confirmed as of July 2.
- The cause and full scope remained under investigation, with recovery expected to take several days; the company also consulted police and relevant authorities.
Article Details
- Victim Organization
- 名鉄協商株式会社
- Victim Domain
- mkyosho.co.jp
- Incident Type
- Unauthorized server access; an external investigation confirmed traces of ransomware-related unauthorized access.
- Incident Date
- 2026-06-19
- Disclosure Date
- 2026-07-02
- Operational Impact
- Some servers stopped, and the company isolated systems and blocked network connections. Several websites and services experienced outages or delays, including parking-related services, point-card procedures, business-card services, ticket sales, and car-share services. Restoration was expected to take several days. The time-rental parking service continued operating normally.
- Ransom Or Extortion
- Unknown
- Claim Status
- confirmed