
Wazuh Promotes Managed SIEM/XDR Platform With AI-Assisted Alert Triage
Summary
In sponsored content, Wazuh describes its managed SIEM/XDR platform for hybrid and multi-cloud environments, highlighting automated operations, endpoint monitoring, scalable indexing, and an AI analyst that generates weekly assessments and remediation recommendations.
Key points
- Wazuh presents its cloud-native service as a way to reduce SIEM/XDR deployment and maintenance work for security teams.
- Wazuh agents collect logs, monitor file integrity, assess configurations, and detect rootkits; the article says events are forwarded to the managed service over an encrypted channel.
- The platform includes vulnerability detection and Security Configuration Assessment, alongside preconfigured rules and dashboards.
- Wazuh says its managed indexer scales automatically and its detection engine correlates events across data sources to reduce false positives.
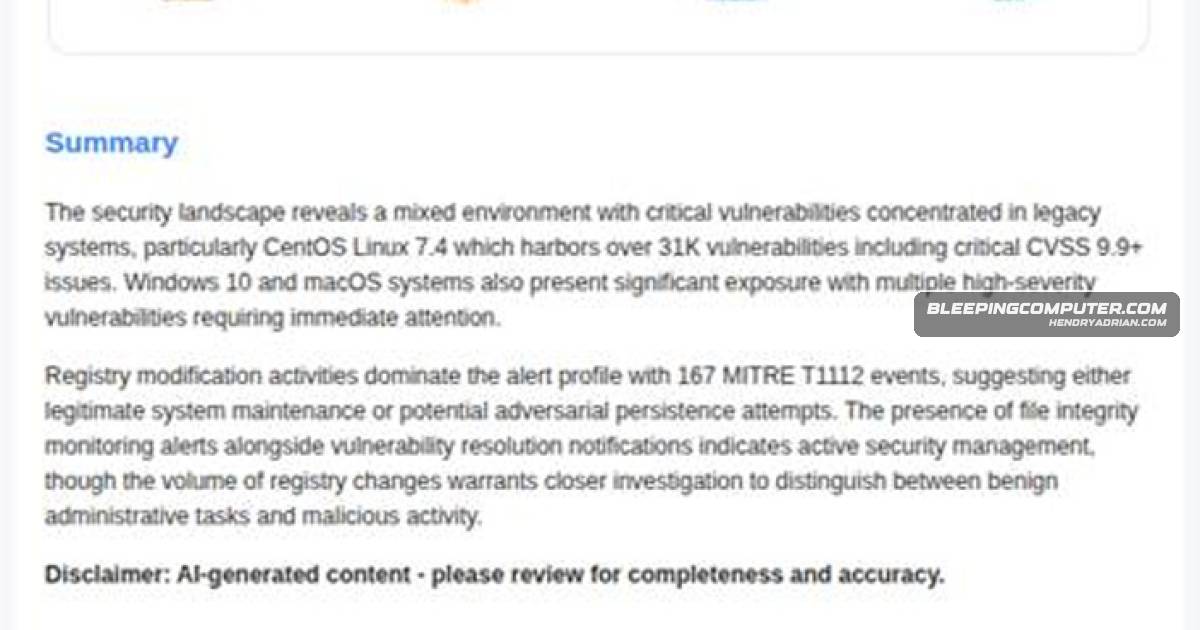
- The Wazuh AI Security Analyst processes alerts, vulnerability findings, and endpoint activity to produce weekly assessments and remediation recommendations.
- Wazuh describes backend maintenance, patches, rule updates, and version upgrades as managed services; these capabilities are vendor claims in sponsored content.
Article Details
- Event Type
- Sponsored product overview of Wazuh Cloud, a managed cloud-native SIEM/XDR platform.
- Impact
- Wazuh says the platform automates operations, scales with agent volume and data ingestion, and uses its AI Security Analyst to help prioritize alerts and remediation. The article presents these as potential operational benefits; it reports no specific security incident or independently verified impact.
Vendors
Products
WazuhWazuh Cloud is presented as a managed, cloud-native SIEM/XDR platform that helps security teams reduce deployment delays, maintenance burden, and alert fatigue in complex hybrid and multi-cloud environments.Wazuh CloudWazuh Cloud is presented as a managed, cloud-native SIEM/XDR platform that helps security teams reduce deployment delays, maintenance burden, and alert fatigue in complex hybrid and multi-cloud environments.