
m3rx Claims SuppCenter Global Systems Were Compromised in Argentina
Summary
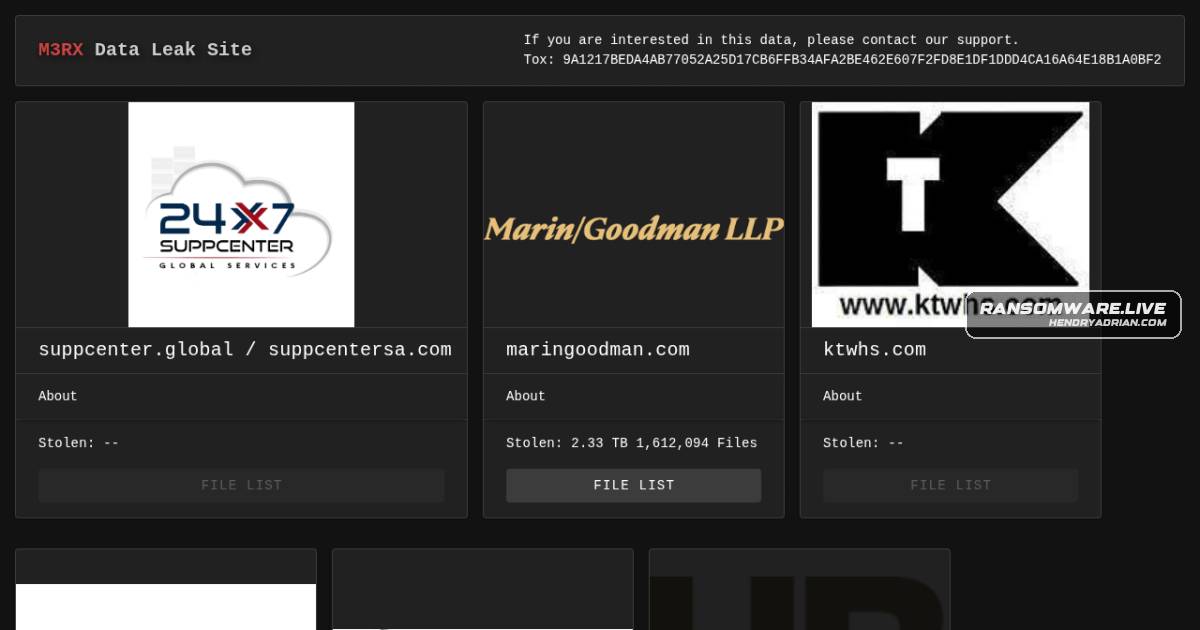
The m3rx ransomware group reportedly claimed SuppCenter Global’s systems were compromised; ransomware.live lists suppcenter[.]global and suppcentersa[.]com in Argentina. The post says the claim is unverified.
Key points
- A ransomware.live monitoring record attributes the compromise claim to the m3rx group and cites a group leak-site listing.
- The record names SuppCenter Global and suppcentersa.com in Argentina.
- The claim that systems were compromised is unverified; the post says it cannot confirm the information.
- SuppCenter Global is described as an MSSP and Xcitium/Comodo security-solutions partner using Xcitium Zero Trust and ZeroDwell technologies.
Article Details
- Victim
- SuppCenter Global Services
- Victim Domain
- suppcenter.global / suppcentersa.com
- Claim Date
- 2026-06-11
- Encryption Status
- Unknown
- Exfiltration Status
- Unknown
- Exfiltrated Data
- Not disclosed
- Ransom Demand
- Not disclosed
- Leak Status
- A claim was published; data publication was not reported.
Threat Actors
Vendors
COMODOclaiming their systems were compromised while using SuppCenter Global’s role as an MSSP and Xcitium/Comodo managed security solutions partner against them.XcitiumArgentina, claiming their systems were compromised while using SuppCenter Global’s role as an MSSP and Xcitium/Comodo managed security solutions partner against them.
Products
Xcitium Zero TrustThe incident aligns with the disruption of Xcitium Zero Trust/ZeroDwell threat prevention deployments associated with their cybersecurity services.ZeroDwellThe incident aligns with the disruption of Xcitium Zero Trust/ZeroDwell threat prevention deployments associated with their cybersecurity services.