
Microsoft’s October 2026 Patch Tuesday Fixes 1,414 Vulnerabilities
Summary
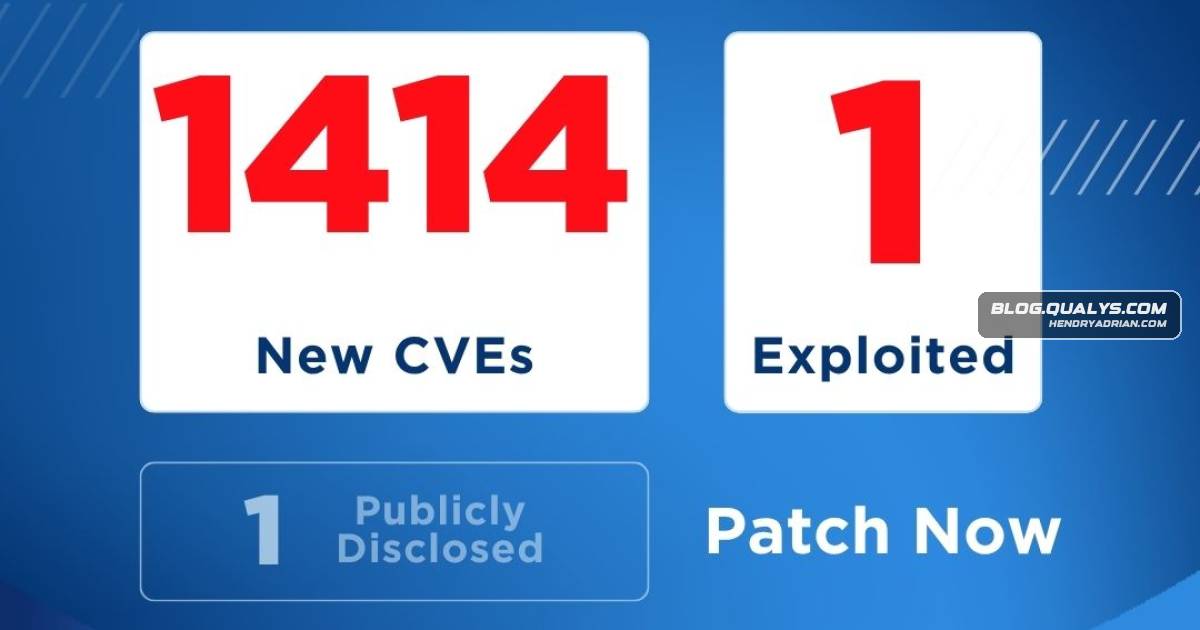
Microsoft’s October 2026 updates address 1,414 vulnerabilities, including 78 rated critical. The article highlights an actively exploited Windows Shell flaw and provides vulnerability details and Qualys remediation guidance.
Key points
- The article reports 1,414 Microsoft vulnerabilities addressed across product families, including 78 critical and 1,329 important-severity issues.
- It identifies CVE-2026-96951, a Windows Shell security-feature bypass, as actively exploited; CISA added it to the Known Exploited Vulnerabilities Catalog and urged patching by October 16.
- The article also lists CVE-2026-108398, a .NET Framework security-feature bypass, in its section on zero-day vulnerabilities.
- Critical issues highlighted include remote code execution flaws in Microsoft QUIC, Exchange Server and Windows components, as well as privilege-escalation vulnerabilities.
- The article reports that Adobe issued 11 advisories covering 176 vulnerabilities, 23 rated critical.
- Qualys provides vulnerability queries and says its mitigation scripts cover 608 vulnerabilities; the article describes configuration changes and patch deployment options.
Article Details
- Event Type
- Microsoft October 2026 Patch Tuesday security update release
- Impact
- Microsoft reported fixes for 1,414 vulnerabilities, including 78 rated critical and 1,329 rated important. The release includes vulnerabilities that could enable remote code execution, privilege escalation, denial of service, or security-feature bypass. CVE-2026-96951, a Windows Shell command-injection flaw that may allow an unauthenticated attacker to bypass a security feature over a network, was reported as actively exploited; CISA added it to its Known Exploited Vulnerabilities Catalog.
CVE
CVE-2026-105016CVE-2026-105016 Microsoft QUIC Remote Code Execution Vulnerability A heap-based buffer overflow flaw in Microsoft QUIC allows an unauthenticated attacker to execute code over a network. CVE-2026-108398CVE-2026-108398: .NET Framework Security Feature Bypass VulnerabilityCVE-2026-70571CVE-2026-70571 Microsoft Exchange Server Remote Code Execution Vulnerability A stack-based buffer overflow flaw in Microsoft Exchange Server allows an unauthenticated attacker to execute code over a network. CVE-2026-96951CVE-2026-96951: Windows Shell Security Feature Bypass Vulnerability
Vendors
Products
.NET FrameworkCVE-2026-108398: .NET Framework Security Feature Bypass VulnerabilityMicrosoft Exchange ServerCVE-2026-70571 Microsoft Exchange Server Remote Code Execution Vulnerability A stack-based buffer overflow flaw in Microsoft Exchange Server allows an unauthenticated attacker to execute code over a network. Microsoft QUICCVE-2026-105016 Microsoft QUIC Remote Code Execution Vulnerability A heap-based buffer overflow flaw in Microsoft QUIC allows an unauthenticated attacker to execute code over a network. Windows ShellCVE-2026-96951: Windows Shell Security Feature Bypass Vulnerability