
ClickFix Campaign Uses Fake Cloudflare Checks to Target macOS and Windows
Summary
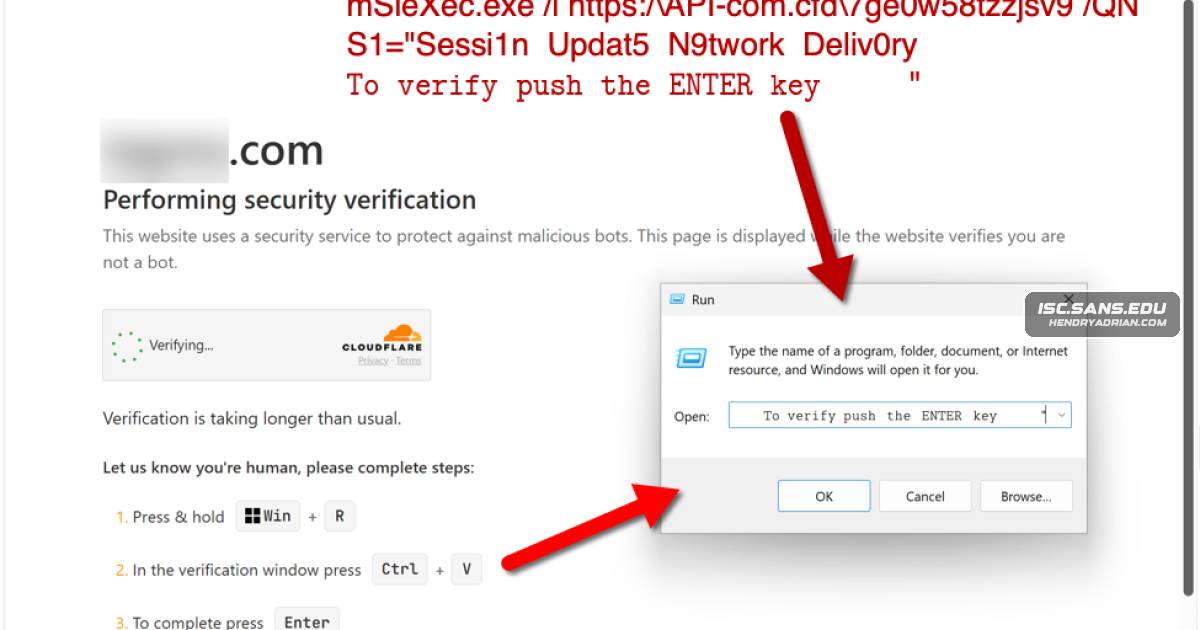
A SANS diary described a newly observed ClickFix campaign using a fake Cloudflare verification page on macOS and Windows. The malware could not be retrieved: one server returned 403, and another domain did not resolve.
Key points
- The campaign used a fake Cloudflare verification page with ClickFix instructions and targeted both macOS and Windows.
- The researcher could not obtain the malware; the Windows command's server returned 403 Forbidden, while the macOS command's domain did not resolve on October 28, 2026.
- The fake verification page was hosted at js-static[.]cfd; the ClickFix commands referenced cf-id[.]com and api-com[.]cfd.
- The diary says a legitimate but compromised website generated the activity, but removed information identifying that site.
- The activity had no specific campaign name in the diary.
Article Details
- Event Type
- A newly observed ClickFix campaign using a fake Cloudflare verification page and targeting macOS and Windows.
- Impact
- The campaign's malware was not retrieved: the Windows malware-hosting server returned 403 Forbidden, and the macOS malware-hosting domain did not resolve. The article does not report a confirmed infection.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | js-static[.]cfd | Domain hosting the fake verification page and related campaign activity. |
| URL | hxxps[:]//api-com[.]cfd/7ge0w58tzzjsv9 | URL shown in the Windows ClickFix text; the article identifies its server as hosting malware, but it returned 403 Forbidden. |
| URL | hxxps[:]//cf-id[.]com/?ray-id=nz0ovm2jq2g68i | URL shown in the ClickFix text on macOS; the article identifies its domain as the malware-hosting server, which did not resolve when checked. |
| URL | hxxps[:]//js-static[.]cfd/embed.js?v=24 | Campaign script served from the domain hosting the fake verification page. |