
Article Warns AI KYC May Be Bypassed With Stolen Sessions and Synthetic Identities
Summary
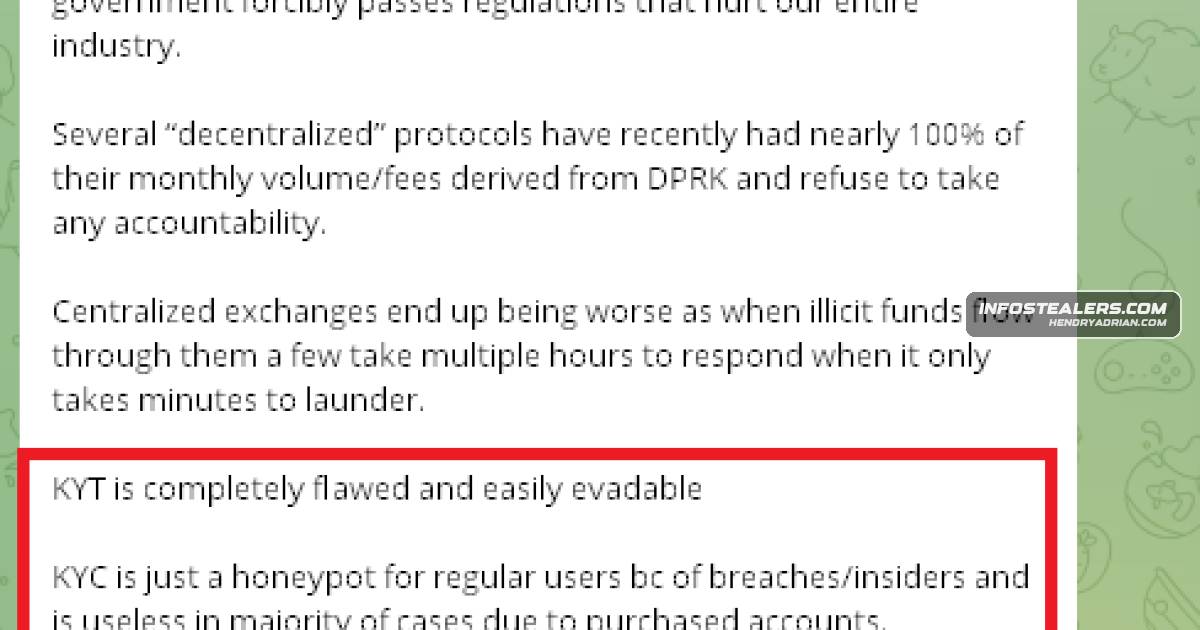
Article argues stolen infostealer sessions, pre-verified accounts and synthetic identities could bypass planned AI-platform KYC, while passport and biometric stores could become breach targets. The text provides no independent validation.
Key points
- The article says U.S. export controls have taken Fable 5 and Mythos 5 offline for foreign users, prompting frontier AI labs to consider financial-grade KYC.
- It argues infostealer logs from Lumma, Vidar and RedLine can expose session cookies and credentials for AI services, enabling account access that bypasses onboarding and MFA.
- The article cites Hudson Rock intelligence claiming more than 30,000 corporate OpenAI credentials were harvested by infostealer infections; it gives no supporting methodology.
- It describes pre-verified accounts, synthetic identities, stolen identity documents, deepfakes and voice manipulation as ways criminals may evade identity and biometric checks.
- It warns that collecting passports and biometric data could make AI-provider identity stores attractive targets; a breach is presented as a risk, not a reported incident.
Article Details
- Topic
- Cybercriminal bypasses of AI-platform KYC controls and the security risks of collecting identity data
MITRE ATT&CK
T1078 · Valid AccountsThe article describes attackers using stolen credentials or pre-verified accounts to access AI platforms as legitimate users.T1539 · Steal Web Session CookieThe article describes infostealer logs containing active session cookies and tokens that attackers import to hijack users' sessions.
People
Malware
Vendors
Products
claude.aiactive session tokens, cookies, and saved credentials for vital infrastructure platforms, including Claude.ai and OpenAI. An adversary in a restricted jurisdiction can purchase these stolen logs from undergroundFable 5export controls on Fable 5 and Mythos 5 are pushing frontier AI labs toward KYC-based access controls, but cybercriminals are already preparing to bypass them with stolen sessions, synthetic identities, and pre-verifiedMythos 5export controls on Fable 5 and Mythos 5 are pushing frontier AI labs toward KYC-based access controls, but cybercriminals are already preparing to bypass them with stolen sessions, synthetic identities, and pre-verified