
China-Linked UNC6508 Used REDCap Backdoor and Google Workspace Rules to Steal Emails
Summary
Google attributes a campaign to UNC6508 with high confidence: the group used INFINITERED in compromised REDCap servers and abused Google Workspace rules to copy targeted emails. Google says it notified affected organizations and disrupted the group’s infrastructure.
Key points
- Google says UNC6508 targeted clinical, academic, military health, advocacy, and regulatory organizations in the US and Canada.
- The group compromised externally facing REDCap servers; Google did not identify the initial access vector, a specific CVE, or affected versions.
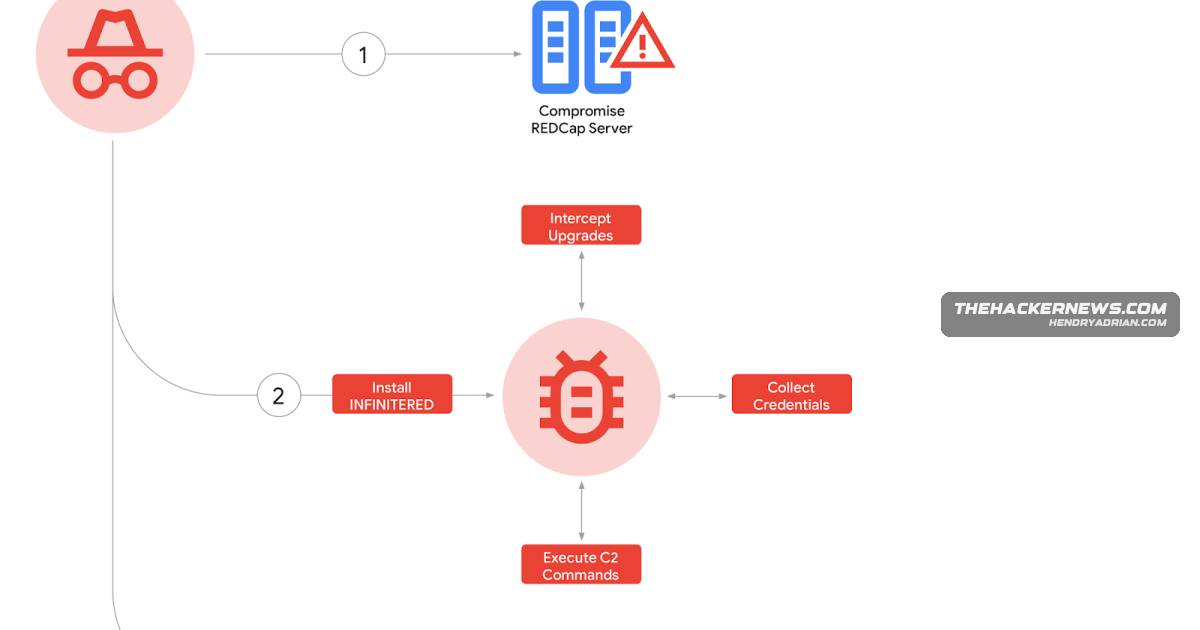
- INFINITERED trojanized REDCap system files, persisted through upgrades, harvested credentials, and accepted commands through HTTP cookies.
- After reconnaissance and credential discovery, the group used stolen credentials to move through internal networks and reach a domain administrator account.
- UNC6508 abused Google Workspace content compliance rules to silently BCC emails matching nearly 150 keywords and addresses to an attacker-controlled account.
- Google says it notified affected organizations and disrupted the group’s infrastructure; the attacker-controlled Gmail account was disabled.
- Recommended defenses include patching externally exposed REDCap servers, removing legacy versions, auditing mail rules and admin logs, hunting for INFINITERED, and enforcing phishing-resistant MFA for administrators.
Article Details
- Attack Vectors
- UNC6508 compromised externally facing REDCap servers; Google did not determine the initial access vector.
- The attackers deployed INFINITERED, which modified REDCap system files, captured login credentials, and accepted commands through HTTP cookies.
- Using credentials obtained on the servers, the attackers moved into internal networks and reached a domain administrator account.
- With administrator access, UNC6508 abused Google Workspace content compliance rules to BCC matching email to an attacker-controlled Gmail inbox.
- Defensive Notes
- Patch externally facing REDCap servers and remove legacy versions, rather than leaving older versions installed alongside current builds.
- Review Google Workspace content compliance and mail-forwarding rules for unexpected external BCC or rerouting destinations; inspect audit logs for rule changes.
- Hunt for INFINITERED using GTIG’s published indicators.
- Enforce phishing-resistant MFA for administrator accounts.
MITRE ATT&CK
T1056.003 · Web Portal CaptureINFINITERED captured usernames and passwords from the REDCap login page and stored them in local database tables.T1071.001 · Web ProtocolsINFINITERED accepted commands through HTTP cookies.T1078 · Valid AccountsThe attackers used credentials obtained from REDCap servers to access internal network resources and reach a domain administrator account.T1114.003 · Email Forwarding RuleUNC6508 created a Google Workspace content compliance rule that silently BCC’d matching messages to an attacker-controlled Gmail inbox.
Threat Actors
Malware
Vendors
Products
Google WorkspaceInstead of using obvious exfiltration tools, the attackers abused Google Workspace content compliance rules to silently copy sensitive email to an attacker-controlled inbox.REDCapA China-linked espionage cluster tracked as UNC6508 hid inside North American medical, academic, and military research networks for more than a year by exploiting REDCap servers and the INFINITERED backdoor.