
Hospital Cyberattacks Disrupt Patient Services, Bring Legal Fallout
Summary
Cyber incidents disrupted services at health systems in New Mexico and Ohio, prompting scam warnings and proposed litigation. The article also covers an $800,000 federal settlement tied to a 2023 ransomware attack at Lehigh Valley Health Network.
Key points
- A cyberattack at the University of New Mexico Health Sciences Center temporarily diverted ambulances from the state's only Level-1 trauma center and suspended some services; services and classes resumed by Wednesday.
- Threat actor Byod claimed it compromised 36,000 devices and accessed sensitive data at UNM. UNM has not publicly confirmed ransomware or patient-data theft.
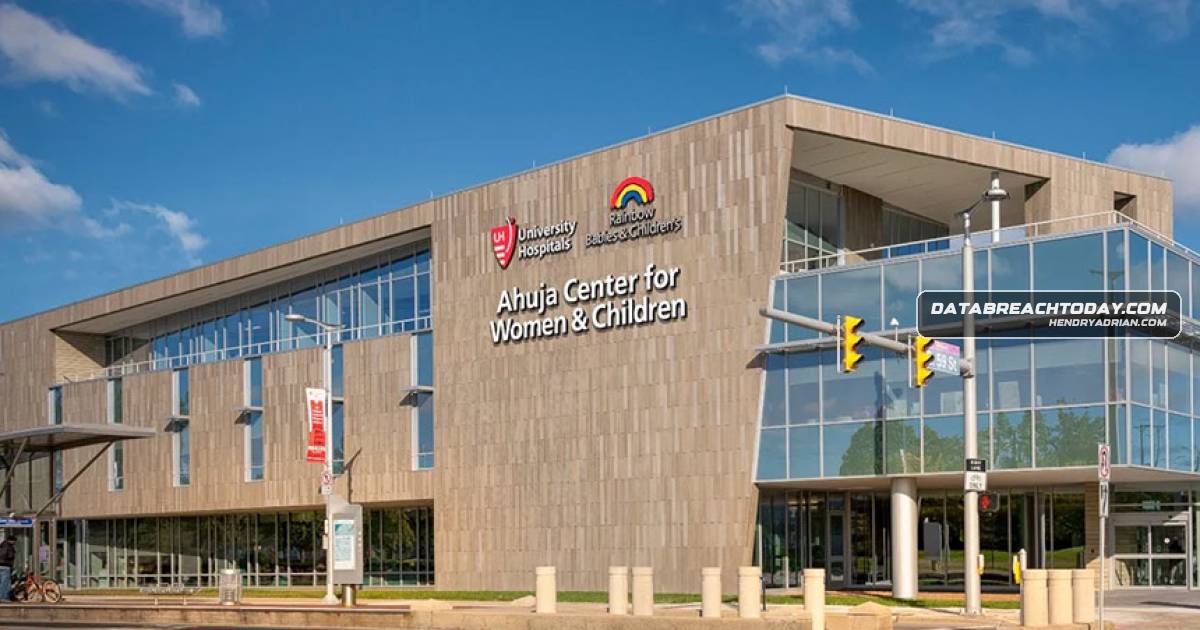
- University Hospitals in Ohio was restoring systems after an Oct. 22 incident that took MyChart offline and disrupted pre-authorizations and some appointments; it had not said whether patient data was compromised.
- Both health systems warned patients and others about potential scams following the incidents.
- Law firms announced investigations or proposed class action litigation related to the UNM and University Hospitals incidents.
- HHS reached an $800,000 settlement with Lehigh Valley Health Network over potential HIPAA violations related to a 2023 ransomware attack affecting more than 248,000 people; the agreement includes three years of federal monitoring.
Article Details
- Event Type
- Cyberattacks disrupting services at two U.S. university health systems, alongside ransomware-related HIPAA enforcement fallout.
- Impact
- The University of New Mexico Health Sciences Center temporarily diverted ambulances, suspended outpatient services, and canceled classes; it later said services and classes had resumed. Byod claimed it compromised 36,000 devices and accessed student, employee, and patient data, but UNM did not publicly confirm ransomware or patient-data theft. An incident at University Hospitals disrupted MyChart, insurance pre-authorizations, and some appointments and procedures; the system was still restoring services, and it had not said whether ransomware or patient-data compromise was involved. Both systems warned of potential scams. Separately, Lehigh Valley Health Network agreed to an $800,000 settlement over potential HIPAA violations following a 2023 ransomware attack; the article also reports a $65 million civil settlement related to that attack.
Threat Actors
ALPHVThe article identifies AlphV as another name for BlackCat, the ransomware group reported to have posted stolen examination photographs of breast cancer patients after the 2023 Lehigh Valley Health Network attack.BlackCatThe article identifies BlackCat as the ransomware group that posted stolen examination photographs of breast cancer patients after the 2023 Lehigh Valley Health Network attack; it also states that BlackCat is known as AlphV.BYODByod reportedly claimed responsibility for compromising 36,000 devices at UNM and accessing sensitive student, employee, and patient data. The claims were not publicly confirmed by UNM.