
ScarCruft Uses Fake Microsoft Alerts to Deliver NarwhalRAT
Summary
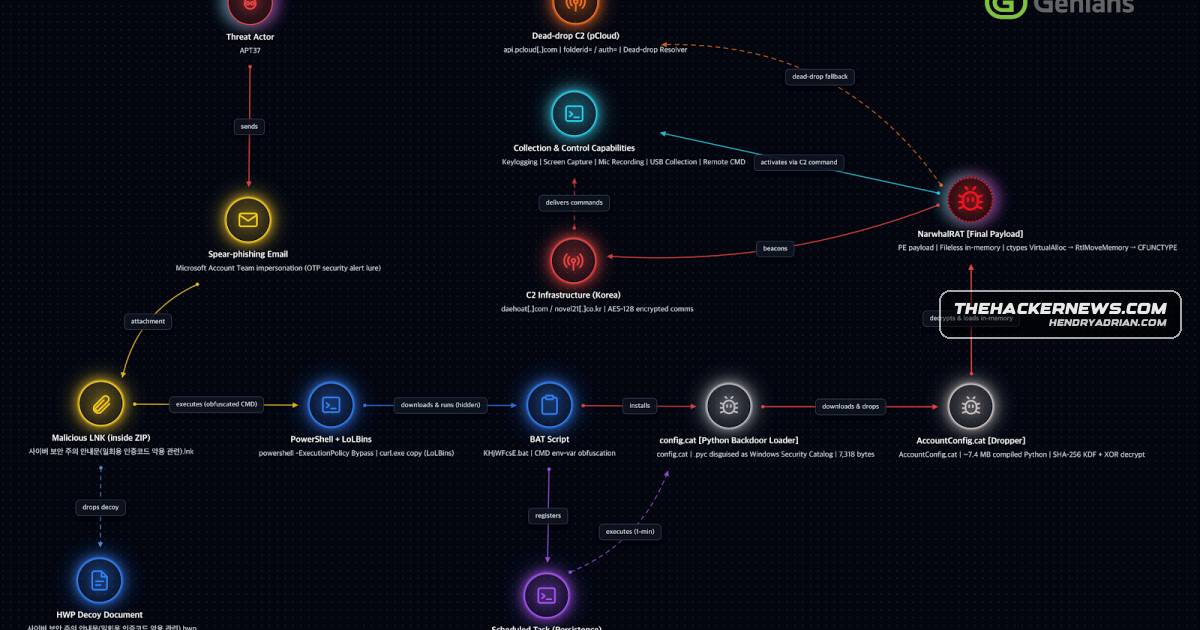
Genians reports that ScarCruft used fake Microsoft Account alerts to deliver NarwhalRAT via a ZIP containing a malicious LNK. The multi-stage infection uses in-memory execution, scheduled-task persistence, and Korean websites and pCloud for C2.
Key points
- Genians attributes the spear-phishing campaign to ScarCruft (APT37); the emails impersonated Microsoft Account security alerts and urged recipients to open an attachment.
- The attachment was a ZIP containing a malicious LNK, which starts a multi-stage infection chain using batch scripts, Python, and a CAT file.
- A scheduled task supports persistence; the CAT file fetches and runs the main payload in memory.
- NarwhalRAT can log keystrokes, capture screenshots, record ambient audio, collect system and directory data, and execute C2 instructions.
- The malware uses Korean websites and pCloud as C2 channels; Genians says the pCloud routines support a secondary channel using the service as a dead drop resolver.
- Genians says the activity resembles earlier ScarCruft Python-based attacks but marks a departure from the group’s previously associated RokRAT malware.
Article Details
- Attack Vectors
- Spear-phishing emails impersonate Microsoft Account security alerts and urge recipients to open a ZIP attachment containing a malicious LNK file.
- The LNK initiates a multi-stage chain using batch scripts, Python, and a CAT file to fetch and run NarwhalRAT in memory.
- A scheduled task launches the CAT file as a persistence mechanism.
- NarwhalRAT communicates through Korean websites and the pCloud cloud storage API as C2 channels.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | daehoat[.]com | Identified as a Korean website used as a primary C2 communication relay by NarwhalRAT. |
| DOMAIN | novel21[.]co[.]kr | Identified as a Korean website used as a primary C2 communication relay by NarwhalRAT. |
MITRE ATT&CK
T1005 · Data from Local SystemNarwhalRAT collects system data and uploads directory contents from the compromised host.T1025 · Data from Removable MediaNarwhalRAT gathers data from USB media.T1027 · Obfuscated Files or InformationThe report describes the downloaded batch script as obfuscated.T1041 · Exfiltration Over C2 ChannelThe malware sends collected information and command results back to its C2 server.T1053.005 · Scheduled TaskA scheduled task is created to launch the CAT file that fetches and runs the main payload.T1056.001 · KeyloggingNarwhalRAT can log keystrokes.T1059.003 · Windows Command ShellThe infection chain uses intermediary batch scripts, including an obfuscated batch script downloaded from a C2 server.T1059.006 · PythonThe malware uses Python, including a compiled Python script, in its multi-stage execution chain.T1082 · System Information DiscoveryThe malware collects system data from compromised hosts.T1102.001 · Dead Drop ResolverThe malware uses the pCloud API as a secondary C2 channel in a dead drop resolver arrangement.T1105 · Ingress Tool TransferThe infection chain downloads an obfuscated batch script, a Python executable, and a CAT file from remote infrastructure.T1113 · Screen CaptureNarwhalRAT can capture screenshots, including high-resolution images.T1123 · Audio CaptureNarwhalRAT can record ambient audio.T1204.002 · Malicious FileThe recipient is induced to open a ZIP attachment containing a malicious LNK file, which starts the infection chain.T1566.001 · Spearphishing AttachmentScarCruft used spear-phishing emails impersonating Microsoft Account security alerts to deliver a ZIP attachment.
Threat Actors
Malware
Products
Microsoft accountScarCruft (APT37) is using spear-phishing emails that impersonate Microsoft Account security alerts to trick victims into opening a ZIP file that launches a malicious LNK and installs NarwhalRAT.Naver WhaleThe hidden directory’s name is an attempt to evade detection by masquerading as Naver Whale, a web browser developed by South Korean tech company Naver Corporation.pCloudThe malware runs through a multi-stage, in-memory infection chain, collects sensitive data, and uses Korean websites plus pCloud as command-and-control channels.