
Aurora Claims Ransomware Data Theft at Diamond Truck Centres
Summary
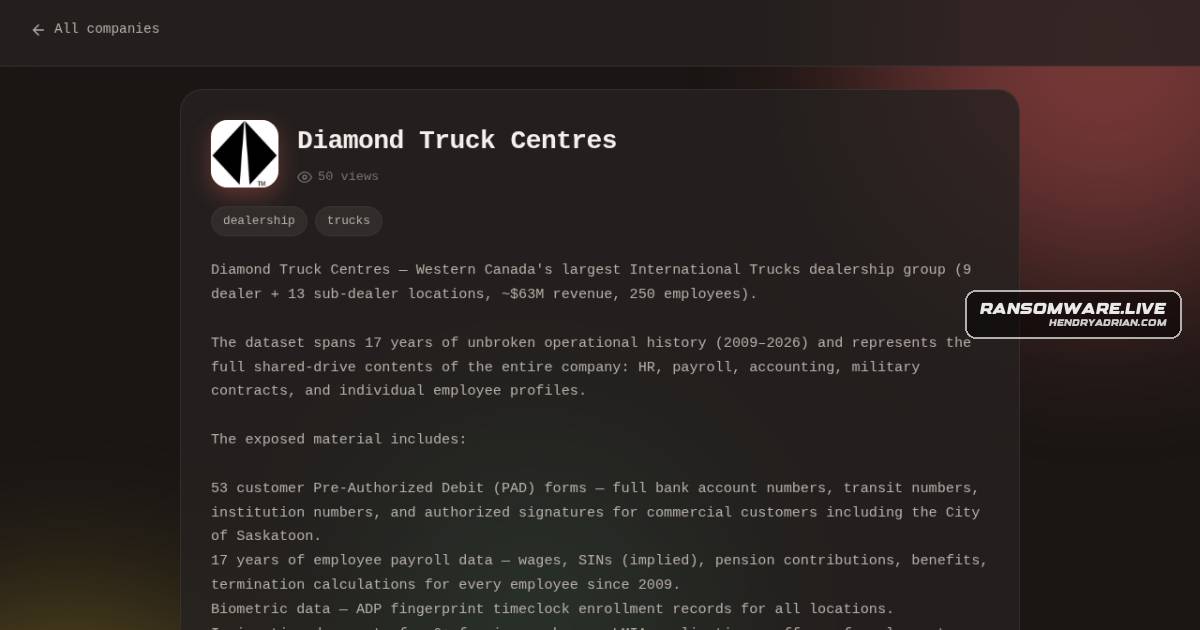
A ransomware.live record attributes to aurora claims that Diamond Truck Centres’ data was exposed, including payroll, customer banking, biometric, immigration, credential and military-contract information. The claims are unconfirmed.
Key points
- The record attributes the claims to aurora and links them to an actor leak-site post; ransomware.live monitored the listing.
- The post allegedly lists 17 years of shared-drive records, including employee HR, payroll and pension information.
- It claims customer banking details were exposed, including 53 PAD forms and 289 GB of bank-deposit scans.
- Other alleged data includes fingerprint timeclock enrollment records, immigration documents, plaintext access details and military-contract files.
- The source says the claims are unconfirmed and offers to share an official statement from Diamond Truck Centres if available.
Article Details
- Victim
- Diamond Truck Centres
- Encryption Status
- Unknown
- Exfiltration Status
- Unverified; the post describes data reportedly exposed based on public claims by aurora, but does not confirm exfiltration.
- Exfiltrated Data
- The post alleges exposure of HR and payroll records, biometric timeclock enrollment data, immigration documents, plaintext system access details, military contract and vehicle information, customer banking forms, bank deposit scans, and internal email. The claims are unverified.
- Ransom Demand
- Not disclosed
- Leak Status
- A public claim by aurora is reported; the source says it cannot confirm the information's accuracy and does not confirm that data was published.