
CYFIRMA Details Tax-Themed Campaign Delivering RAT-Like Malware
Summary
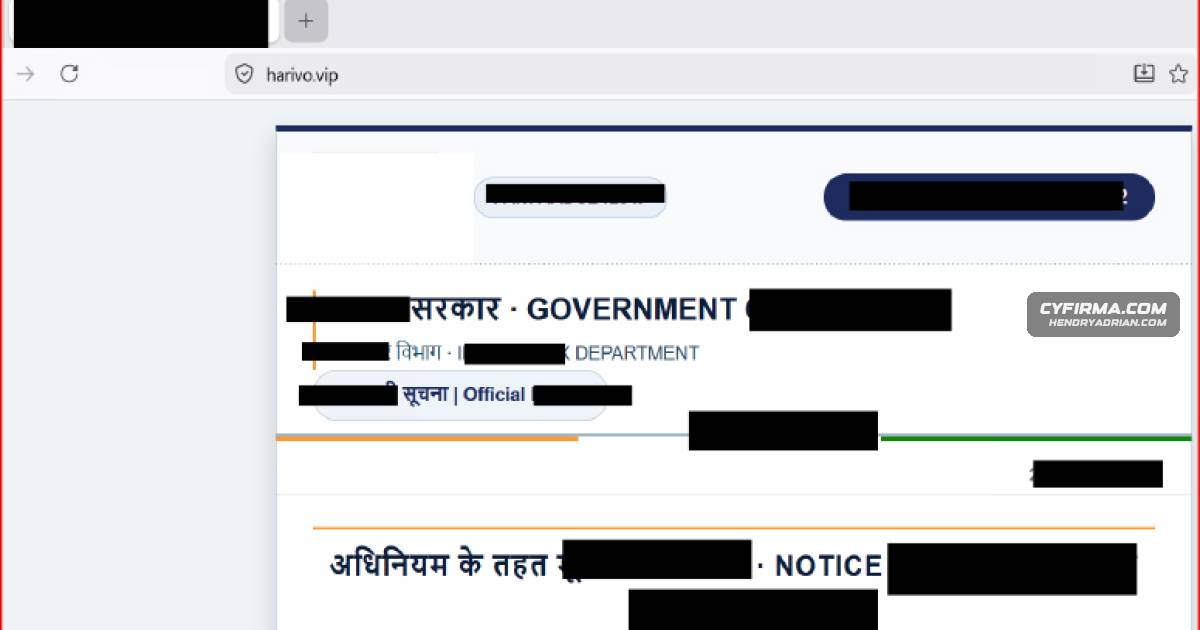
CYFIRMA analyzed a fake Indian Income Tax Department portal at harivo[.]vip that delivers a staged Windows malware payload. The report details obfuscation, persistence, RAT-like capabilities and encrypted C2; actor attribution remains unconfirmed.
Key points
- The report describes a fake Indian Income Tax Department assessment notice hosted on harivo[.]vip, used to lure users into downloading Tax_Assessment_0609.zip.
- The ZIP contains Tax_Assessment.img, which stages Tax_Assessment.exe and libsvcs.dll.
- Tax_Assessment.exe loads and executes libsvcs.dll using .NET reflection; both components are protected with ConfuserEx obfuscation.
- Analysis identified hidden execution, spoofed assembly metadata, registry changes and persistence mechanisms, including startup registration and scheduled tasks.
- The DLL has RAT-like capabilities, including host discovery, user activity monitoring, remote execution and encrypted C2 communication.
- The report identifies 103.231.12.27:4444 as hardcoded C2 infrastructure and says the observed behavior resembles XWorm; attribution to a specific actor is unconfirmed.
- Recommended defenses include restricting unknown executables from archives and disk images, monitoring suspicious DLL loading and persistence, and reviewing outbound connections to the reported infrastructure.
Article Details
- Publisher
- CYFIRMA
- Report Period
- 2026-06-23
- Scope
- Tax-themed malware campaign targeting users and organizations in India; Windows infection chain.
- Recommendations
- Use email and web security controls to block tax-themed phishing, monitor newly registered or low-reputation domains, and sandbox suspicious URLs and downloads.
- Restrict execution of unknown files delivered through archives and disk images, including from user-writable locations; use application allowlisting.
- Use endpoint detection to identify obfuscated binaries, reflection-based DLL loading, suspicious execution chains, and abnormal registry changes.
- Monitor outbound traffic for unusual encrypted connections, including activity to 103[.]231[.]12[.]27.
- Monitor autorun registry locations, startup folders, and scheduled tasks for unauthorized persistence; train users to verify tax notices through official portals.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | harivo[.]vip | Fraudulent tax-themed campaign domain used to lure victims into downloading the malware archive. |
| IPV4 | 103[.]231[.]12[.]27 | Hardcoded C2 server used by the campaign malware; communication is reported on port 4444. |
| IPV4 | 38[.]76[.]161[.]218 | Reported host for the fraudulent campaign domain harivo[.]vip. |
| MD5 | 3adcf5fca3f4fe23a9b73951e20d43bc | MD5 hash of the campaign's Tax_Assessment_0609.zip archive. |
| MD5 | ac08e8f463e0fa4a431b74fd5d7f01a1 | MD5 hash of the campaign's Tax_Assessment.exe loader. |
| MD5 | ba036fbf209b2dbdfec3fd3dee9b1798 | MD5 hash of the campaign's Tax_Assessment.img disk image. |
| MD5 | c0796f2ee614e1711d5355ee42dcbf62 | MD5 hash of the campaign's libsvcs.dll payload. |
| SHA256 | 372d7d8ca222e03afa5970848cf88efa6a3bc5146d20398601285fc7eaea6735 | SHA-256 hash listed as an IOC associated with the campaign malware. |
| SHA256 | 3fe29bf7e2c391d5405f8c6947cc42a6ec356fcf8455ce705dc23a156f5b450a | SHA-256 hash listed as an IOC associated with the campaign malware. |
| SHA256 | 4b5405d9acd00dd9225ffcec840a1752951be801d20ee1cab4ebde9ccd96916a | SHA-256 hash listed as an IOC associated with the campaign malware. |
| SHA256 | f5dc1016679f54f2be22da0ff6642046f7a943410c188514b96c28d8a3b95e12 | SHA-256 hash listed as an IOC associated with the campaign malware. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationConfuserEx obfuscation is used on the loader and DLL payload.T1033 · System Owner/User DiscoveryThe report describes collection of user information during reconnaissance.T1036 · MasqueradingThe campaign uses tax-document filenames and spoofed assembly metadata to appear legitimate.T1053.005 · Scheduled TaskScheduled-task persistence is reported among the malware's capabilities.T1082 · System Information DiscoveryThe payload gathers Windows and host information.T1112 · Modify RegistryThe malware modifies registry settings for stealth and persistence.T1140 · Deobfuscate/Decode Files or InformationThe report describes runtime decoding of protected assemblies.T1204.002 · Malicious FileThe user is prompted to download and open the malicious Tax_Assessment.exe file.T1497.001 · System ChecksThe report describes anti-analysis checks before execution.T1518.001 · Security Software DiscoveryThe payload enumerates security products.T1547.001 · Registry Run Keys / Startup FolderStartup registration and autorun changes are reported as persistence mechanisms.T1564.003 · Hidden WindowThe loader hides its console window during execution.T1573 · Encrypted ChannelThe malware uses an embedded encryption key for encrypted C2 communication.T1620 · Reflective Code LoadingTax_Assessment.exe loads libsvcs.dll using Assembly.LoadFrom() and reflection.
Malware
Products
Tools
ConfuserExThe malware uses ConfuserEx obfuscation, reflection-based DLL loading, persistence, and encrypted C2 traffic to support RAT-like control over Windows systems, with infrastructure tied to 103[.]231[.]12[.]27:4444.YARA[SHA-256 hashes ] YARA and IOC hashes associated with the campaign – 372d7d8ca222e03afa5970848cf88efa6a3bc5146d20398601285fc7eaea6735, f5dc1016679f54f2be22da0ff6642046f7a943410c188514b96c28d8a3b95e12, and 2 more hashes