
Researchers Find Dormant Remote JavaScript Injection Capability in Adblock for YouTube
Summary
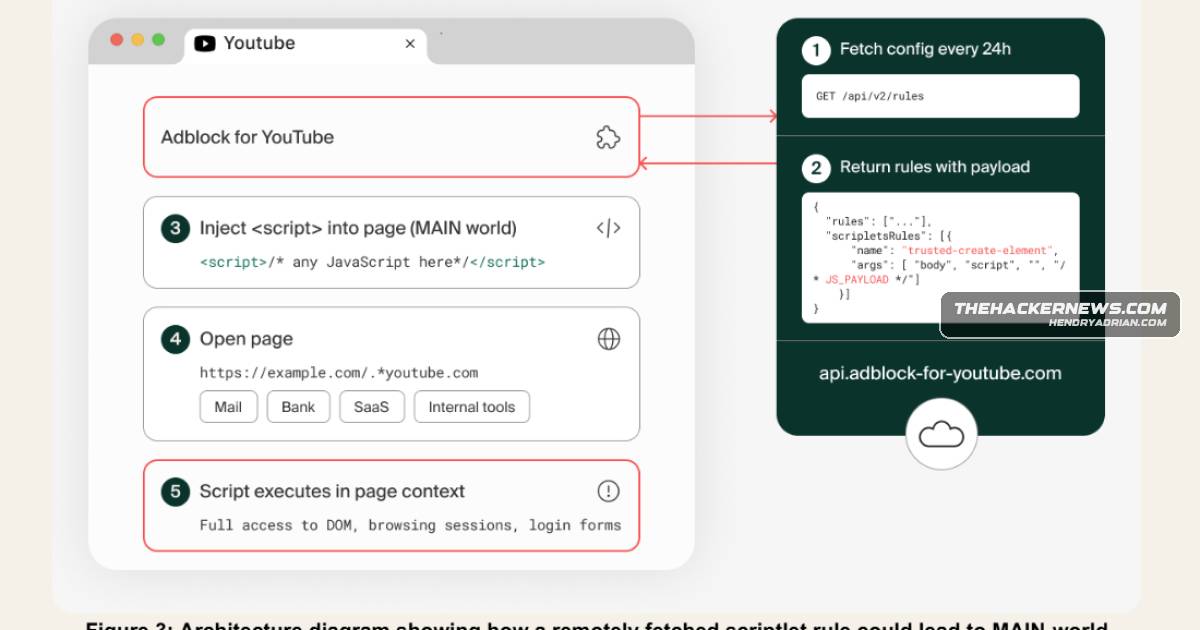
Island researchers found that Adblock for YouTube, installed by over 10 million users, could run arbitrary JavaScript on any website after a server-side change. No malicious payload was observed, but the dormant capability raises security and privacy concerns.
Key points
- Island researchers say a server-side configuration change could activate arbitrary JavaScript execution on any website, without an extension update or store review.
- The custom trusted-create-element scriptlet was inactive in the server response at the time of analysis; researchers reported no evidence of a malicious payload.
- Remote-controlled script injection paths have been present since February 2025; an earlier version included Unistream SDK, which was removed in June 2024.
- The extension’s YouTube check looks for youtube.com anywhere in the URL rather than validating the hostname or frame origin, making the check bypassable.
- The article says related extensions were removed from the Chrome Web Store for malware.
Article Details
- Event Type
- Security research disclosure of a dormant remote JavaScript-injection capability in the Adblock for YouTube Chrome extension.
- Impact
- The extension has more than 10 million installs and can reportedly be configured through a server-side change to execute arbitrary JavaScript on websites without an extension update or store review. Researchers said the capability was dormant at the time of analysis, and no malicious payload had been observed. The capability could expose sensitive browsing data and sessions; related extensions were removed from the Chrome Web Store for malware.
People
Products
Adblock for ChromeRelated extensions such as Adblock for Chrome, Adblock for You, and AdBlock Suite were removed from the store.Adblock for YouRelated extensions such as Adblock for Chrome, Adblock for You, and AdBlock Suite were removed from the store.Adblock for YouTubeResearchers found that the Adblock for YouTube Chrome extension, with over 10 million installs, can be configured to execute arbitrary JavaScript code on any website through a server-side change.AdBlock SuiteRelated extensions such as Adblock for Chrome, Adblock for You, and AdBlock Suite were removed from the store.Google ChromeResearchers found that the Adblock for YouTube Chrome extension, with over 10 million installs, can be configured to execute arbitrary JavaScript code on any website through a server-side change.Unistream SDKEarly iterations of the extension were found to ship with an ad-injection software development kit (SDK) named Unistream SDK, although it was removed in June 2024.