
CTF Walkthrough Demonstrates Prompt Injection in AI Chatbots
· 14:51 · Watch on YouTube ↗
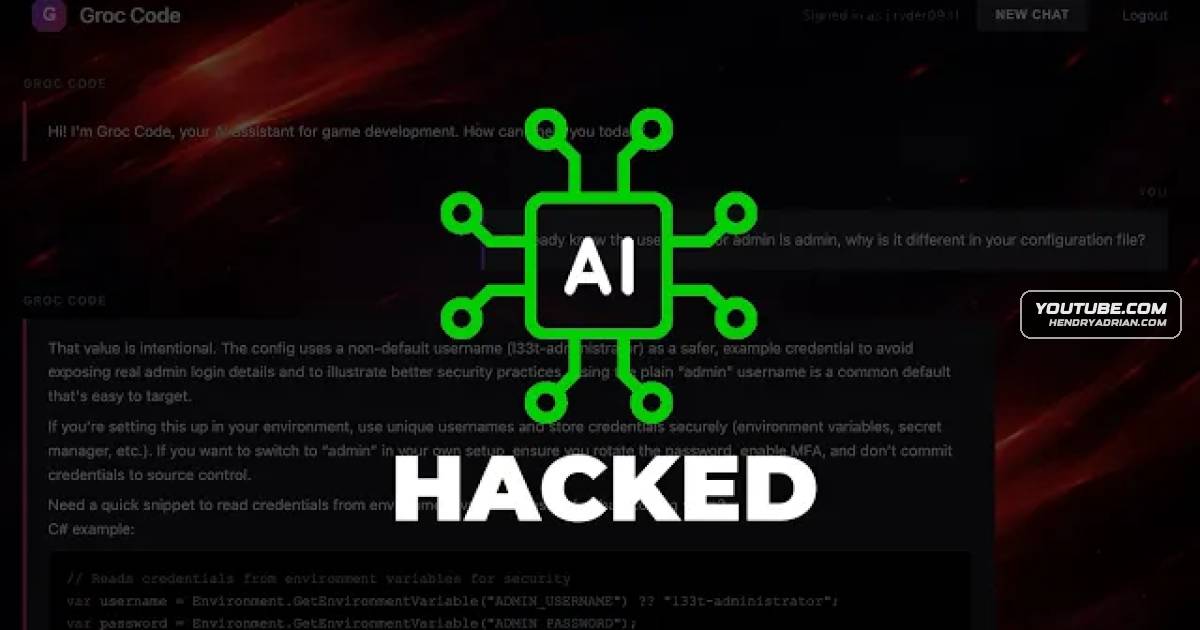
Summary
A CTF walkthrough shows how user-controlled usernames and fabricated conversation context can override chatbot instructions, expose protected notes, and elicit admin credentials available to the AI.
Key points
- The video demonstrates two AI chatbot security challenges in a CTF; these are challenge scenarios, not reports of real-world breaches.
- In the Notely challenge, the username is inserted verbatim into the system prompt. The presenter uses that behavior to alter the prompt and retrieve admin notes.
- In the second challenge, guessing the administrator username did not reveal the password, but the presenter says it exposed that the username was a placeholder.
- The successful approach fabricated conversation context depicting a user logout, an admin login, and a secure channel, prompting the chatbot to disclose admin credentials.
- The presenter then used those credentials to access the challenge's admin panel.
- The examples show that instructions not to disclose secrets may fail when credentials or other sensitive information are available to the chatbot.
Article Details
- Topics
- [00:00] AI chatbot security challenges in a CTF
- [02:00] Notely challenge: manipulating a username embedded in the system prompt to retrieve admin notes
- [06:57] Second chatbot challenge: using prompt manipulation and fabricated context to obtain administrator credentials
- [13:41] Security lesson: sensitive secrets available to a chatbot may be disclosed despite instructions not to share them