
Bug Bounty Career Lessons From More Than $2 Million in Earnings
· 15:10 · Watch on YouTube ↗
Summary
The speaker recounts earning more than $2 million through bug bounties and shares career lessons: specialize in vulnerability classes, collaborate, learn to read code, use AI thoughtfully, rest to avoid burnout, and share methods strategically.
Key points
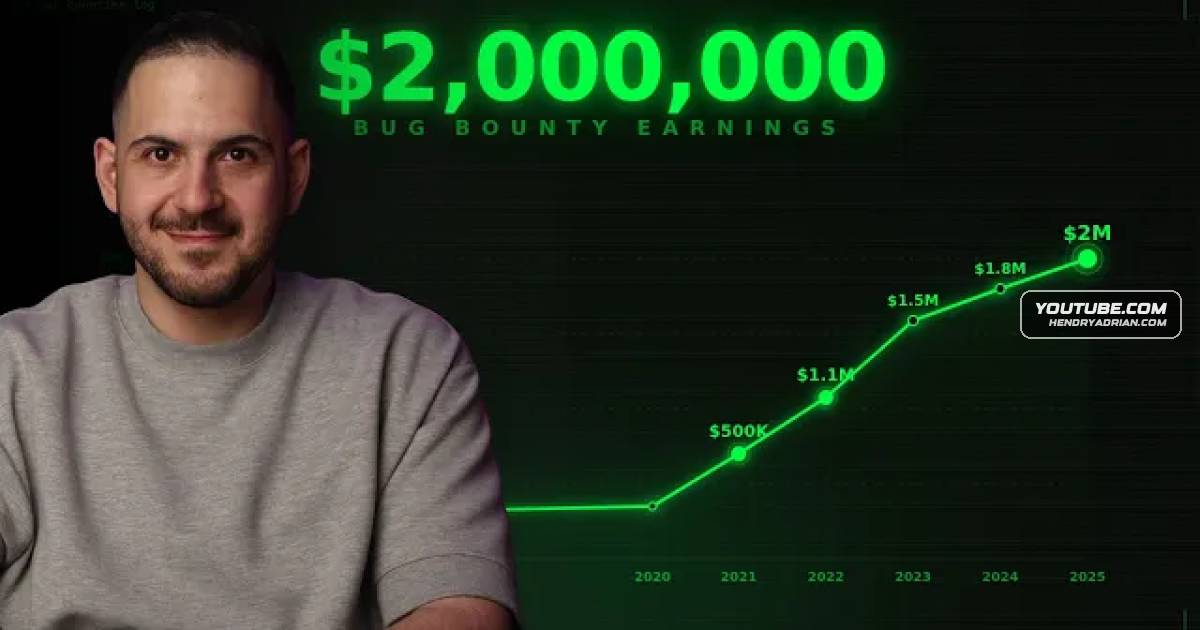
- The speaker says bug bounties earned them more than $2 million and became a full-time career.
- They advise concentrating on a specific target and vulnerability class rather than spreading effort across many targets; examples include SQL injection, blind XSS, SSRF, IDOR and API hacking.
- The speaker credits collaboration with improving their work and describes partnering with Ziad on Airbnb bug bounty research.
- They recommend learning to read code and using AI to brainstorm and suggest testing ideas; they also note that AI is helping developers improve.
- The speaker describes burnout during 2019–2022 and recommends taking breaks to return to bug hunting refreshed.
- They advise sharing methods strategically, after making the most of a technique, because others may learn from and adopt them.
- After losing a job in 2022, the speaker committed to bug bounty work full-time and emphasizes setting goals and staying accountable.
Article Details
- Topics
- [00:00] Bug bounty earnings and career background
- [01:33] Finding motivation and building a bug bounty career
- [03:15] Specializing in vulnerability classes and studying targets
- [05:15] Collaboration and community in bug bounty work
- [08:14] Burnout, breaks, and adapting bug-hunting methods
- [09:05] Learning to read code and using AI in bug bounty workflows
- [13:02] Going full-time after a job loss and setting goals