
Flipper Zero Demonstration Shows a Wi-Fi Deauthentication Attack
· 3:55 · Watch on YouTube ↗
Summary
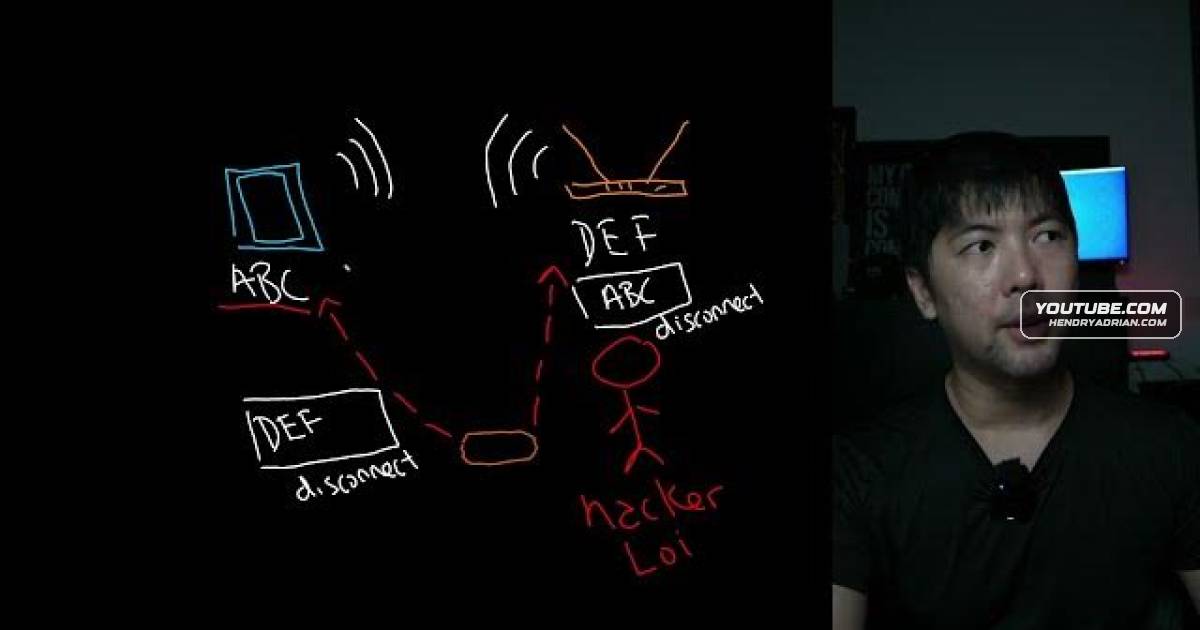
The video demonstrates using Flipper Zero with an ESP32 and Wi-Fi Marauder to disconnect a mobile device from a Wi-Fi access point, then explains how forged messages impersonating device MAC addresses cause disconnection.
Key points
- The presenter scans nearby Wi-Fi networks and selects a target access point.
- Using Flipper Zero with an ESP32 and Wi-Fi Marauder, the presenter launches a deauthentication attack.
- The demonstrated mobile device disconnects from the access point and cannot reconnect while the attack is running.
- The presenter explains that the attack sends disconnection messages impersonating the MAC addresses of the access point and mobile device.