
AWS Security Lake Tutorial Demonstrates Athena Queries and OpenSearch Dashboards
· 16:13 · Watch on YouTube ↗
Summary
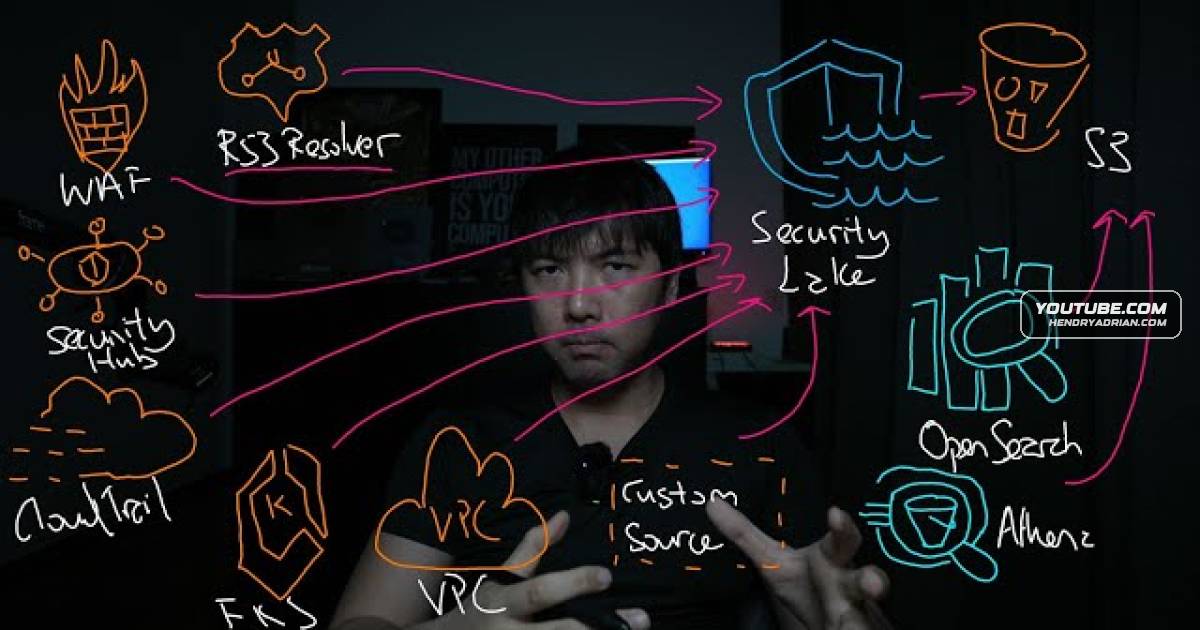
The presenter demonstrates how AWS Security Lake collects OCSF-formatted logs, then uses Athena for investigation and OpenSearch for direct querying and dashboards to support security monitoring, threat hunting, and incident response.
Key points
- The presenter explains that security monitoring must process logs from varied endpoints, servers, applications, databases, and network devices, often requiring ETL to normalize data for analysis.
- Amazon Security Lake can ingest AWS telemetry and custom sources, storing the logs in S3 in OCSF format.
- The demonstration covers configuring data sources, regions, and subscribers, with S3 or Lake Formation access methods for controlled access across accounts.
- Athena queries can inspect Security Lake data; the presenter demonstrates filtering web application firewall records to investigate an unspecified IP address and request activity.
- OpenSearch can connect to Security Lake for direct queries and visualizations; the walkthrough covers setting up permissions and a role.
- CloudTrail and web application firewall dashboards show event trends and filters that can support monitoring, threat hunting, investigation, and incident response.
Article Details
- Topics
- [00:05] Diverse security-log formats and OCSF normalization
- [01:14] Security monitoring ETL, correlation, and anomaly detection
- [03:38] AWS Security Lake data sources and standardized S3 storage
- [05:45] Configuring sources, subscribers, regions, and account access
- [09:42] Athena queries for investigating Security Lake data
- [11:59] Connecting OpenSearch for direct queries
- [14:01] CloudTrail and WAF dashboards for event visualization