
SafePay Claims Caritas Koblenz in an Unverified Ransomware Listing
Summary
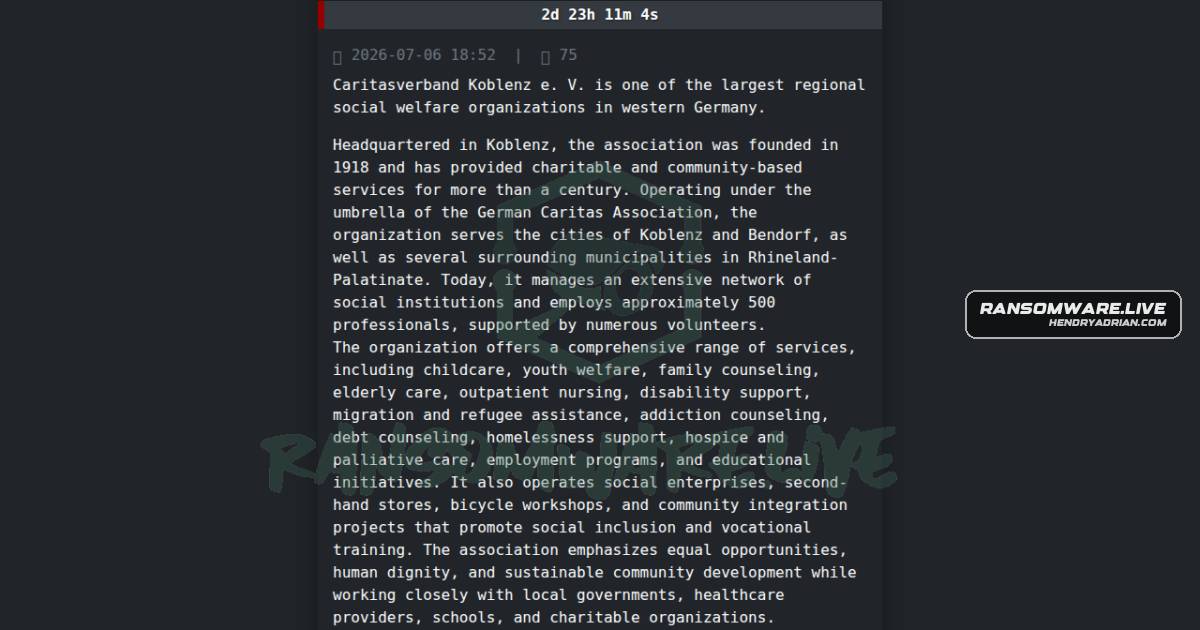
A monitoring entry lists Caritas Koblenz in Germany as a SafePay ransomware claim, citing the group's blog. The post says the claim has not been independently confirmed.
Key points
- The entry identifies Caritas Koblenz in Germany as the claimed victim and SafePay as the ransomware actor.
- The claim is attributed to SafePay's blog; the monitoring post says its accuracy cannot be confirmed.
- The record gives discovery and publication timestamps of July 6, 2026.
- The entry labels the victim's sector as healthcare but provides no evidence confirming compromise or details of impact.
Article Details
- Victim
- caritas-koblenz.de
- Victim Domain
- caritas-koblenz.de
- Claim Date
- 2026-07-06
- Encryption Status
- Unknown; the source does not confirm encryption.
- Exfiltration Status
- Unknown; the source does not confirm exfiltration.
- Exfiltrated Data
- Unknown
- Ransom Demand
- Unknown
- Leak Status
- The source reports a SafePay group claim but does not report a data leak or publication; the claim is unverified.