
Explaining the Seven Phases of the Cyber Kill Chain
· 6:56 · Watch on YouTube ↗
Summary
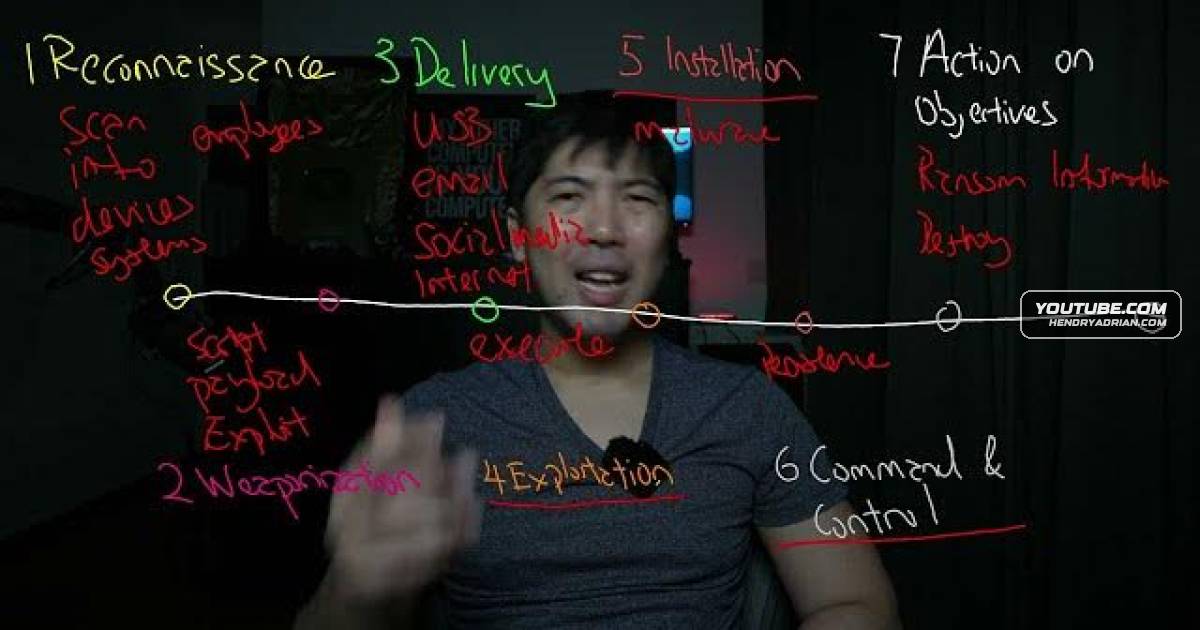
The video presents a seven-phase framework for understanding ethical hacking, using hypothetical examples of reconnaissance, payload delivery, exploitation, persistence and attackers’ objectives.
Key points
- The presenter describes reconnaissance as gathering information about an organization, its systems, services, devices and employees.
- Weaponization involves preparing tools or a payload, with malicious macros in a document given as a hypothetical example.
- Delivery examples include USB devices, phishing messages and sending a payload to a vulnerable web server.
- The exploitation phase is described as executing malicious code by taking advantage of an unpatched service, vulnerability or misconfiguration.
- The video describes persistence as retaining access after a user removes a program or executable.
- Possible objectives include ransomware, disrupting services and collecting organizational data; these are presented as examples, not reported incidents.
Article Details
- Topics
- [00:00] Overview of the Cyber Kill Chain as a structured way to understand hacking phases
- [01:02] Reconnaissance and gathering information about an organization
- [02:20] Weaponization and preparing tools or malicious payloads
- [03:03] Delivery methods including USB devices, phishing and internet-facing services
- [04:35] Exploitation through vulnerabilities, unpatched systems or misconfigurations
- [05:28] Persistence and maintaining access
- [05:49] Actions on objectives: ransomware, disruption or data collection