
SafePay Claims rtngmbh.de as Ransomware Victim
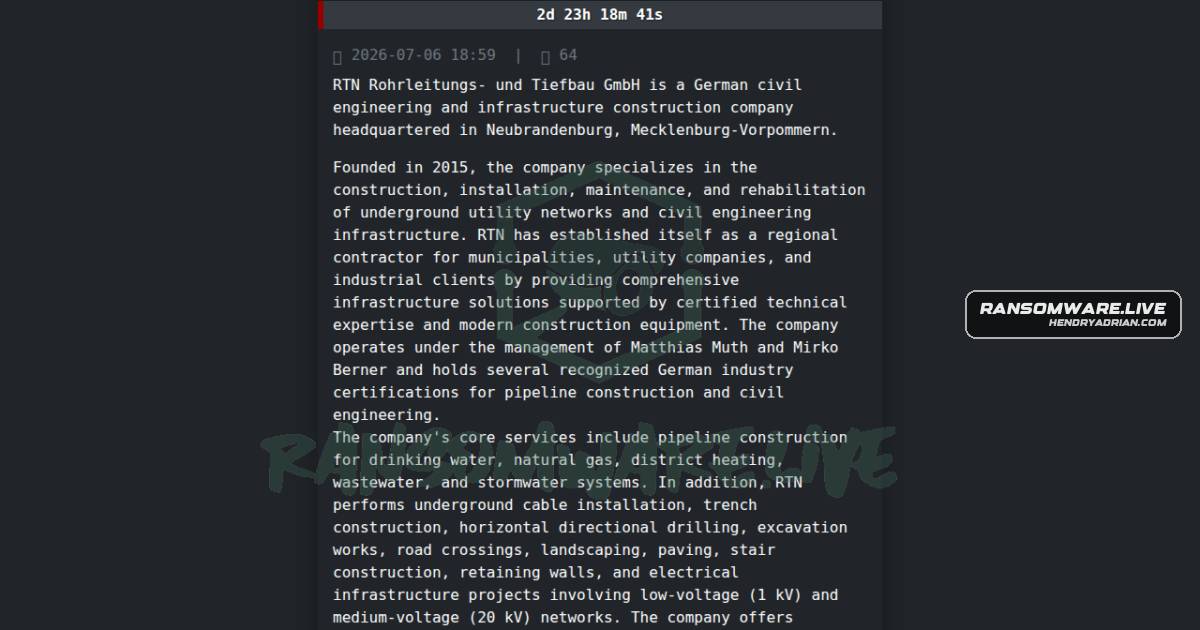
Summary
SafePay's leak-site post names rtngmbh[.]de in Germany as a ransomware victim. The monitoring record says the claim is unconfirmed; compromise, disruption, and data impact are not independently verified.
Key points
- The record attributes a ransomware claim naming rtngmbh[.]de to SafePay.
- The cited source is a SafePay onion-site post: hxxp://safepaypfxntwixwjrlcscft433ggemlhgkkdupi2ynhtcmvdgubmoyd[.]onion/blog/post/rtngmbhde/.
- The claim was published and discovered on July 6, 2026.
- The article describes disruption and encryption or threatened access to data, but says the information is based on the group's public claim and cannot be confirmed.
Article Details
- Victim
- rtngmbh.de
- Victim Domain
- rtngmbh.de
- Claim Date
- 2026-07-06
- Encryption Status
- The article says the group claimed ransomware activity that encrypted data or threatened access to it; this is unconfirmed.
- Encrypted Size
- Not disclosed
- Exfiltration Status
- Not disclosed
- Exfiltrated Data
- Not disclosed
- Exfiltrated Size
- Not disclosed
- Ransom Demand
- Not disclosed
- Leak Status
- The claim was listed on safepay's blog; publication of victim data is not confirmed.
Threat Actors
Countries
Industries
business servicesSector: Business ServicesCivil engineeringFounded in 2015, the company focuses on construction, installation, maintenance, and rehabilitation of underground utility networks and civil engineering, and the incident impacted #GermanyConstructionFounded in 2015, the company focuses on construction, installation, maintenance, and rehabilitation of underground utility networks and civil engineering, and the incident impacted #Germany