
XSS Tutorial Demonstrates Session Hijacking and Credential Harvesting
· 9:48 · Watch on YouTube ↗
Summary
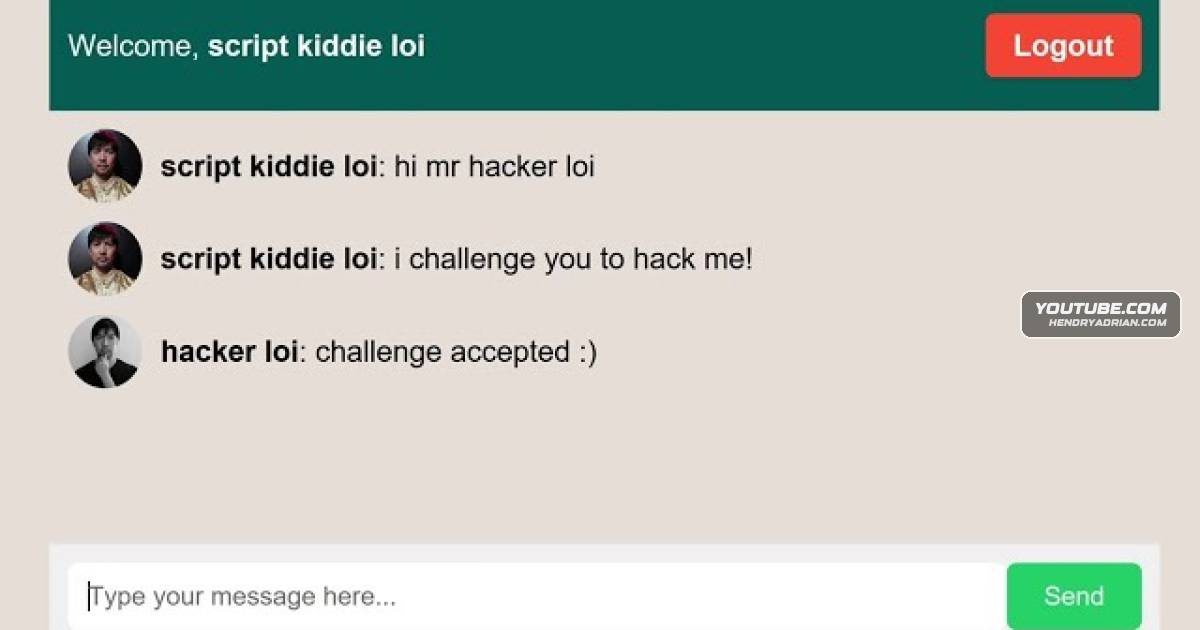
The tutorial demonstrates cross-site scripting in a chat app, using injected JavaScript to redirect users, capture session cookies, impersonate a user, and send credentials to a fake login page.
Key points
- The presenter explains how user-submitted content can allow injected scripts to execute for other visitors.
- A JavaScript payload redirects visitors from the demonstrated chat app.
- The tutorial shows capturing a PHP session cookie and changing browser storage to impersonate another user.
- The presenter uses the Social Engineering Toolkit to create a fake Google login page and demonstrate credential capture.
- The video shows sample XSS payloads and advises that hacking requires permission.