
Cross-Site Request Forgery Demo Shows How Hidden Forms Abuse Logged-In Sessions
· 6:24 · Watch on YouTube ↗
Summary
A tutorial demonstrates how a deceptive link can trigger a logged-in user’s browser to submit a message through a hidden form, then shows how JavaScript can automate submission and how to inspect the resulting request.
Key points
- The presenter explains that a victim’s existing session can be used to perform actions on a website when they follow a deceptive link.
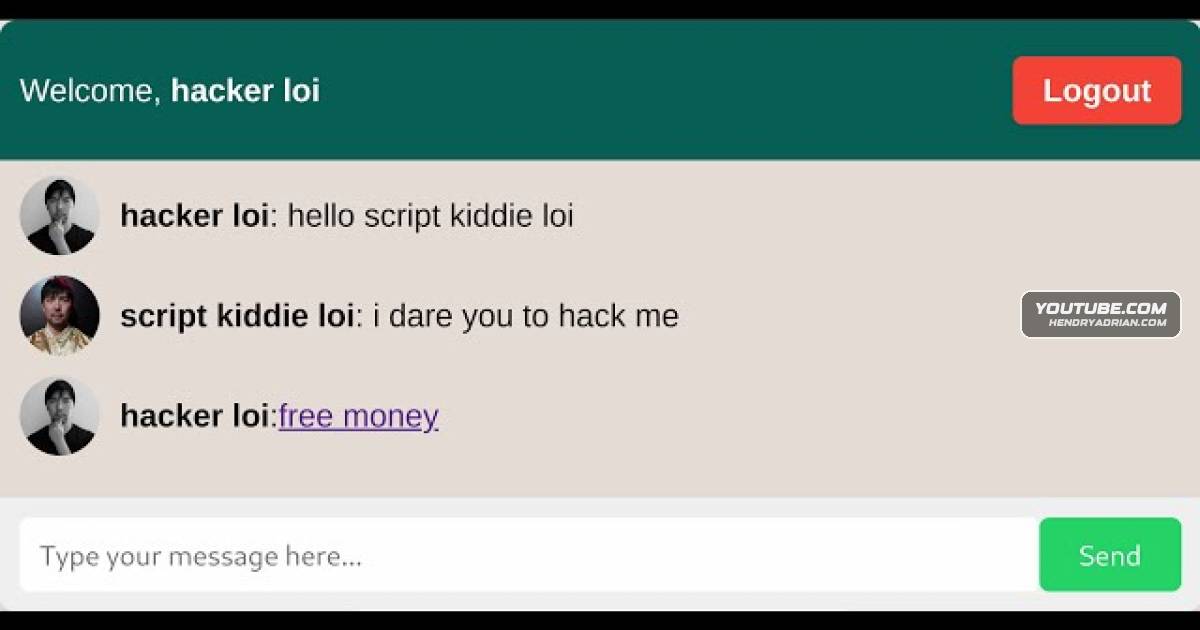
- A demonstration uses a fake prize page and a messaging application to submit a message as a logged-in test account.
- The initial form requires the user to click a button; added JavaScript automatically submits the form when the page loads.
- The presenter inspects the browser’s network activity to show the POST request and submitted message.
Article Details
- Topics
- [00:00] How CSRF can use a logged-in session to trigger website actions
- [01:14] Demonstration setup using a messaging application and test accounts
- [02:00] Creating and hosting a deceptive page with a hidden form
- [04:16] Automating form submission when the page loads
- [05:34] Inspecting the submitted POST request in browser network tools