
U.S. Army Secures Two Subdomains After 404-Page Defacements
Summary
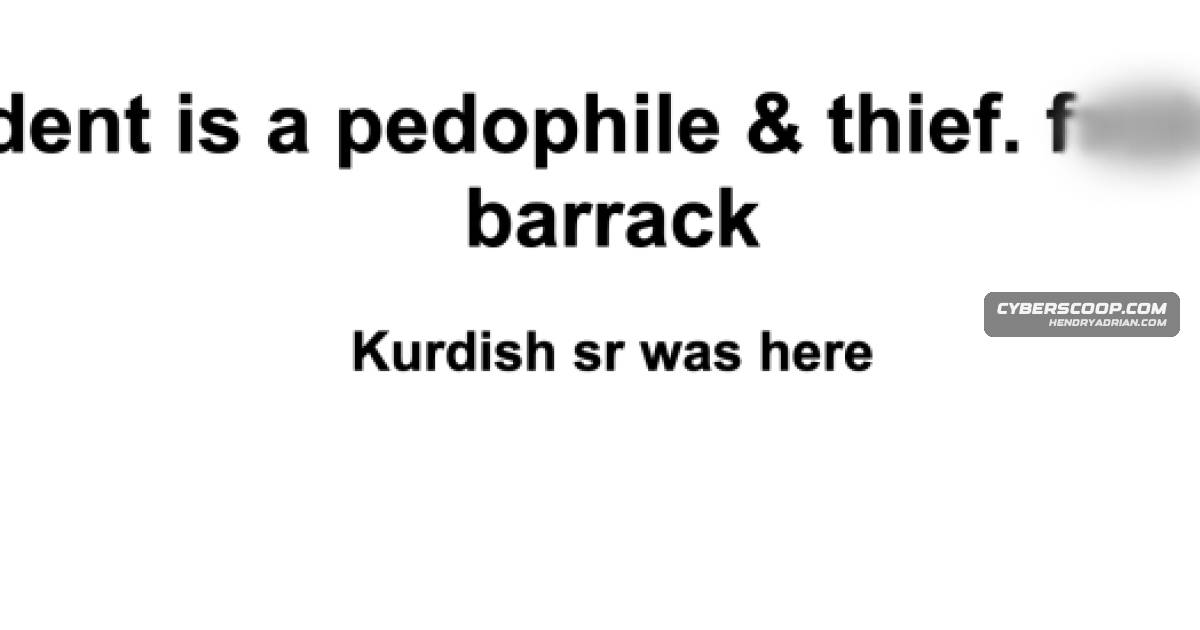
The Army confirmed unauthorized defacements of error pages on oil[.]army[.]mil and ai2c[.]army[.]mil. The pages, hosted on a legacy third-party platform, were secured as Army investigators continue examining the incident.
Key points
- The Army confirmed unauthorized defacements on error pages for oil[.]army[.]mil and ai2c[.]army[.]mil; the pages have been secured.
- The error pages displayed pro-Kurdistan messages and insults targeting President Donald Trump and Ambassador Tom Barrack.
- The Army said the affected pages were hosted on a legacy third-party platform not connected to its enterprise network.
- Cybersecurity researcher Ronald Lovelace discovered the defacements and alerted Army officials and CyberScoop.
- The Army’s incident response is ongoing; how the defacements occurred, how long they lasted, and whether other subdomains were affected remain unclear.
- The article describes 404 hijacking as altering the content shown on missing-page errors, potentially leaving a site's other pages apparently unaffected.
Article Details
- Victim Organization
- U.S. Army
- Victim Domain
- army.mil
- Incident Type
- 404 hijacking and website defacement affecting Army subdomains
- Operational Impact
- The affected pages were taken offline, removed, and secured. The Army said incident response was ongoing; broader effects beyond the website defacements were unclear.
- Claim Status
- confirmed
MITRE ATT&CK
People
Vendors
Products
Countries
Industries
DefenseThe Army takes all cyber incidents seriously and is actively investigating this matter to enforce our strict cyber defense and network security standards.”GovernmentThe Kurdish separatist movement has fought for decades to establish an independent nation, and defacing government websites has long been a popular tactic among Kurdish hacktivists.