
SpaceBears Claims Fitcrunch Ransomware Incident
Summary
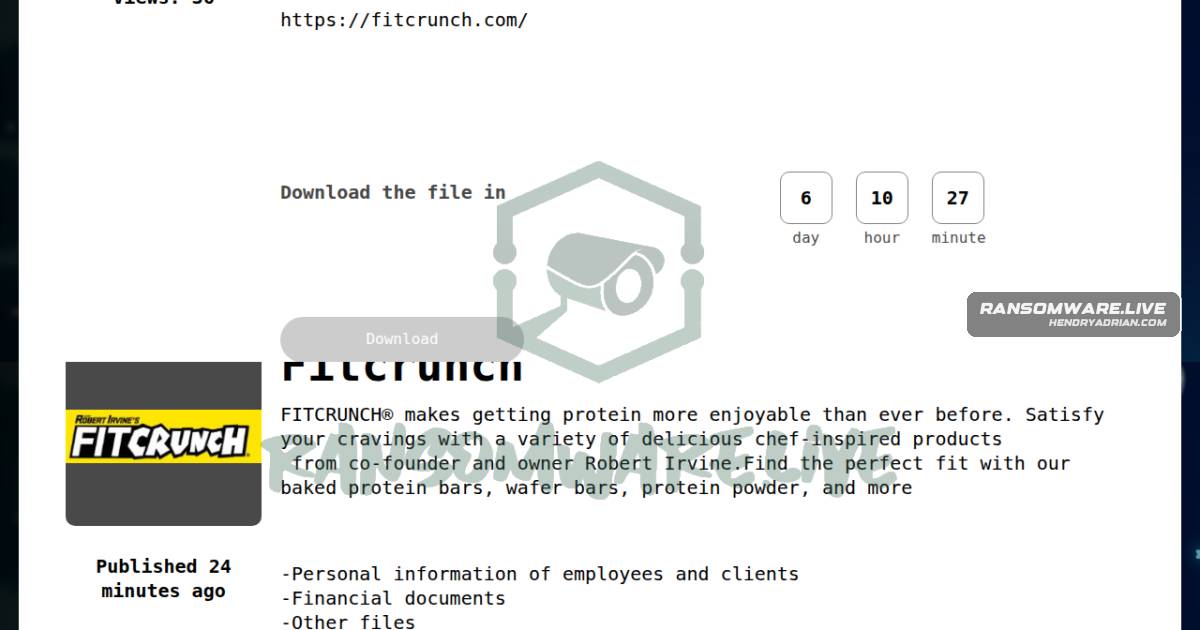
SpaceBears reportedly claims it targeted Fitcrunch and says personal information, financial documents and other files were affected. The claim is unconfirmed.
Key points
- The record identifies Fitcrunch in the US as the named victim and SpaceBears as the actor.
- The claim is attributed to the group's leak site and monitored by ransomware.live.
- The group reportedly claims personal information, financial documents and other files were affected; the author says the claims cannot be confirmed.
Article Details
- Victim
- Fitcrunch
- Claim Date
- 2026-06-25
- Encryption Status
- Unverified; the report says encryption or theft may have occurred but does not establish encryption.
- Exfiltration Status
- Unverified; the report says encryption or theft may have occurred but does not establish exfiltration.
- Exfiltrated Data
- The report attributes claims of employee and client personal information, financial documents, and other files to the ransomware group; authenticity and exfiltration are unconfirmed.
- Leak Status
- The group’s listing is cited, but publication of data is not established.