
AWS Security Hub Demonstrates Correlated Exposure Findings and Potential Attack Paths
· 5:00 · Watch on YouTube ↗
Summary
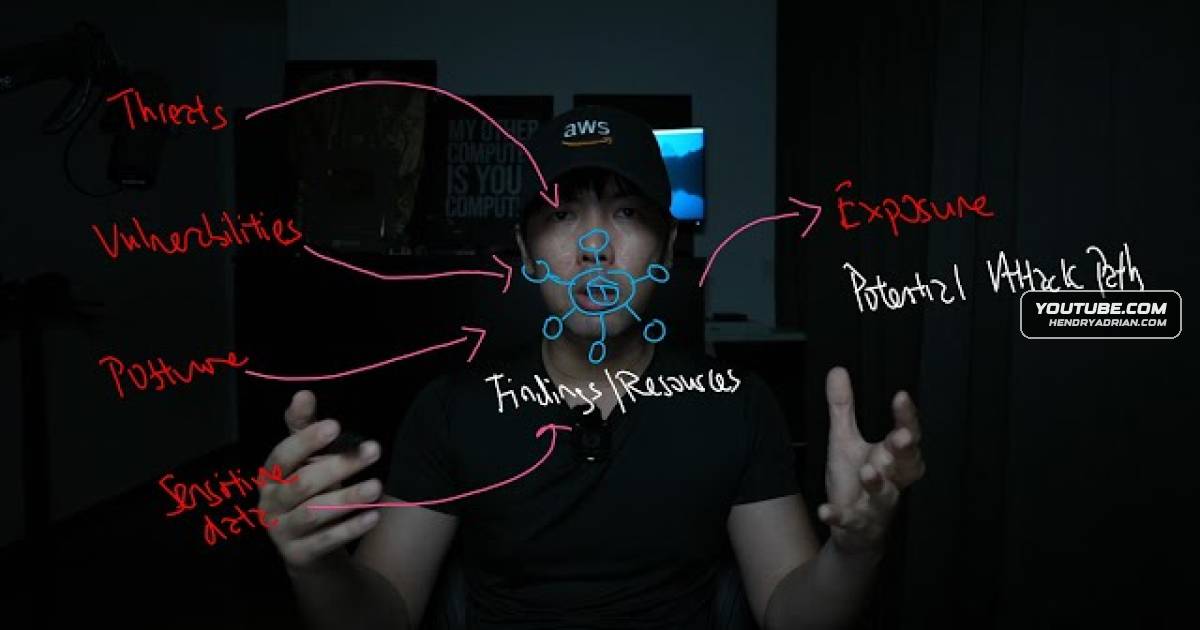
A walkthrough shows AWS Security Hub correlating security findings into potential attack paths, including a vulnerable EC2 instance with excessive IAM permissions, and illustrates how to investigate and remediate the exposure.
Key points
- The demonstration shows Security Hub combining findings from threat detection, vulnerability management, posture management, and sensitive-data discovery.
- Exposure findings correlate vulnerabilities, misconfigurations, and other signals to help prioritize investigation before reviewing individual findings.
- A demonstrated finding describes a potentially credential-stealing EC2 instance with software vulnerabilities and an administrative instance profile; it is presented as a potential risk, not a confirmed compromise.
- The attack-path view maps related resources, including a VPC, subnet, EC2 instance, and network interface, to support investigation.
- The example reveals excessive IAM permissions, including S3 full access and IAM full access; the presenter recommends removing unused access and tightening permissions.
Article Details
- Topics
- [00:00] Security Hub and connected security services
- [00:57] Correlating findings into potential exposure paths
- [02:15] Investigating a potentially credential-stealing EC2 finding
- [02:50] Following the attack-path topology across cloud resources
- [03:41] Reviewing excessive IAM permissions and remediation