
Amazon Inspector Tutorial Demonstrates Vulnerability Scanning and Remediation
· 12:55 · Watch on YouTube ↗
Summary
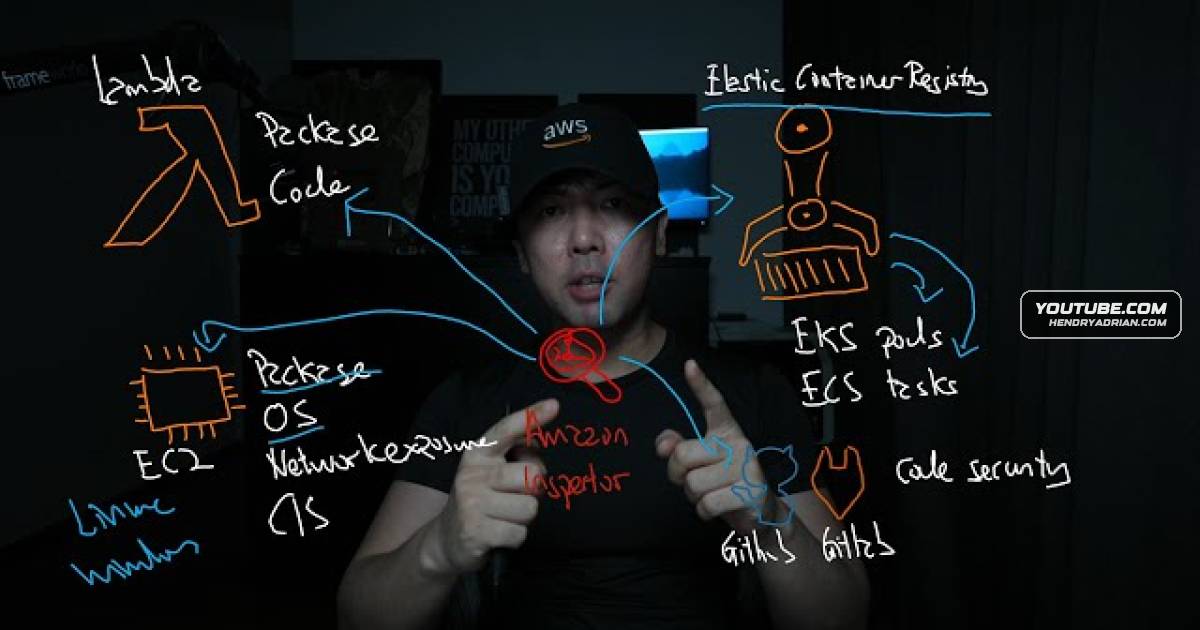
The tutorial demonstrates Amazon Inspector’s vulnerability management across Lambda, EC2, container images and code repositories, showing how to prioritize findings, inspect vulnerable code and packages, remediate issues, and search for CVEs.
Key points
- The video presents Amazon Inspector as a way to scan Lambda functions, EC2 instances, container images, and code repositories for package and code vulnerabilities.
- Its dashboard highlights critical findings and findings with available exploits or fixes to help prioritize remediation.
- The tutorial shows an ECR image being pushed and then appearing in Inspector findings.
- Examples of Lambda findings include excessive privileges, AWS credentials logged in code, and potentially unsafe use of user input in Python commands.
- The video demonstrates a suggested remediation approach: validate user-supplied input used in Python subprocess and OS command functions.
- Inspector’s vulnerability database search is shown as a way to find affected resources for a searched CVE.
Article Details
- Topics
- [00:00] Amazon Inspector and supported workload scanning
- [01:42] Dashboard coverage and prioritizing critical findings
- [03:05] Finding details and vulnerability intelligence
- [05:37] EC2 and container image findings and scan workflow
- [09:57] Lambda package and code findings with remediation
- [12:00] Searching the vulnerability database for affected resources