
Spacebears Claims Biessse Data in Ransomware Listing
Summary
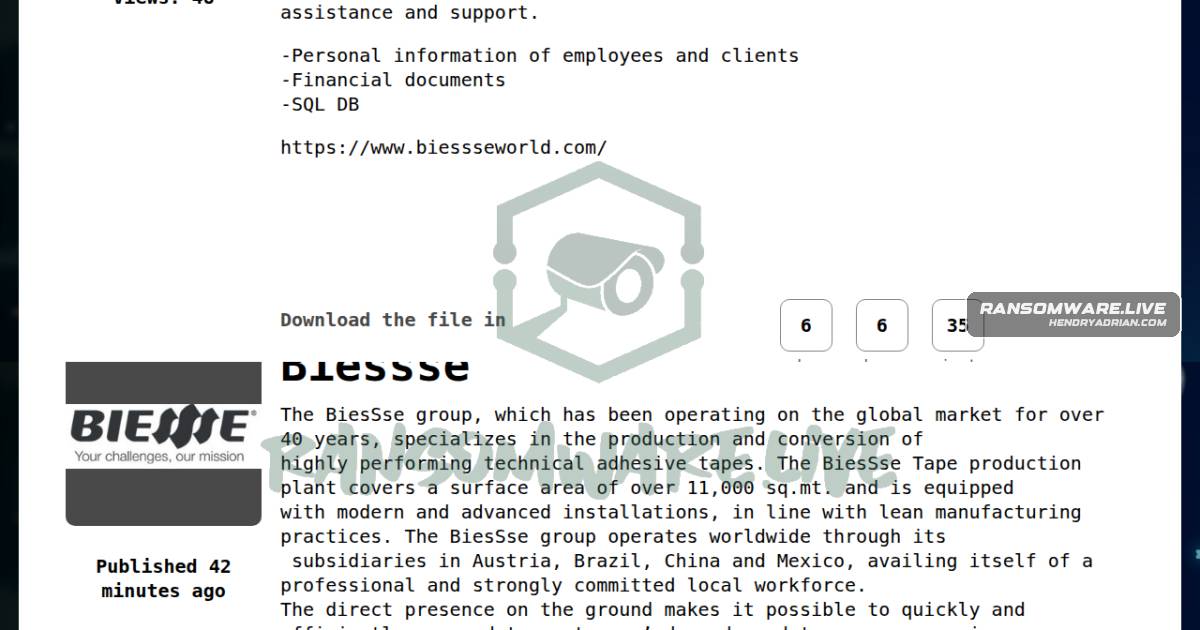
Ransomware.live reports that spacebears claims access to Biessse employee and client personal information, financial documents, and an SQL database. The claim is unconfirmed.
Key points
- The record identifies Biessse as the claimed victim and spacebears as the ransomware actor.
- The group allegedly claims access to employee and client personal information, financial documents, and an SQL database.
- The claim is attributed to a spacebears listing and monitored by ransomware.live.
- The article says the incident impacted Italy but provides no independent confirmation; the author says the claim’s accuracy cannot be confirmed.
Article Details
- Victim
- Biessse
- Victim Domain
- Not disclosed
- Attack Date
- 2026-07-08
- Claim Date
- 2026-06-09
- Encryption Status
- Not disclosed
- Encrypted Size
- Not disclosed
- Exfiltration Status
- Claimed; unverified
- Exfiltrated Data
- The group claimed access to personal information of employees and clients, financial documents, and an SQL database. The source says the claim could not be confirmed.
- Exfiltrated Size
- Not disclosed
- Ransom Demand
- Not disclosed
- Leak Status
- Not disclosed